What "javascript:document.vulnerable=true" Actually Is
The string javascript:document.vulnerable=true is not a product, model number, or technology standard. It is a fragment of JavaScript code — specifically, a script payload that can appear in a cross-site scripting (XSS) attempt. Attackers sometimes inject strings like this into web forms, URL parameters, or stored content. If a browser or web application executes it, the script simply sets a property called vulnerable on the page's document object. On its own it does nothing harmful — it is typically used as a harmless proof-of-concept marker by security researchers and penetration testers to demonstrate that script injection is possible on a page. The real risk is not this specific line of code, but the fact that a site allowed it to run at all.
Why Script Injection Matters for Industrial and Embedded Systems
On a traditional office PC, an XSS flaw is serious but usually contained to a browser session. On an industrial computer, thin client, or all-in-one PC running a kiosk, HMI, or point-of-sale application, the stakes are different. These devices often run unattended, display web-based dashboards, and connect to operational technology (OT) networks. If a browser-based interface on such a device can be tricked into executing injected scripts, an attacker could potentially read session tokens, alter displayed data, or pivot toward other systems on the same network.
Practical Mitigations
Protecting deployments against script injection is mostly a software and configuration discipline, not a hardware one:
| Layer | Recommended Measure |
|---|---|
| Application | Escape and validate all user input; use a Content Security Policy (CSP) header |
| Browser | Disable unnecessary extensions; run kiosk mode with a locked-down profile |
| Operating System | Apply security updates promptly; use a standard (non-admin) user account |
| Network | Segment OT devices from general IT and internet traffic |
| Device | Choose hardware that supports long-term OS patching and a stable, supported platform |
A Content Security Policy that disallows inline scripts is one of the most effective single defences, because it stops injected javascript: payloads from executing even if they reach the page.
Choosing Hardware That Supports a Secure Lifecycle
Security is only as good as the platform underneath it. Devices that receive regular firmware and OS updates, run current operating systems such as Windows 11 Pro or a maintained Linux distribution, and offer predictable long-term availability make it far easier to keep patches current. Fanless industrial PCs are particularly well suited to kiosk and control-room roles because they tolerate dust, heat, and continuous operation without moving parts to fail.
Thinvent Products for Secure, Always-On Deployments
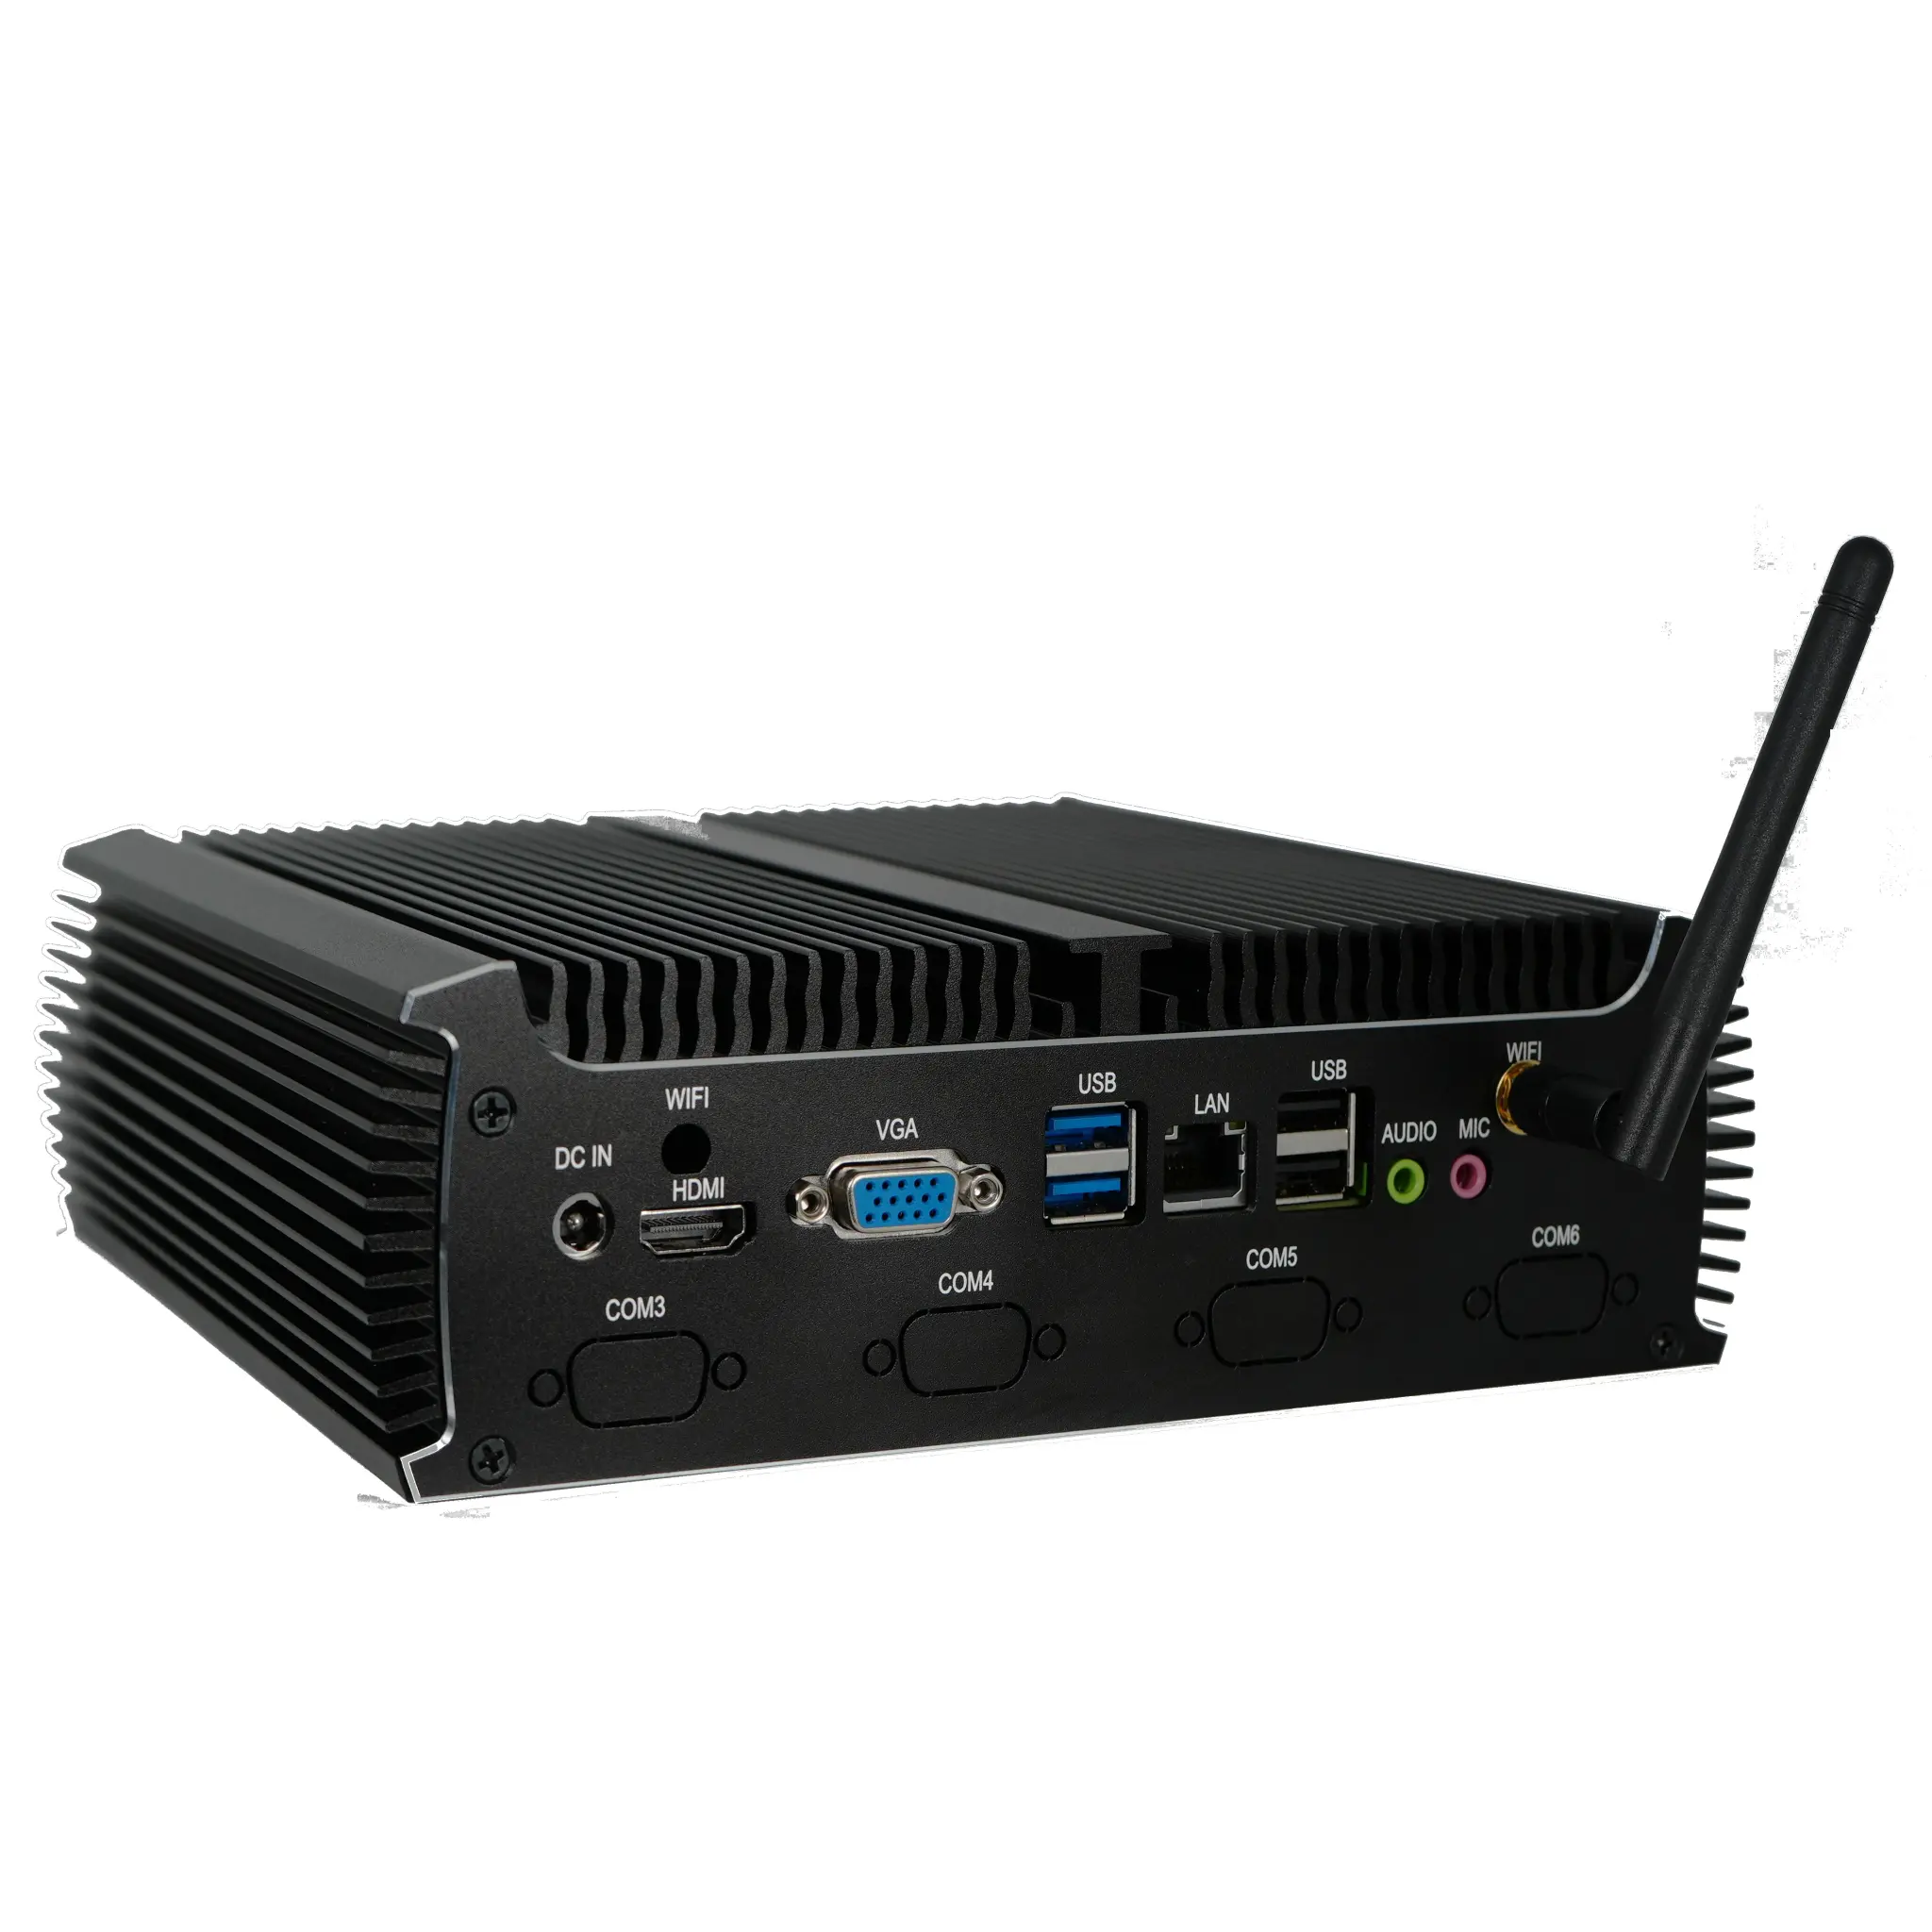
Thinvent's industrial computers, mini PCs, thin clients, and all-in-one PCs are built for exactly these environments. The IPC3 series, for example, pairs an Intel® Core™ i3-1215U processor (6 cores, up to 4.4 GHz, 10 MB cache) with 16 GB DDR4 RAM and up to 1 TB SSD storage, and is available with Windows 11 Professional, Windows 11 IoT Value, DOS, or Thinux™ Embedded Linux — so you can standardise on a platform you can patch and control. Quad DB9 serial options support legacy industrial equipment, while fanless operation keeps these systems running quietly and reliably in kiosks, control rooms, and shop floors. Thinvent's range gives integrators a consistent, updatable hardware base for secure, locked-down deployments worldwide.