What is a Trusted Platform Module (TPM)?
A Trusted Platform Module (TPM) is a dedicated microcontroller designed to secure hardware through integrated cryptographic keys. It provides a hardware-based root of trust for the system, enabling secure generation, storage, and management of sensitive data like encryption keys, digital certificates, and passwords. Unlike software-based security, a TPM chip is physically isolated on the motherboard, making it highly resistant to software attacks and tampering. This technology is a critical component for implementing robust security standards and is widely adopted in enterprise and industrial computing environments.
Key Specifications and Security Features
A TPM chip offers several core security functions. Its primary role is secure cryptographic key generation and storage, ensuring private keys never leave the protected environment of the chip. It enables platform integrity measurement by creating a hash of critical startup components (like BIOS/UEFI, OS loader), which can be verified to detect unauthorized changes. TPMs also facilitate secure boot processes, device authentication, and hardware-bound disk encryption (e.g., with BitLocker). Modern TPMs adhere to standards like TPM 2.0, which supports stronger algorithms and more flexible authorization policies compared to the older TPM 1.2 specification.
Applications and Use Cases
TPM security is essential across various demanding sectors. In industrial automation and IoT, it secures device identity and ensures firmware integrity for operational technology (OT) networks. For digital signage and kiosks, it protects against malware and unauthorized OS modifications. In finance and point-of-sale (POS) systems, TPMs are used to securely process transactions and protect sensitive customer data. Healthcare applications rely on TPMs to safeguard patient data in compliance with regulations like HIPAA. Furthermore, TPM is a fundamental requirement for running modern operating systems like Windows 11 in a secure configuration.
Thinvent Products with TPM Security
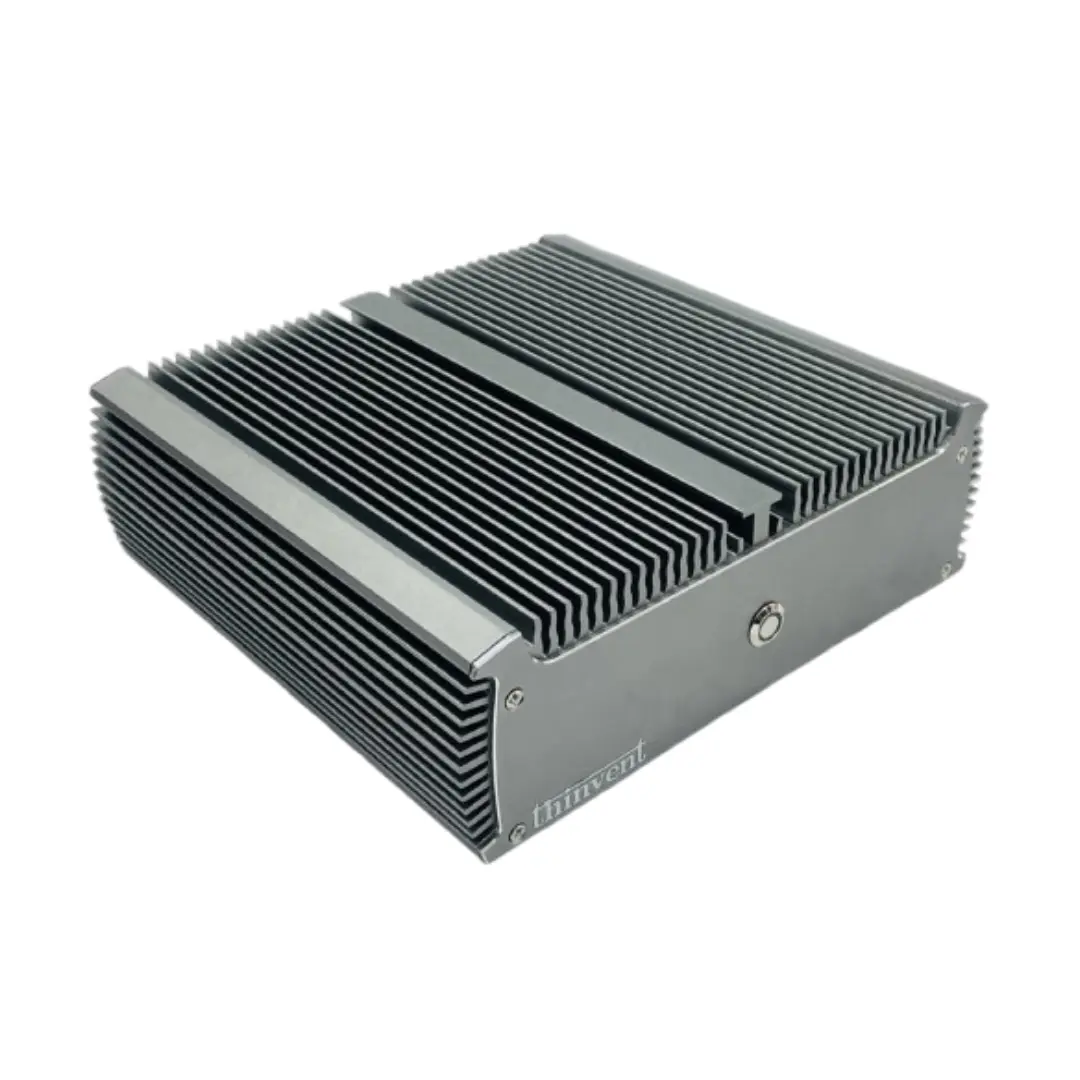
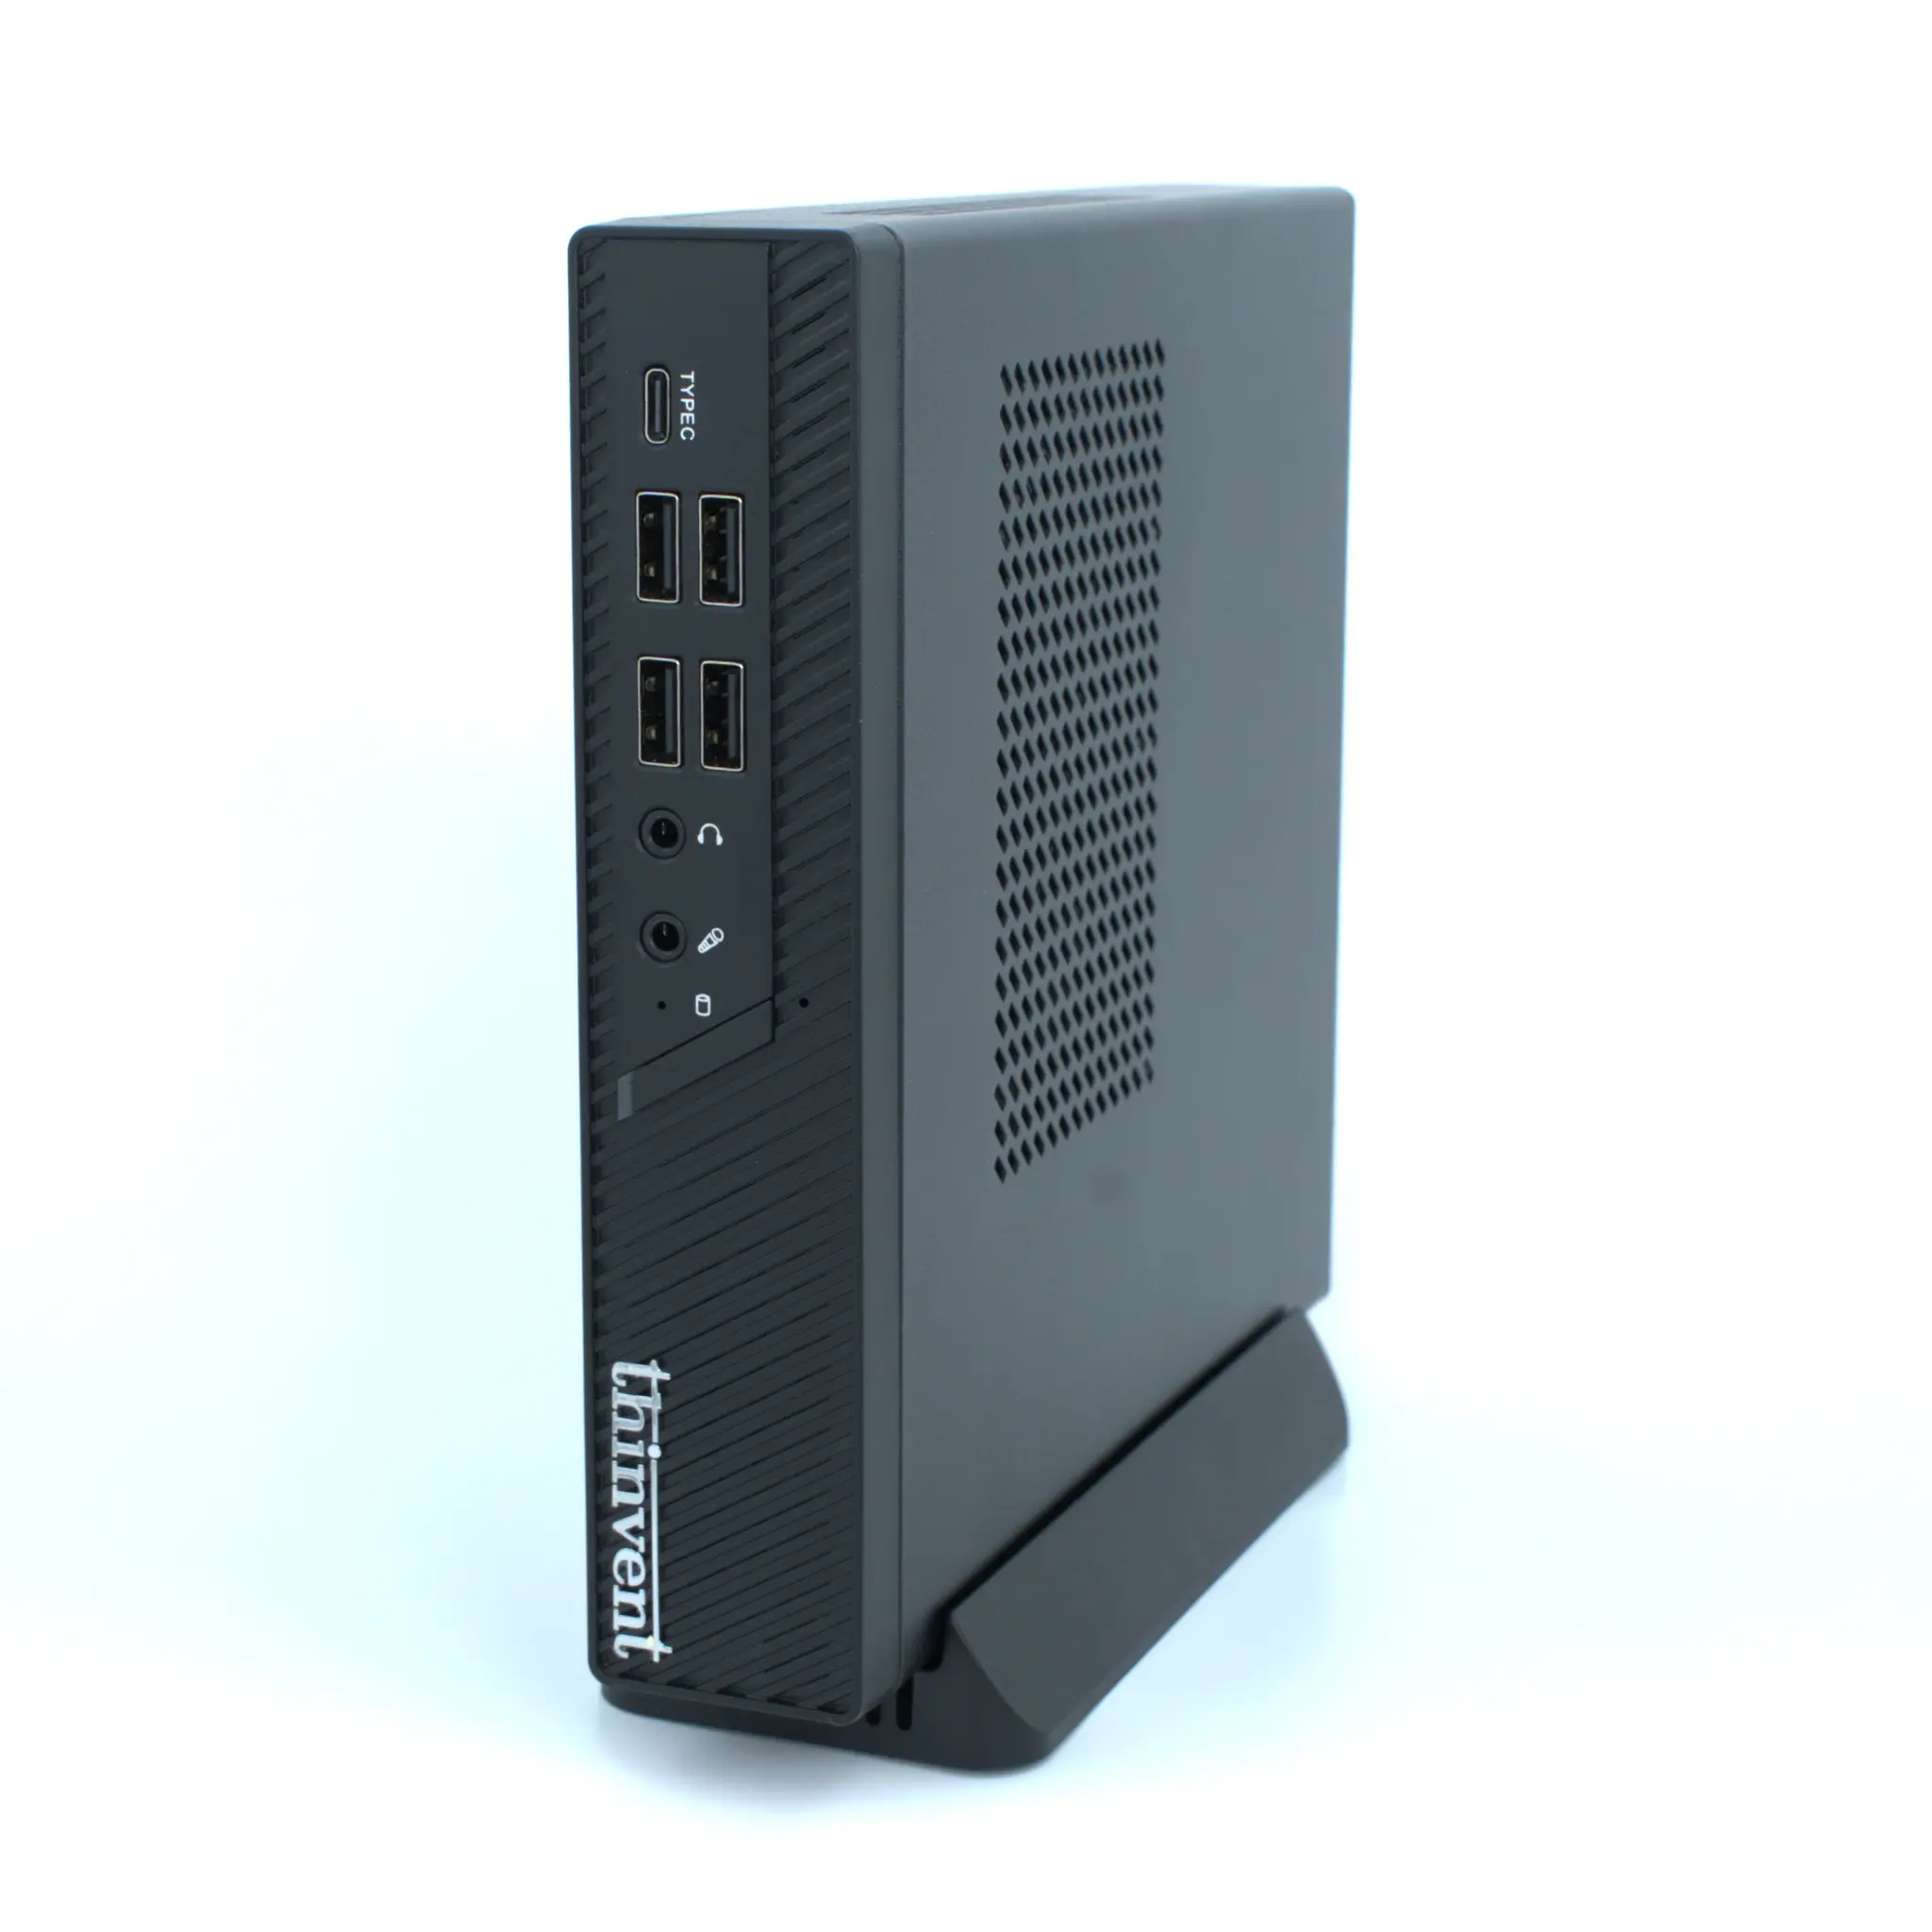
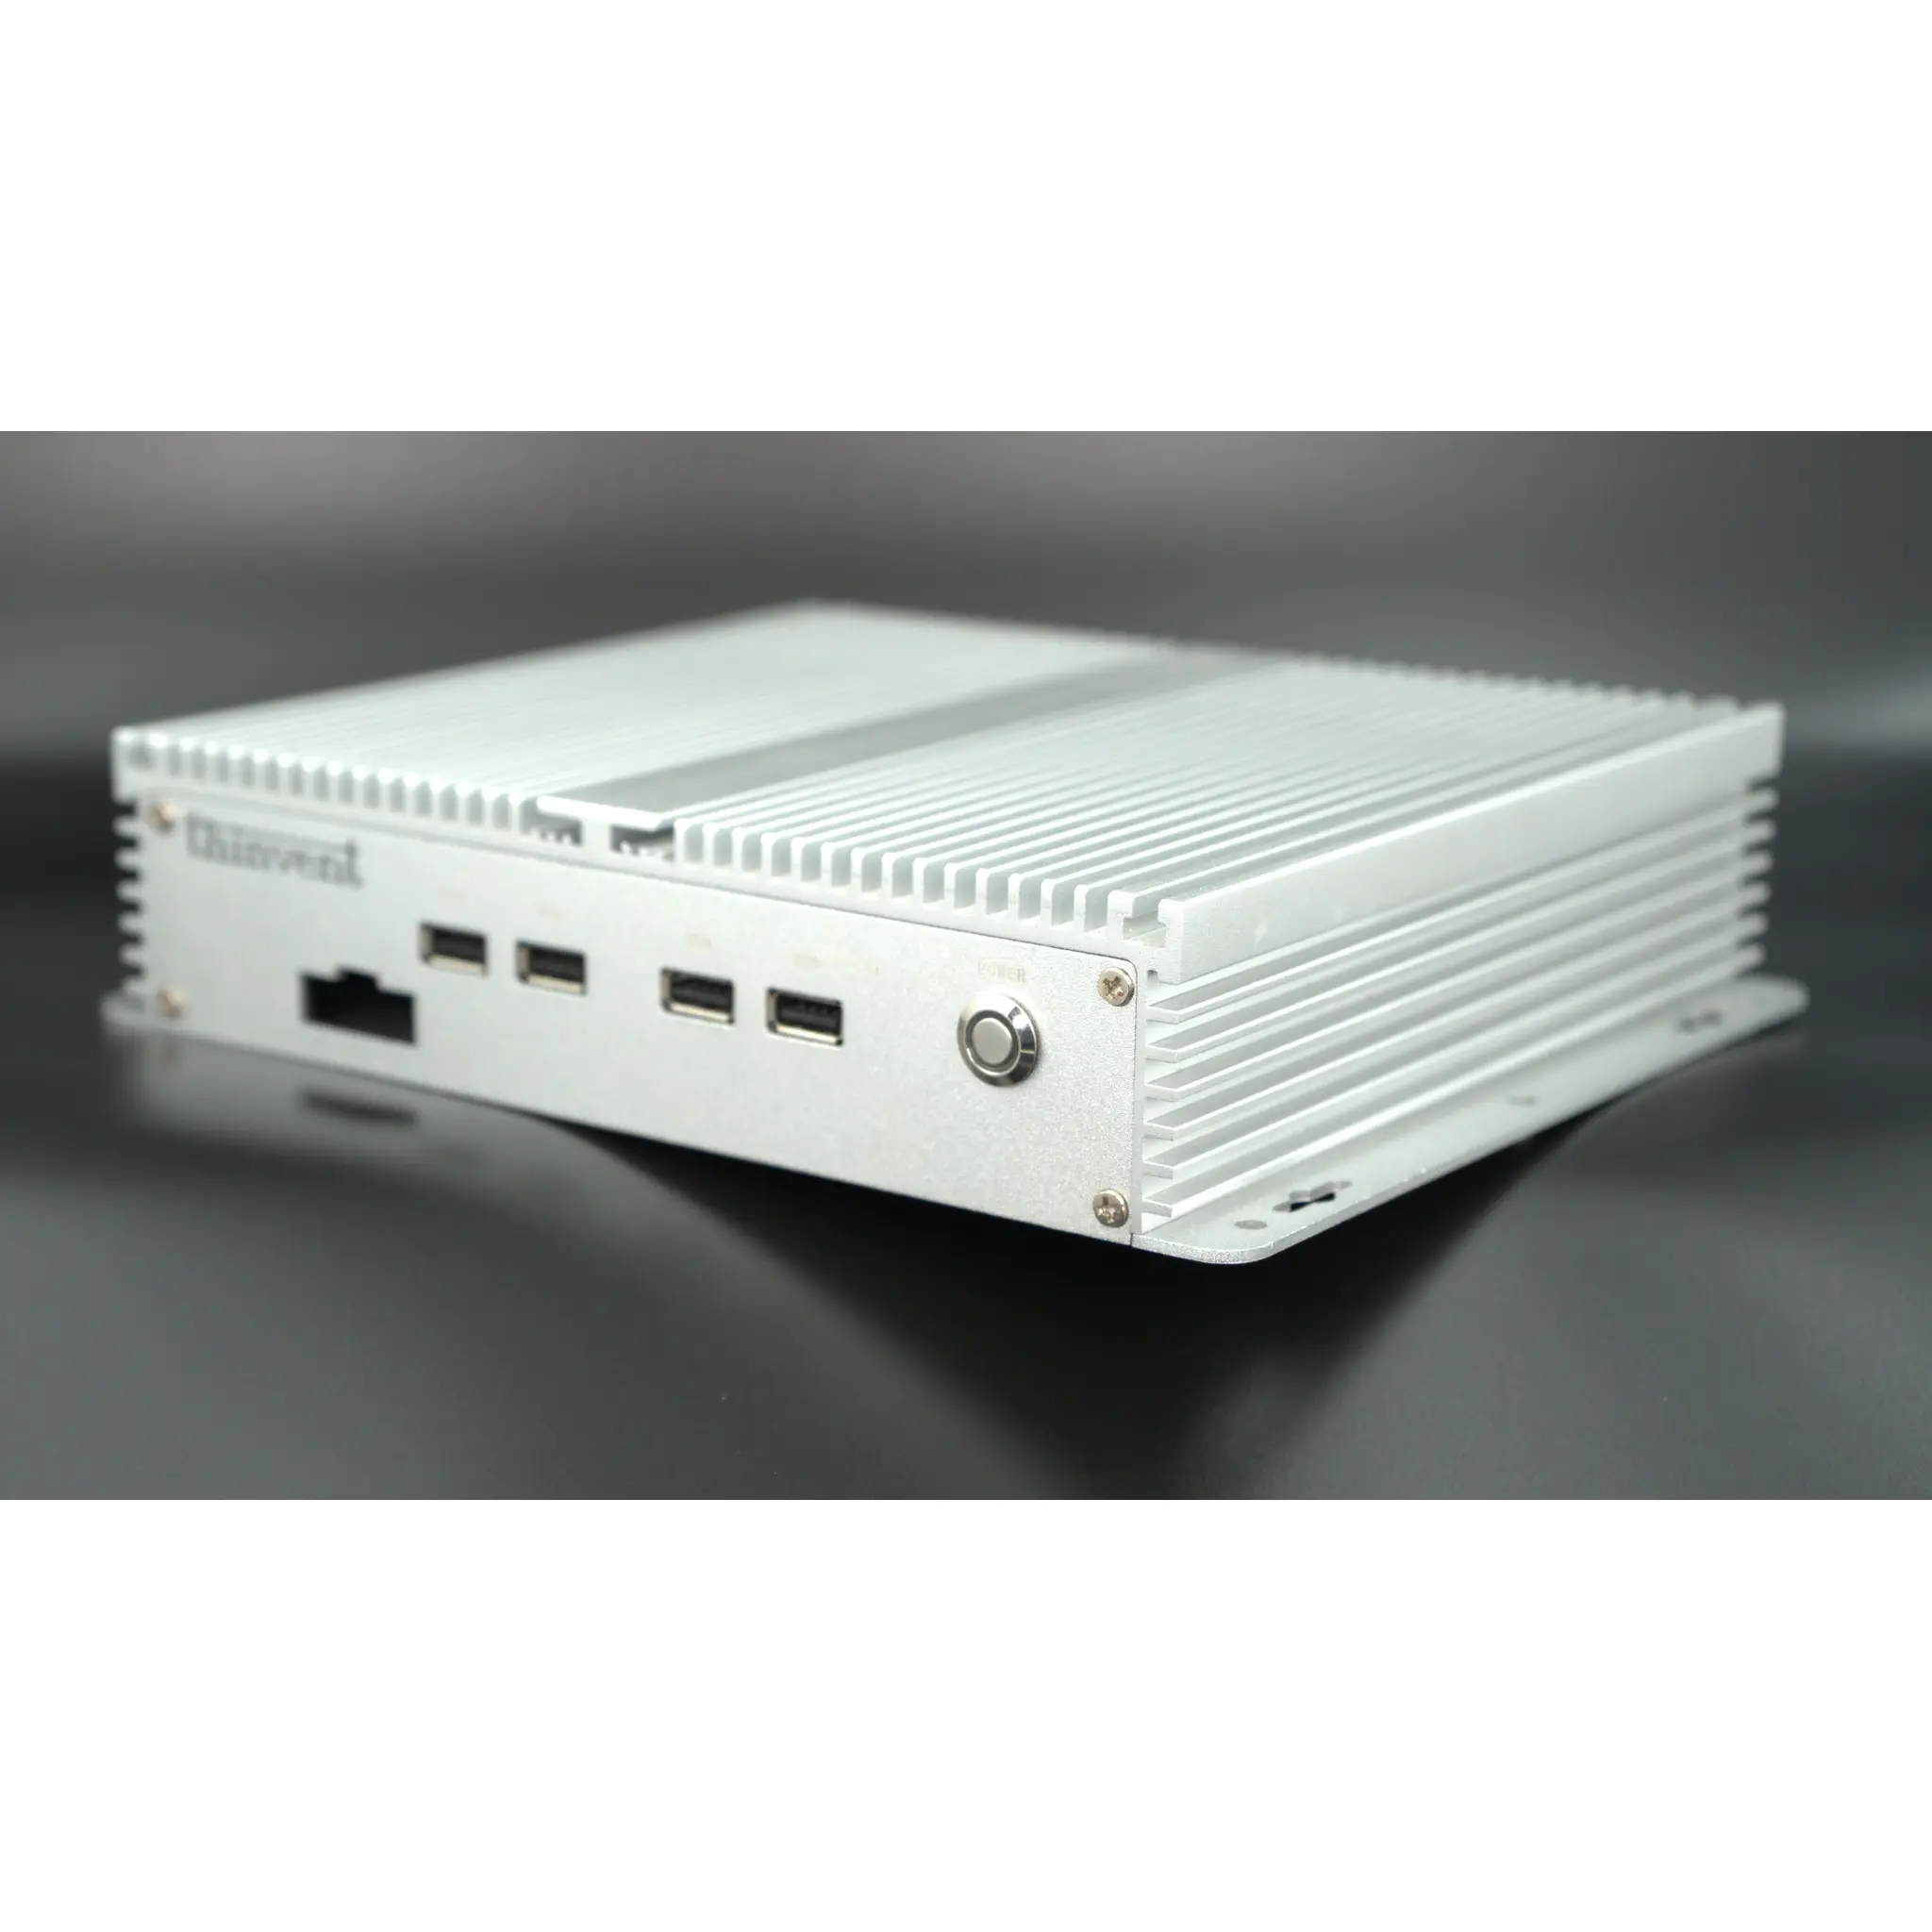
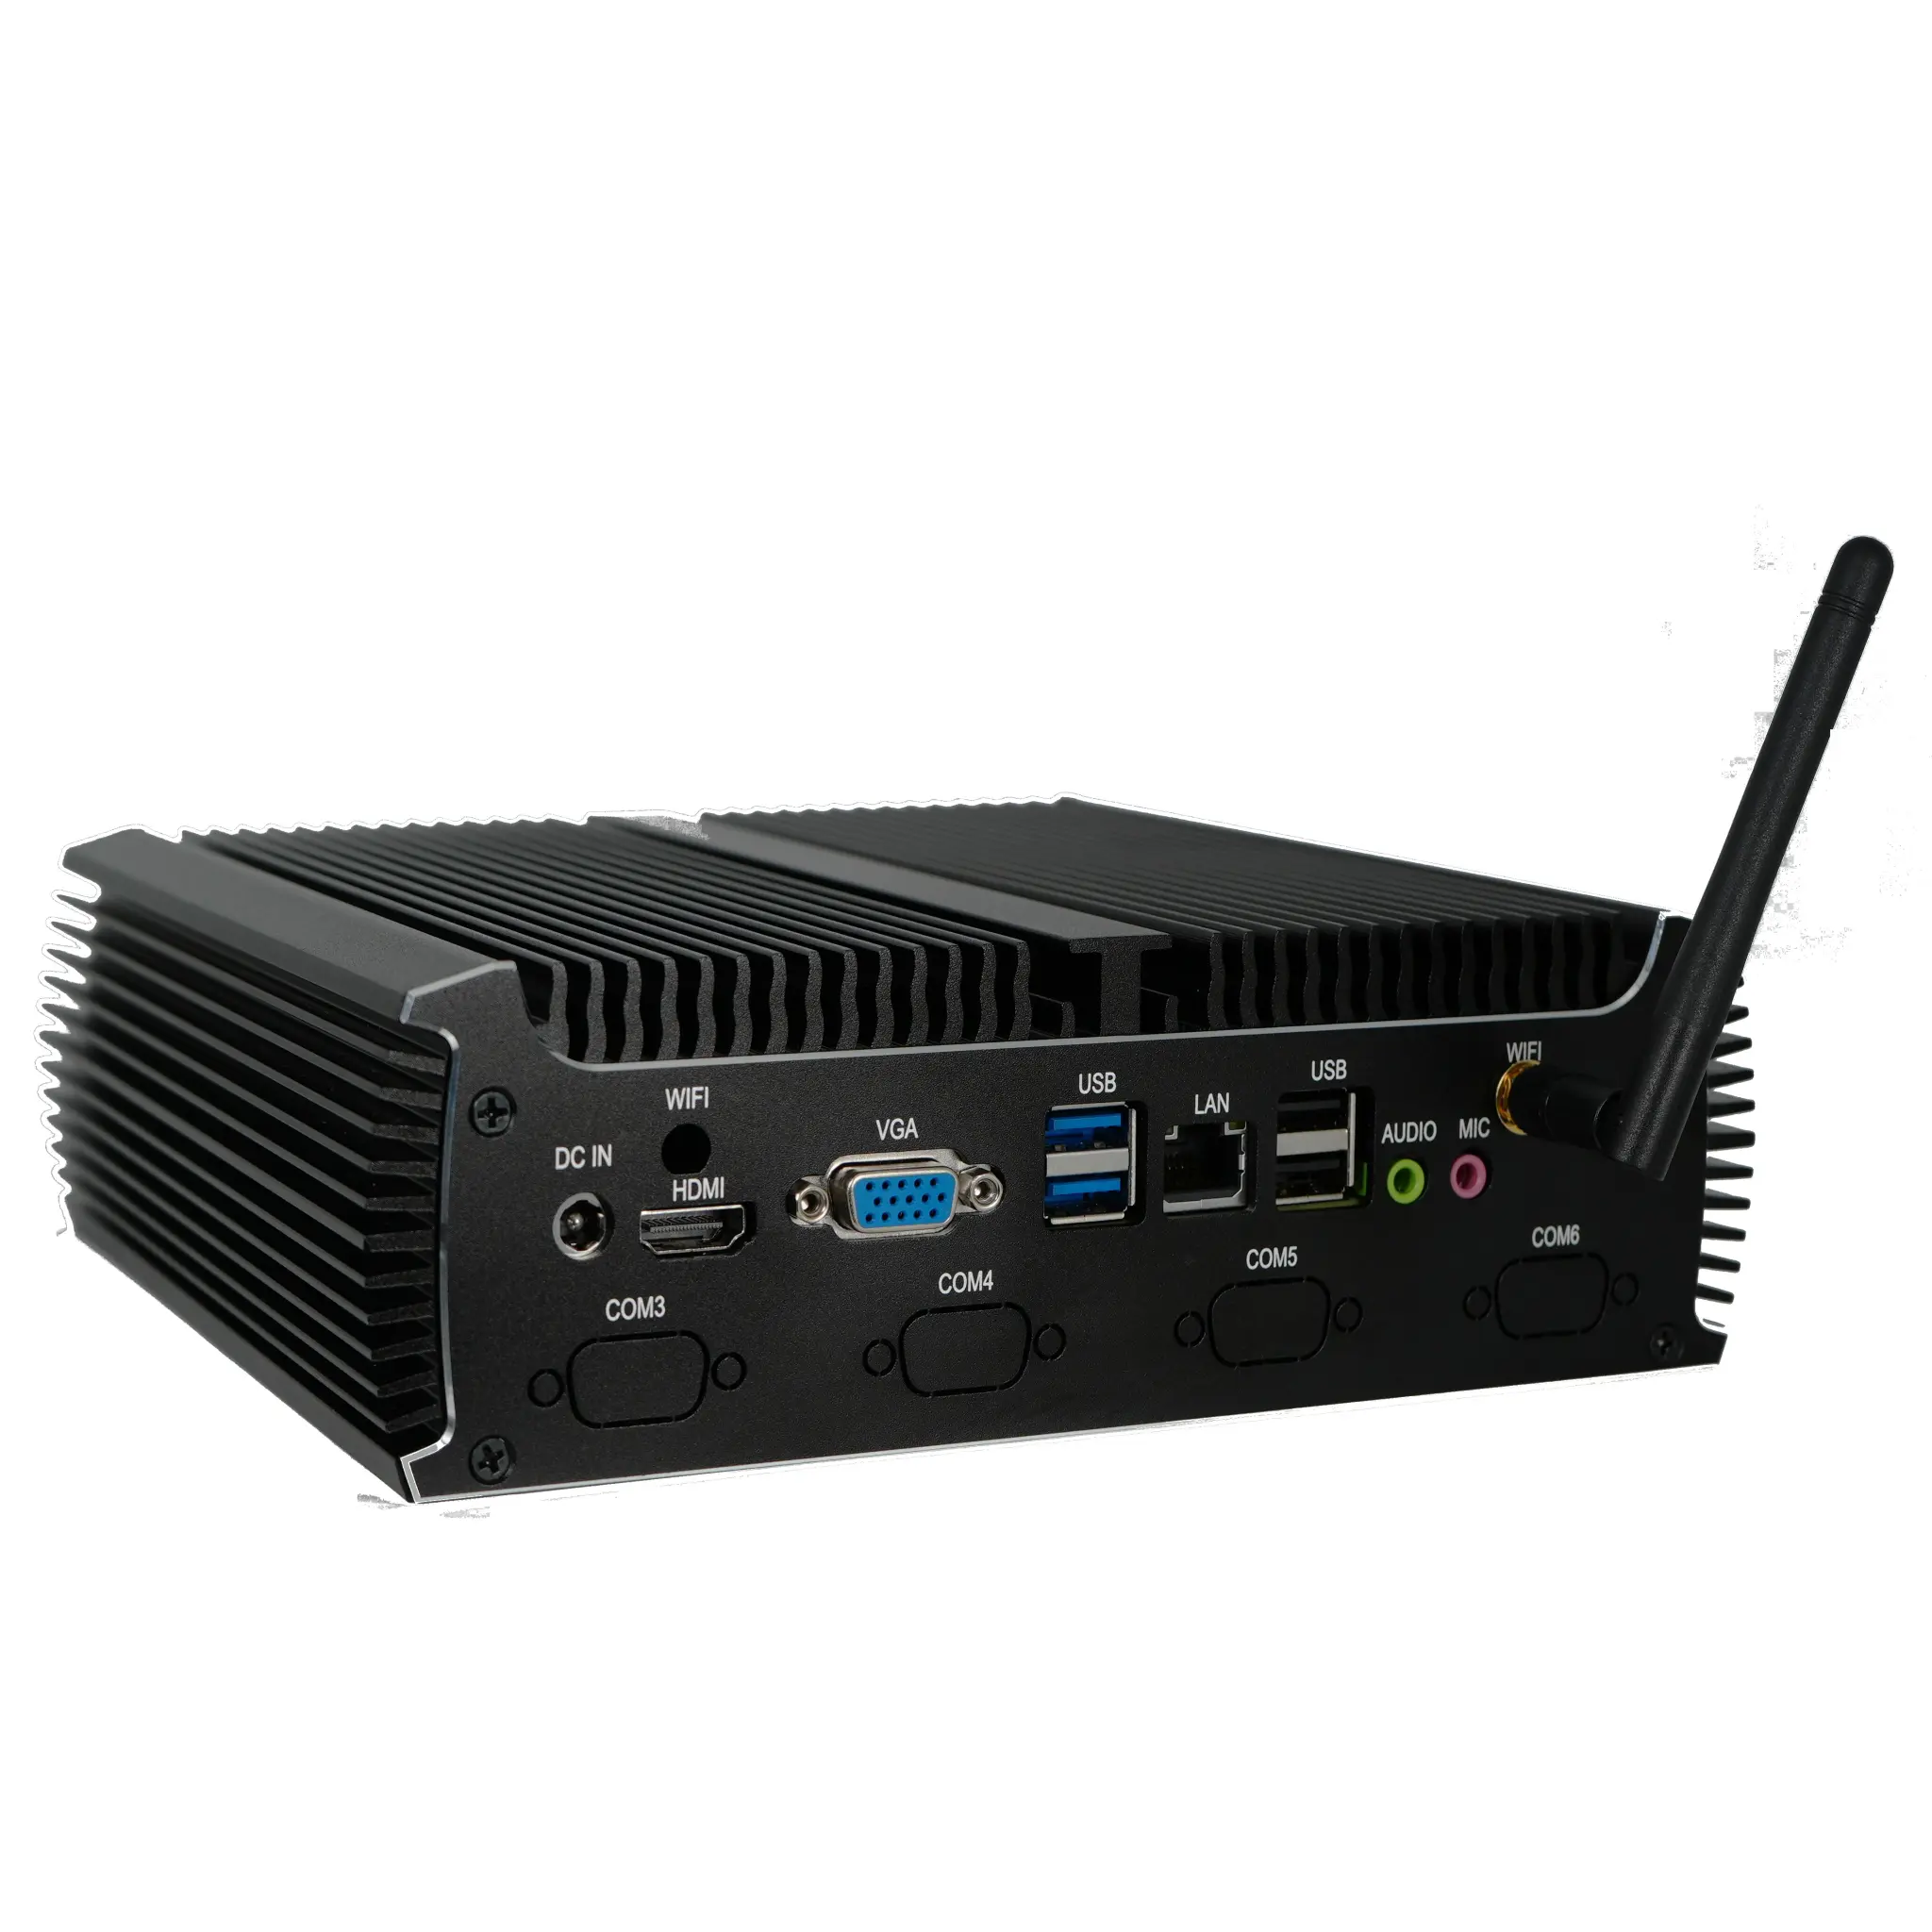
Thinvent integrates TPM security into its range of industrial and commercial computing solutions to provide hardened, reliable platforms for secure deployments. Our products are engineered to leverage this hardware security for diverse applications.
| Product Series | Example Model | Key Processor | Typical Use Case | Security & OS Context |
|---|---|---|---|---|
| Industrial PC Series | IPC5 (Intel Core i5) | Intel Core i5-1250P | High-performance industrial control, machine vision | Compatible with Windows 11 IoT/Pro for secure deployments. |
| Aero Mini PC Series | Aero (Intel Core 5) | Intel Core 5 120U | Enterprise workspaces, secure digital signage | Supports Windows 11 Pro with TPM-based security features. |
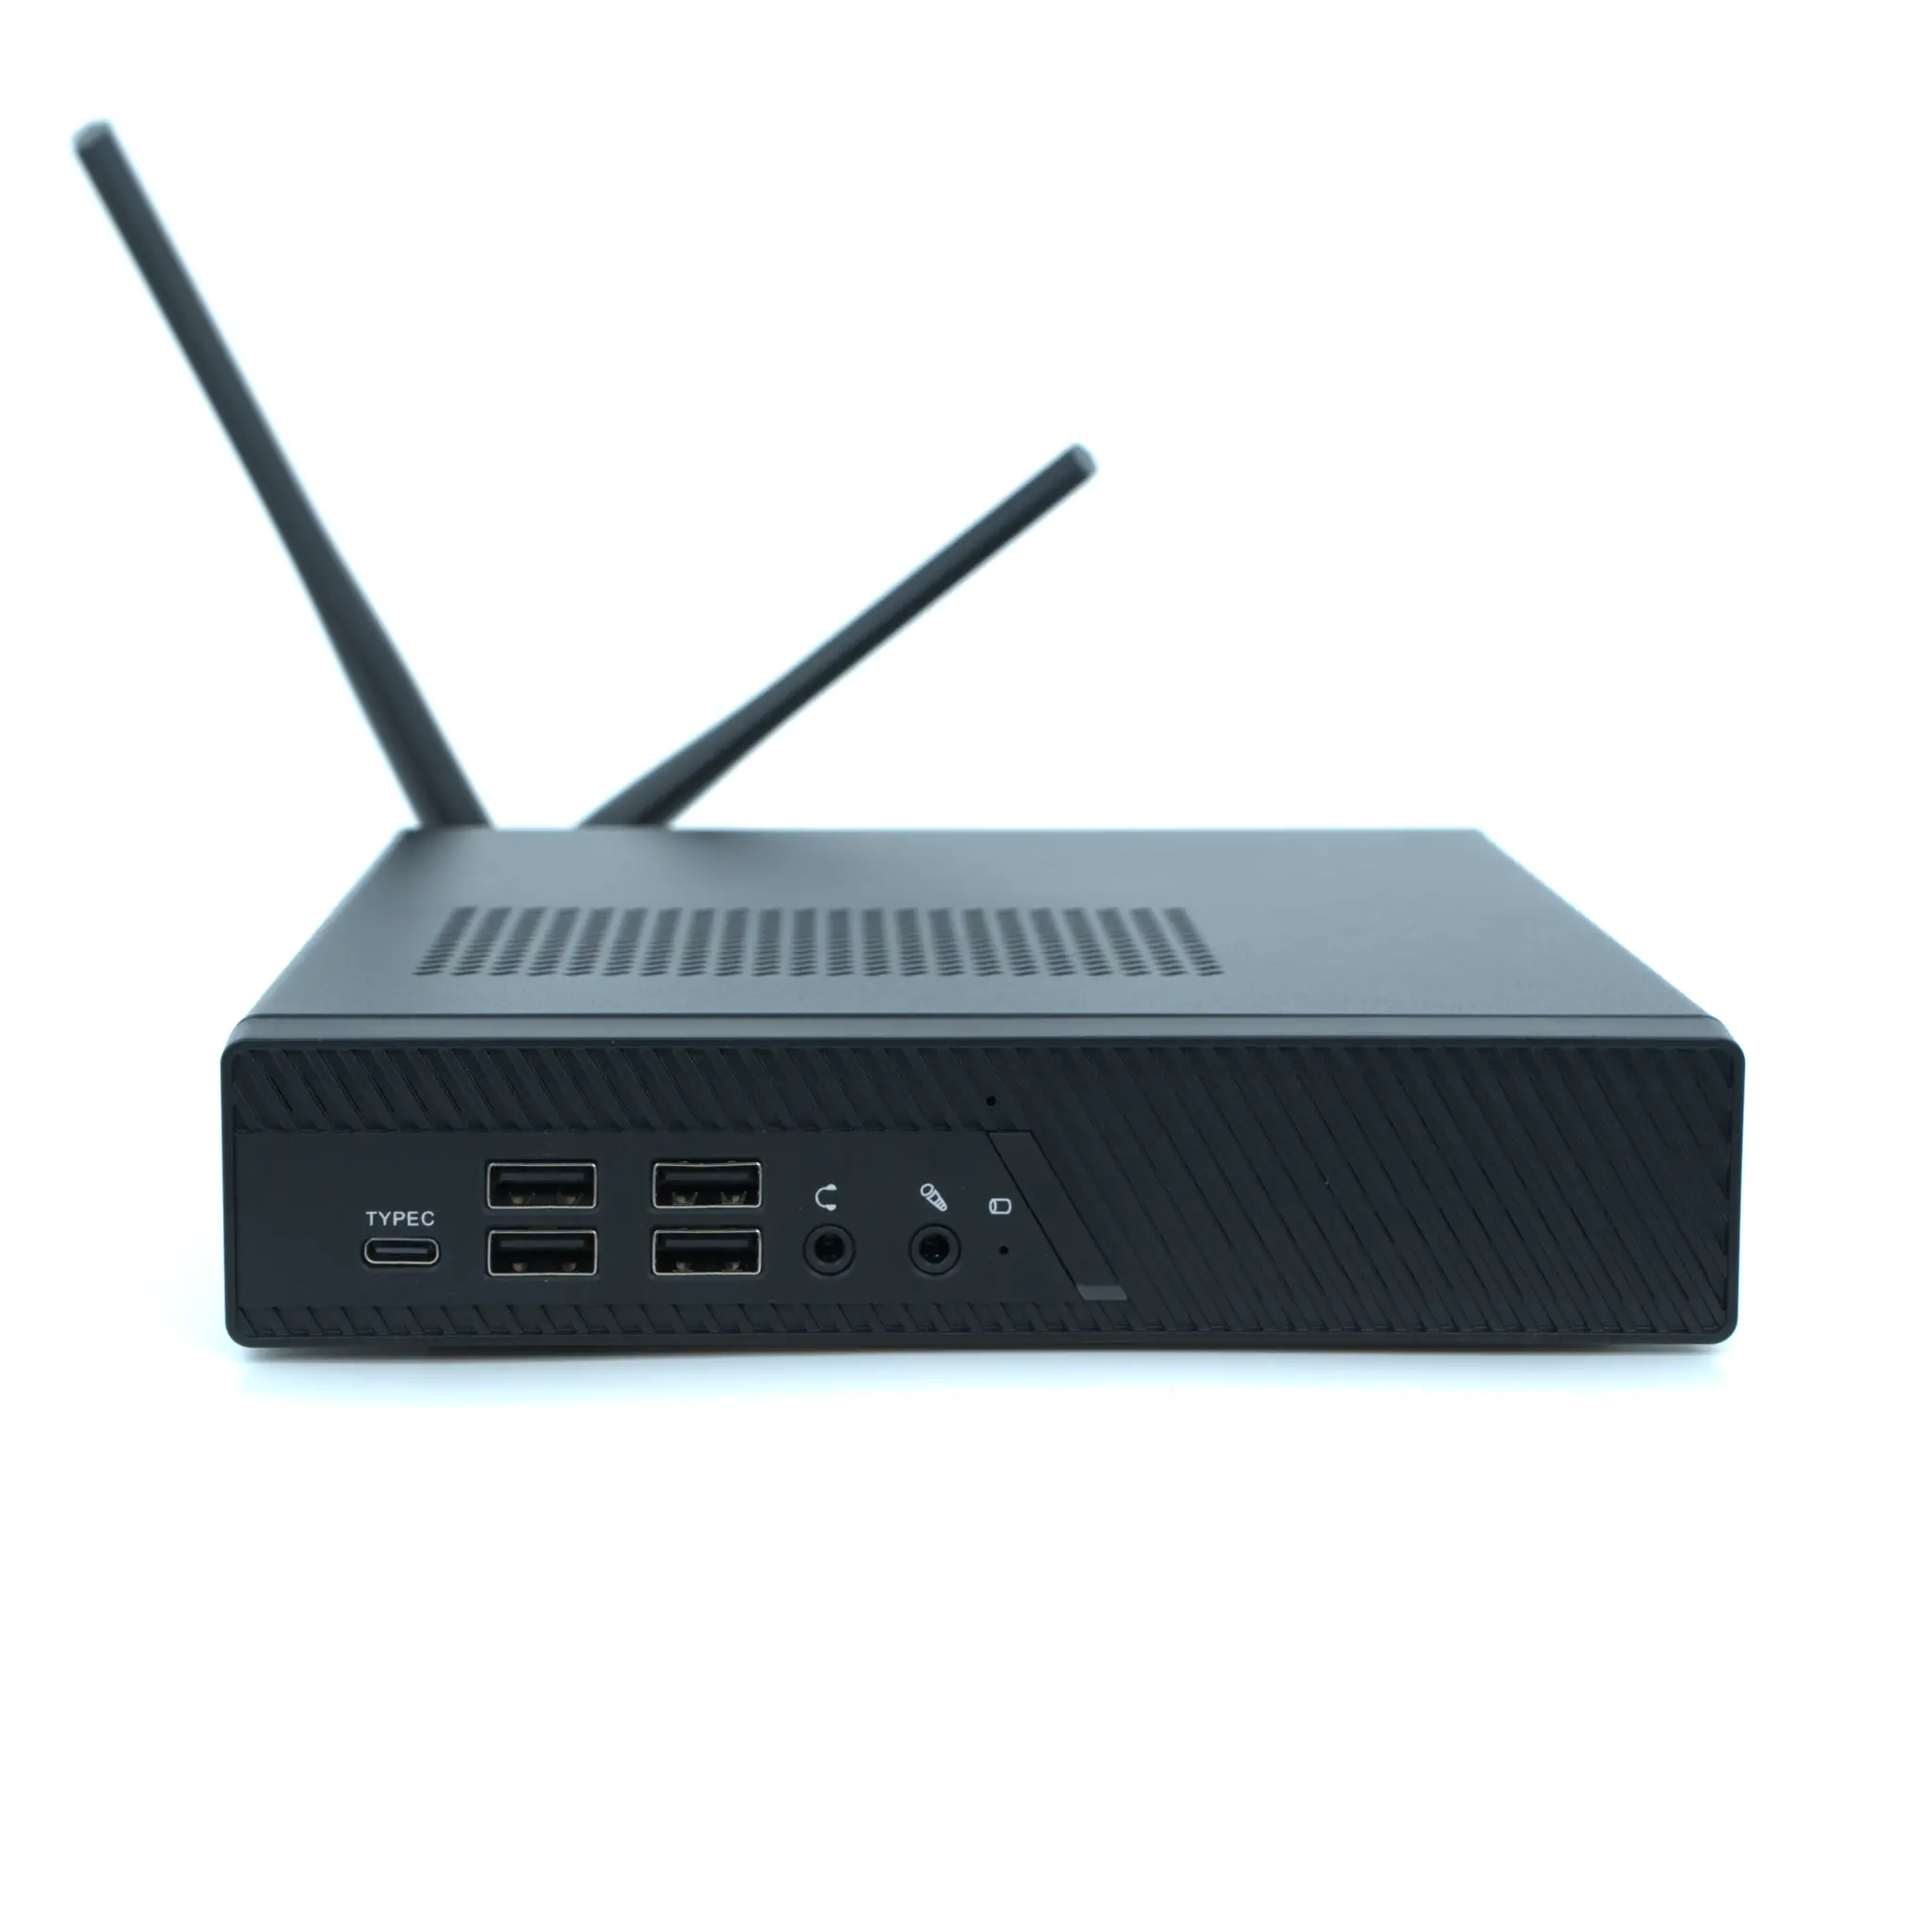
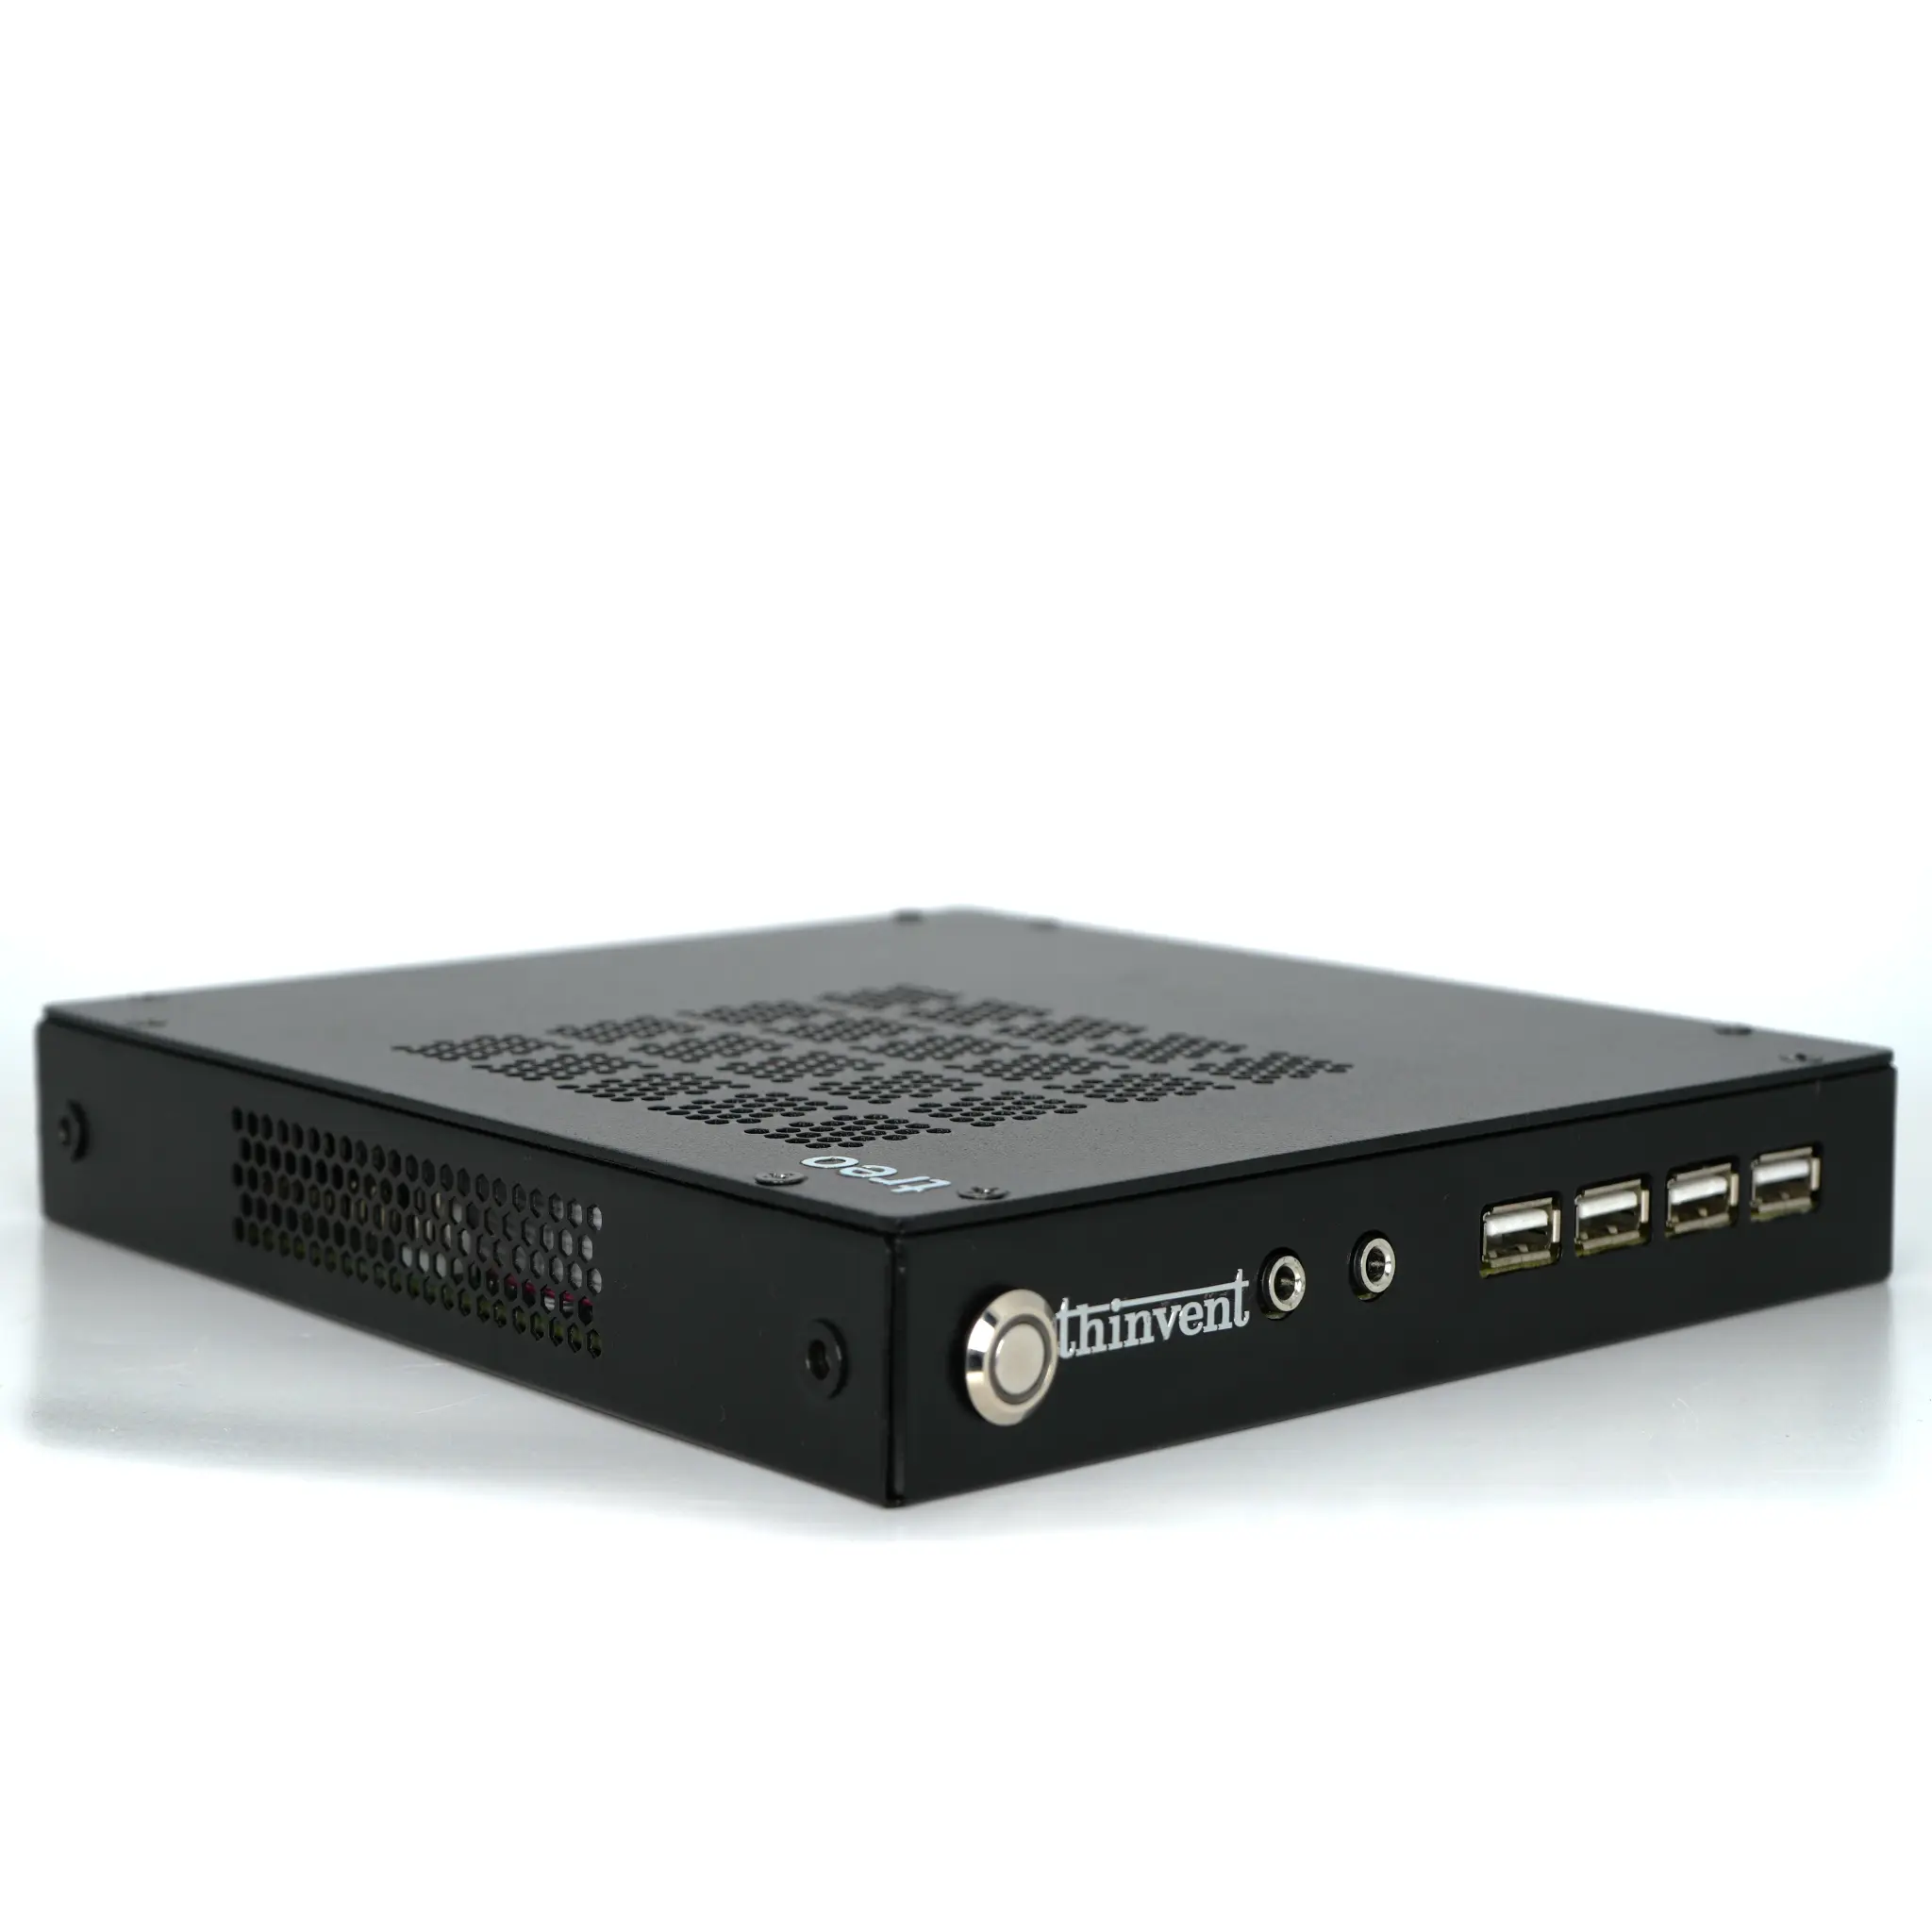
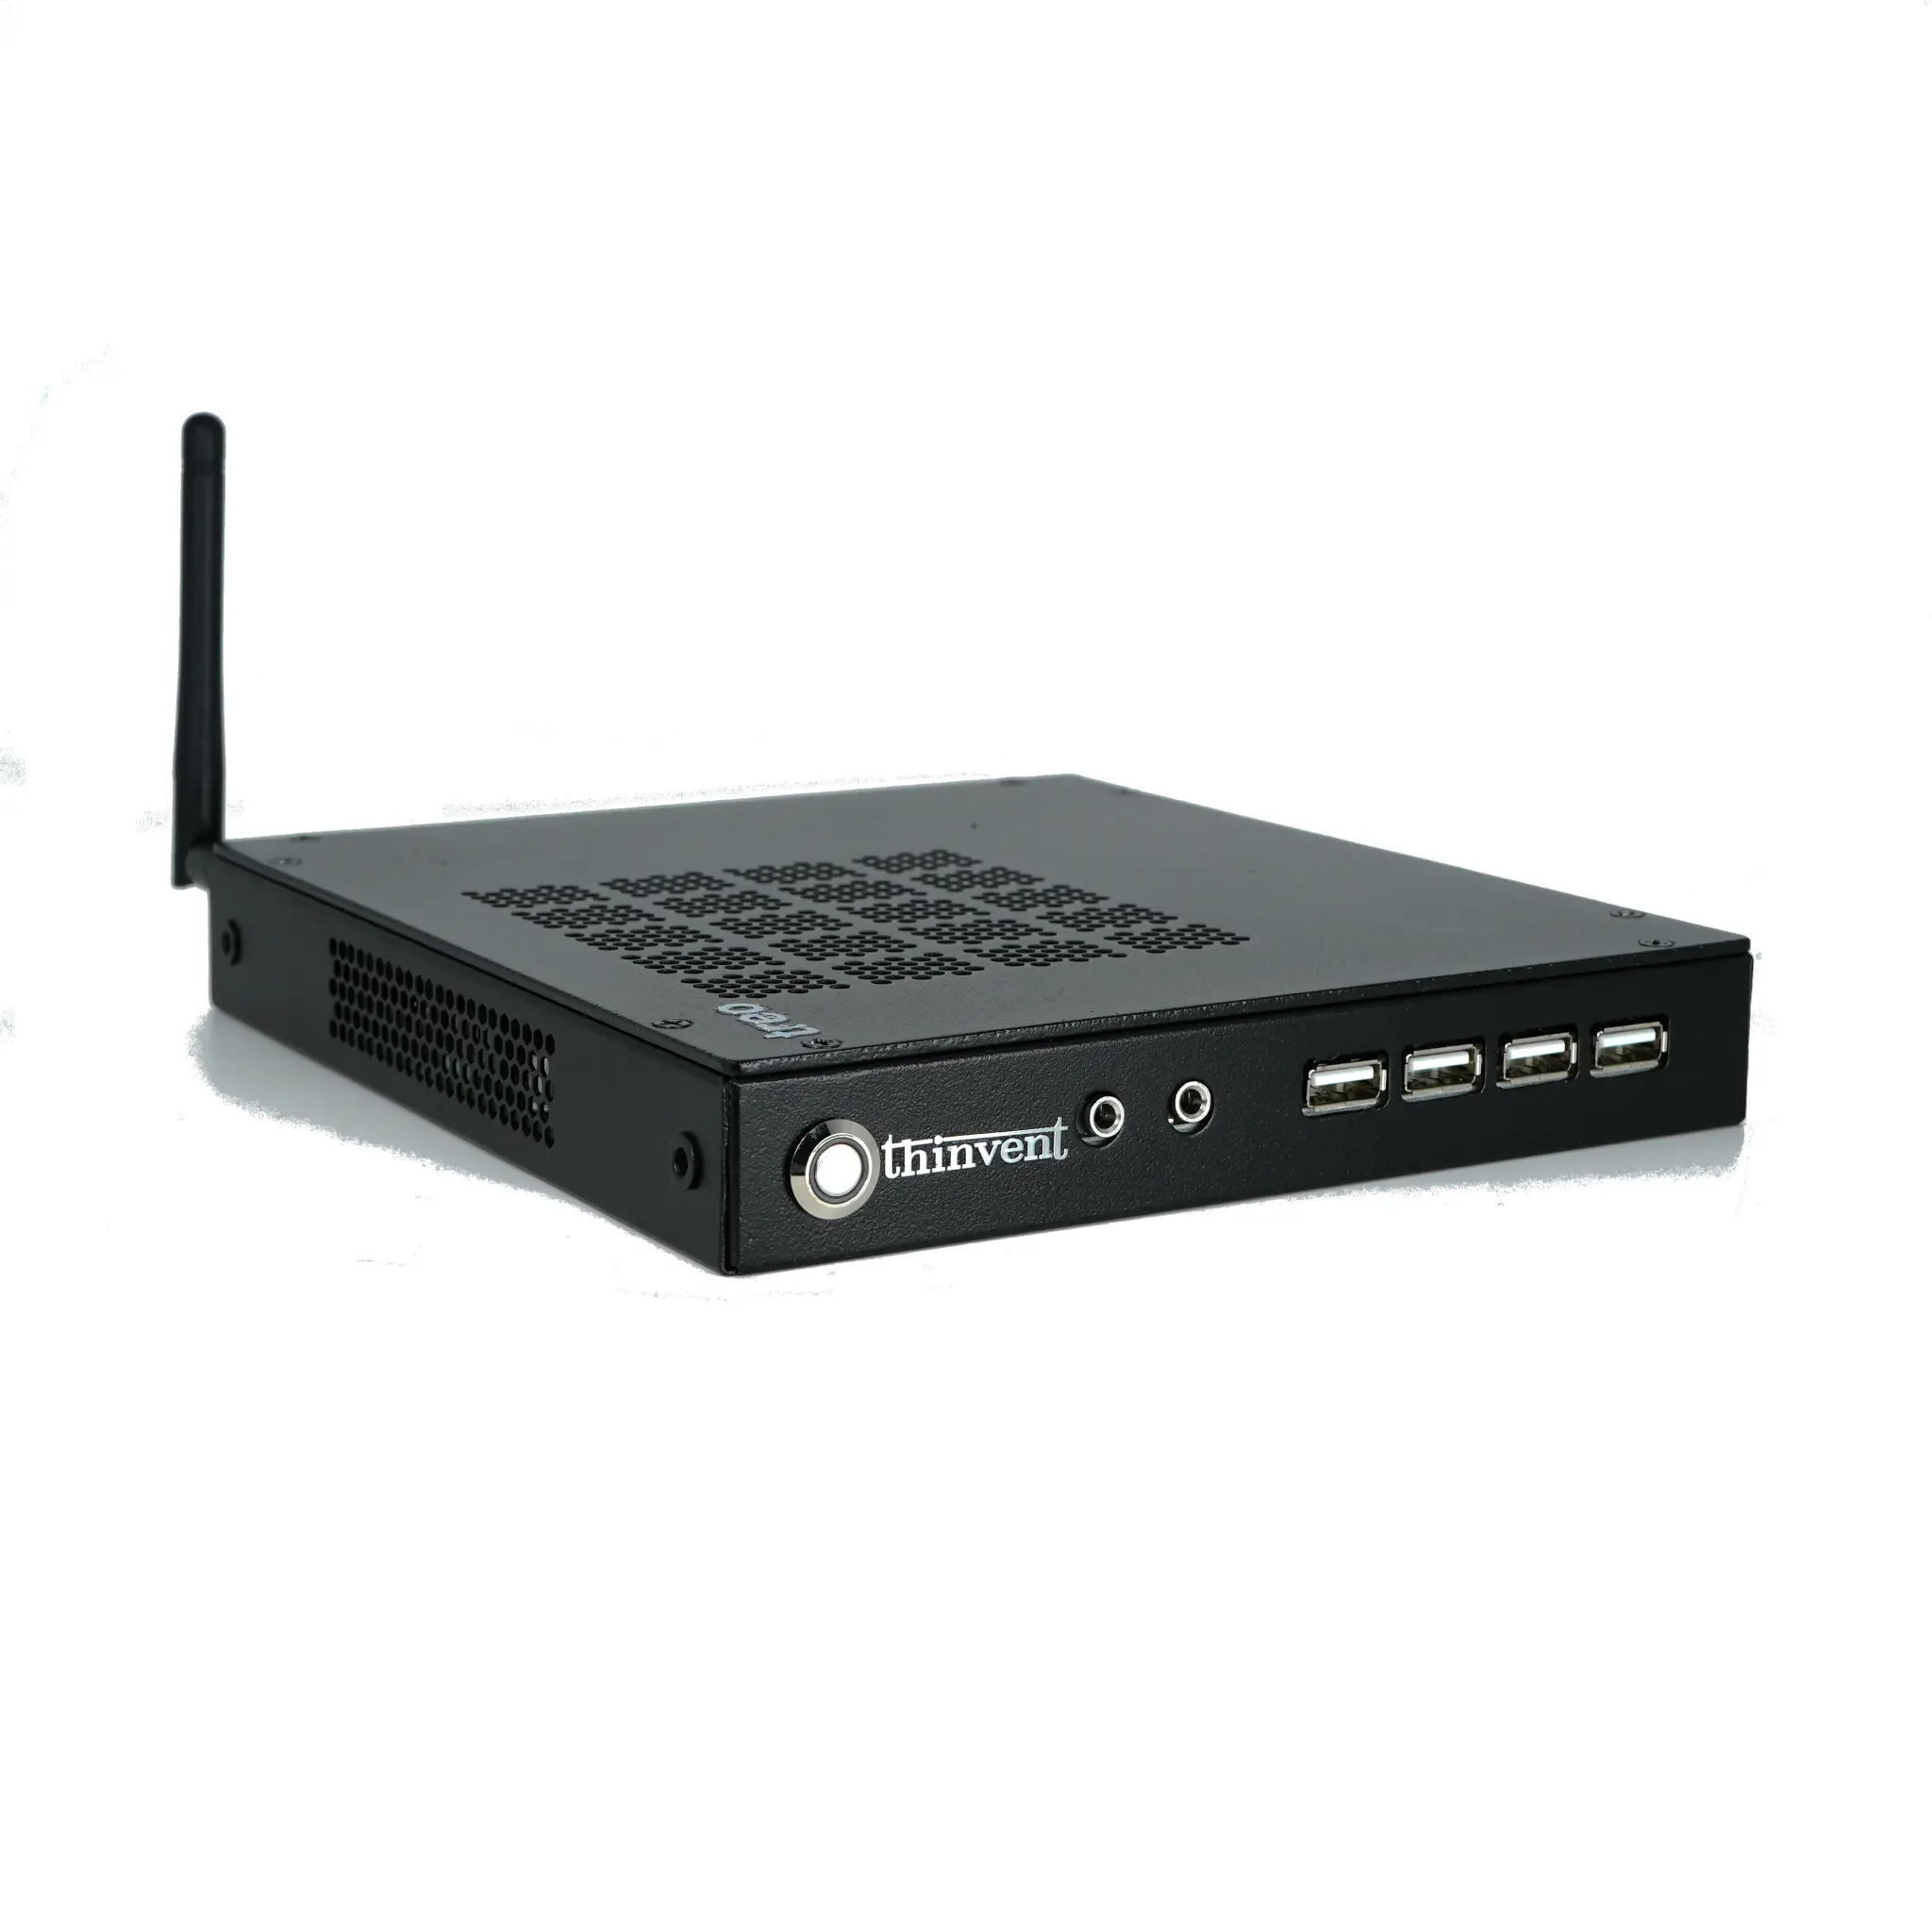
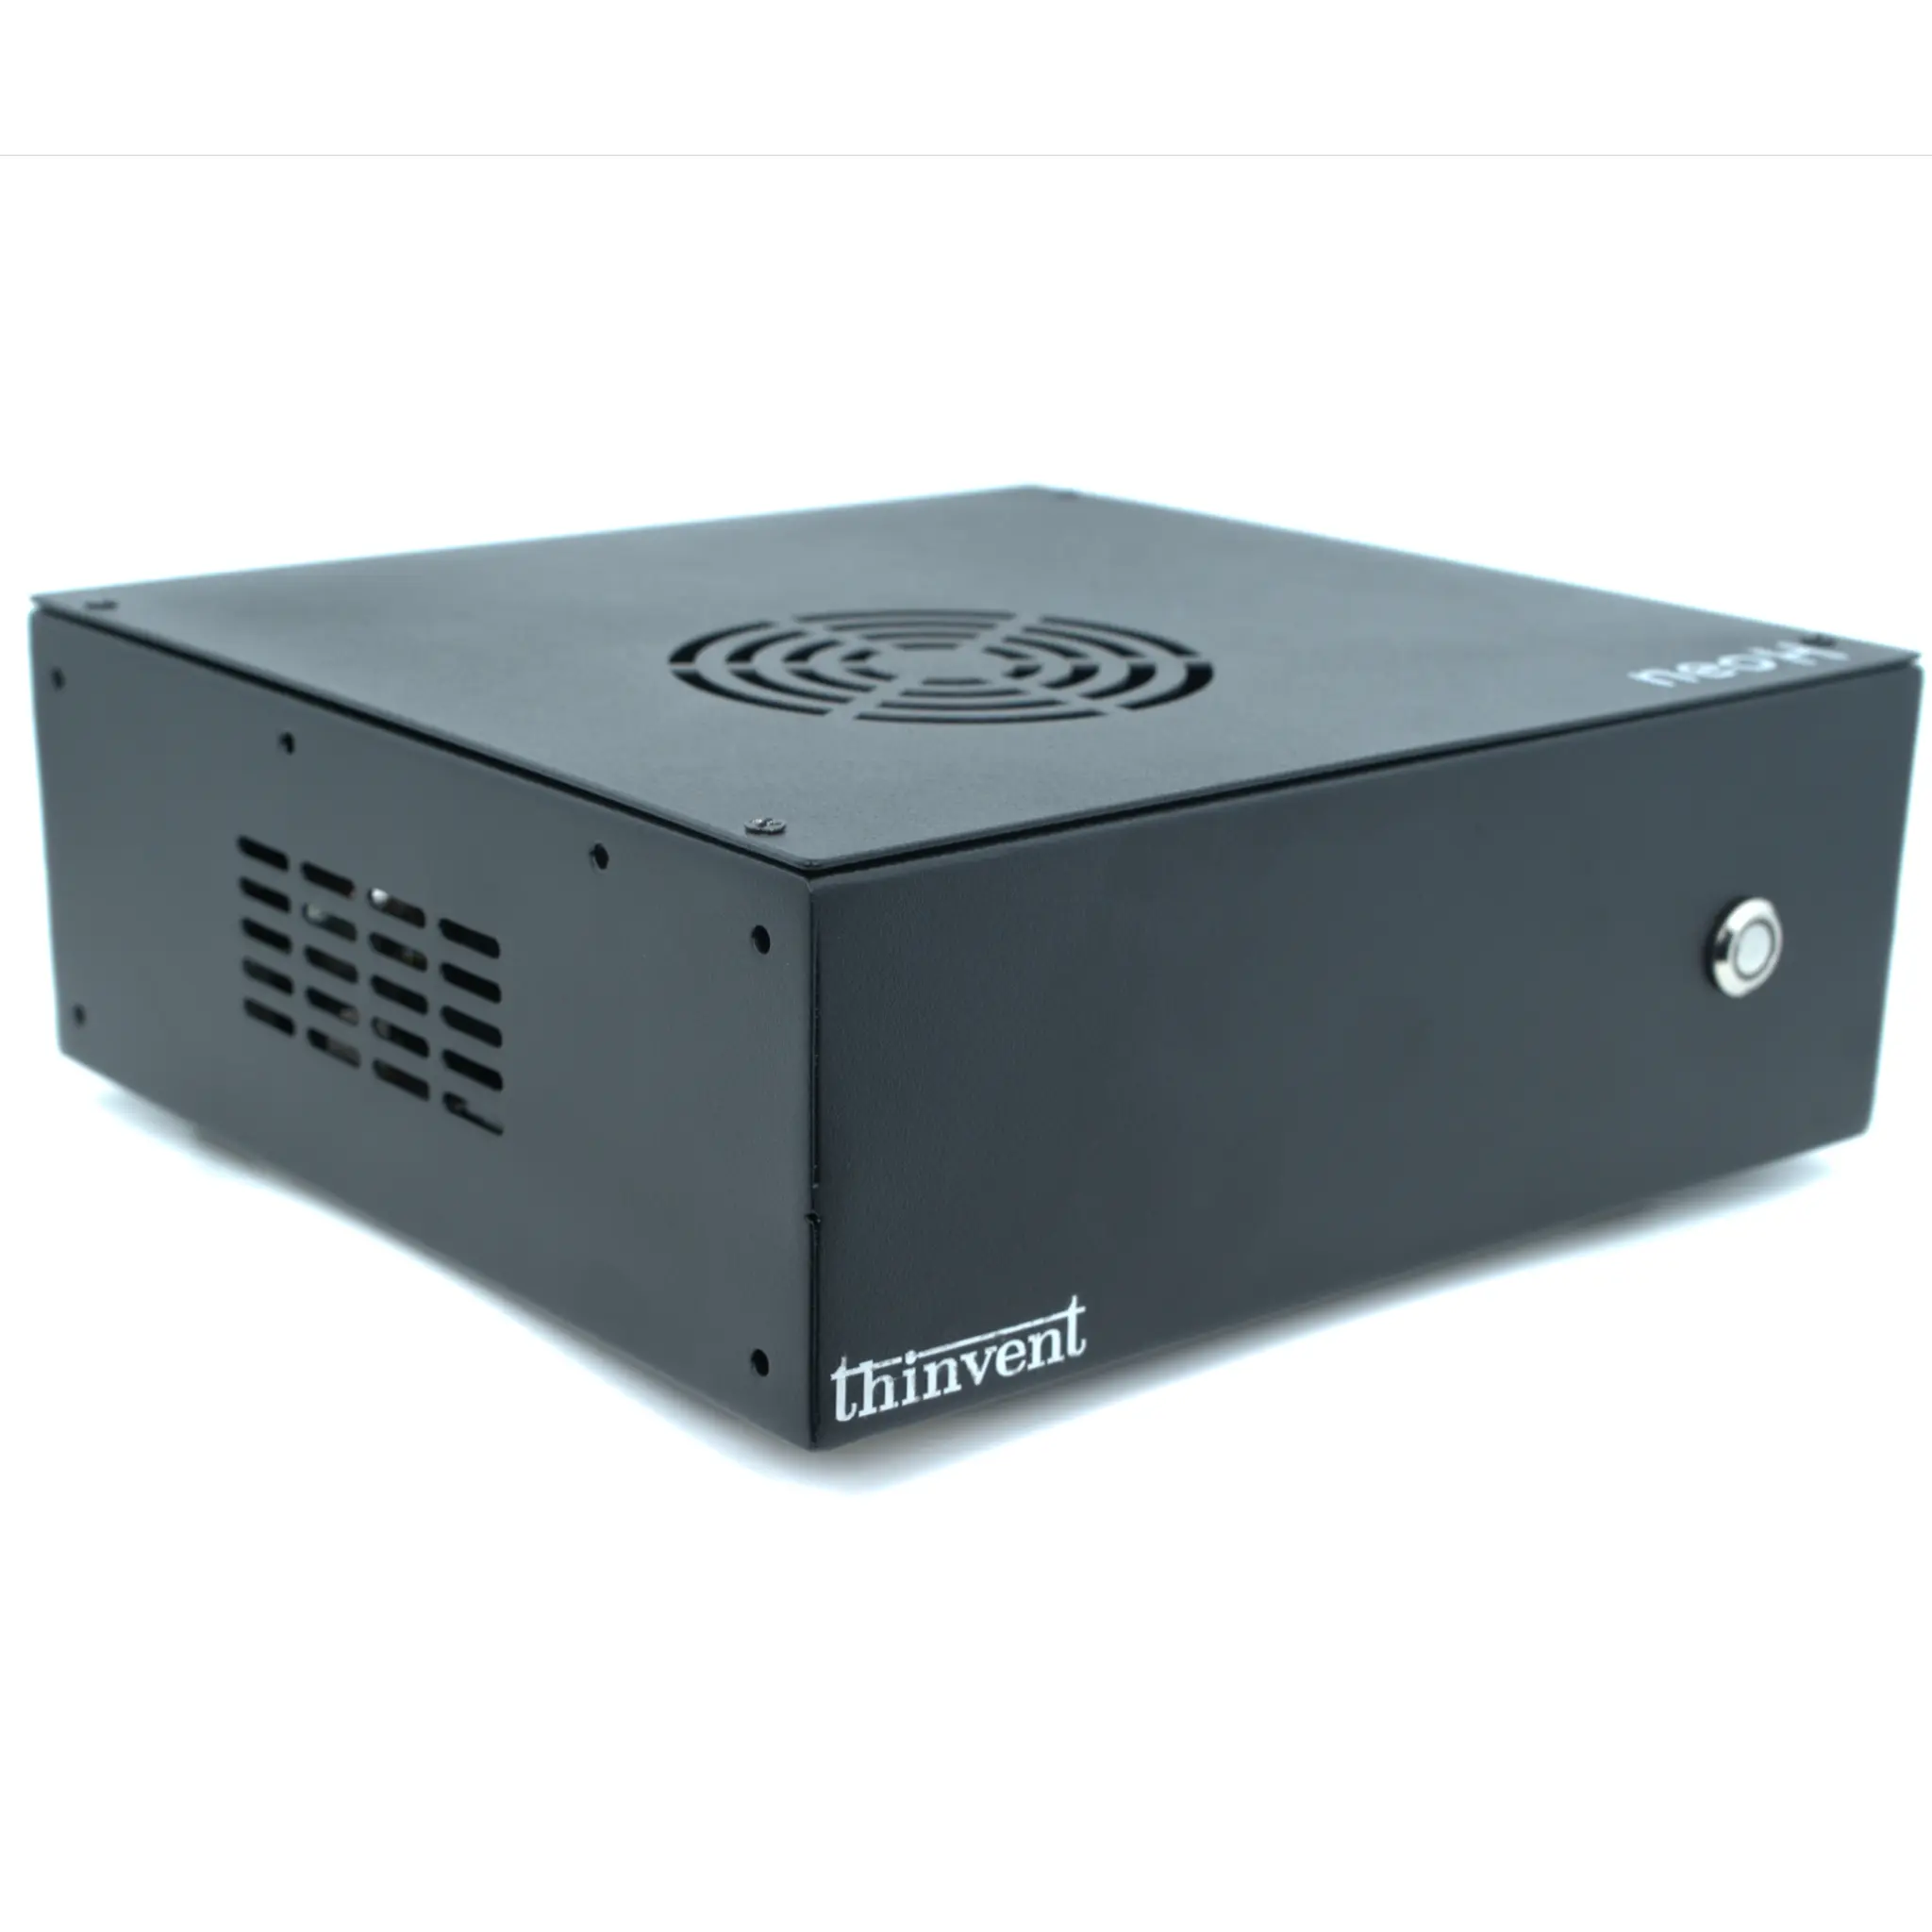
| Treo / IPC1 Series | Treo (Intel N100) | Intel Processor N100 | Light industrial, secure kiosks, edge computing | Runs Ubuntu Linux or Thinux™, enabling secure, customized OS builds. |
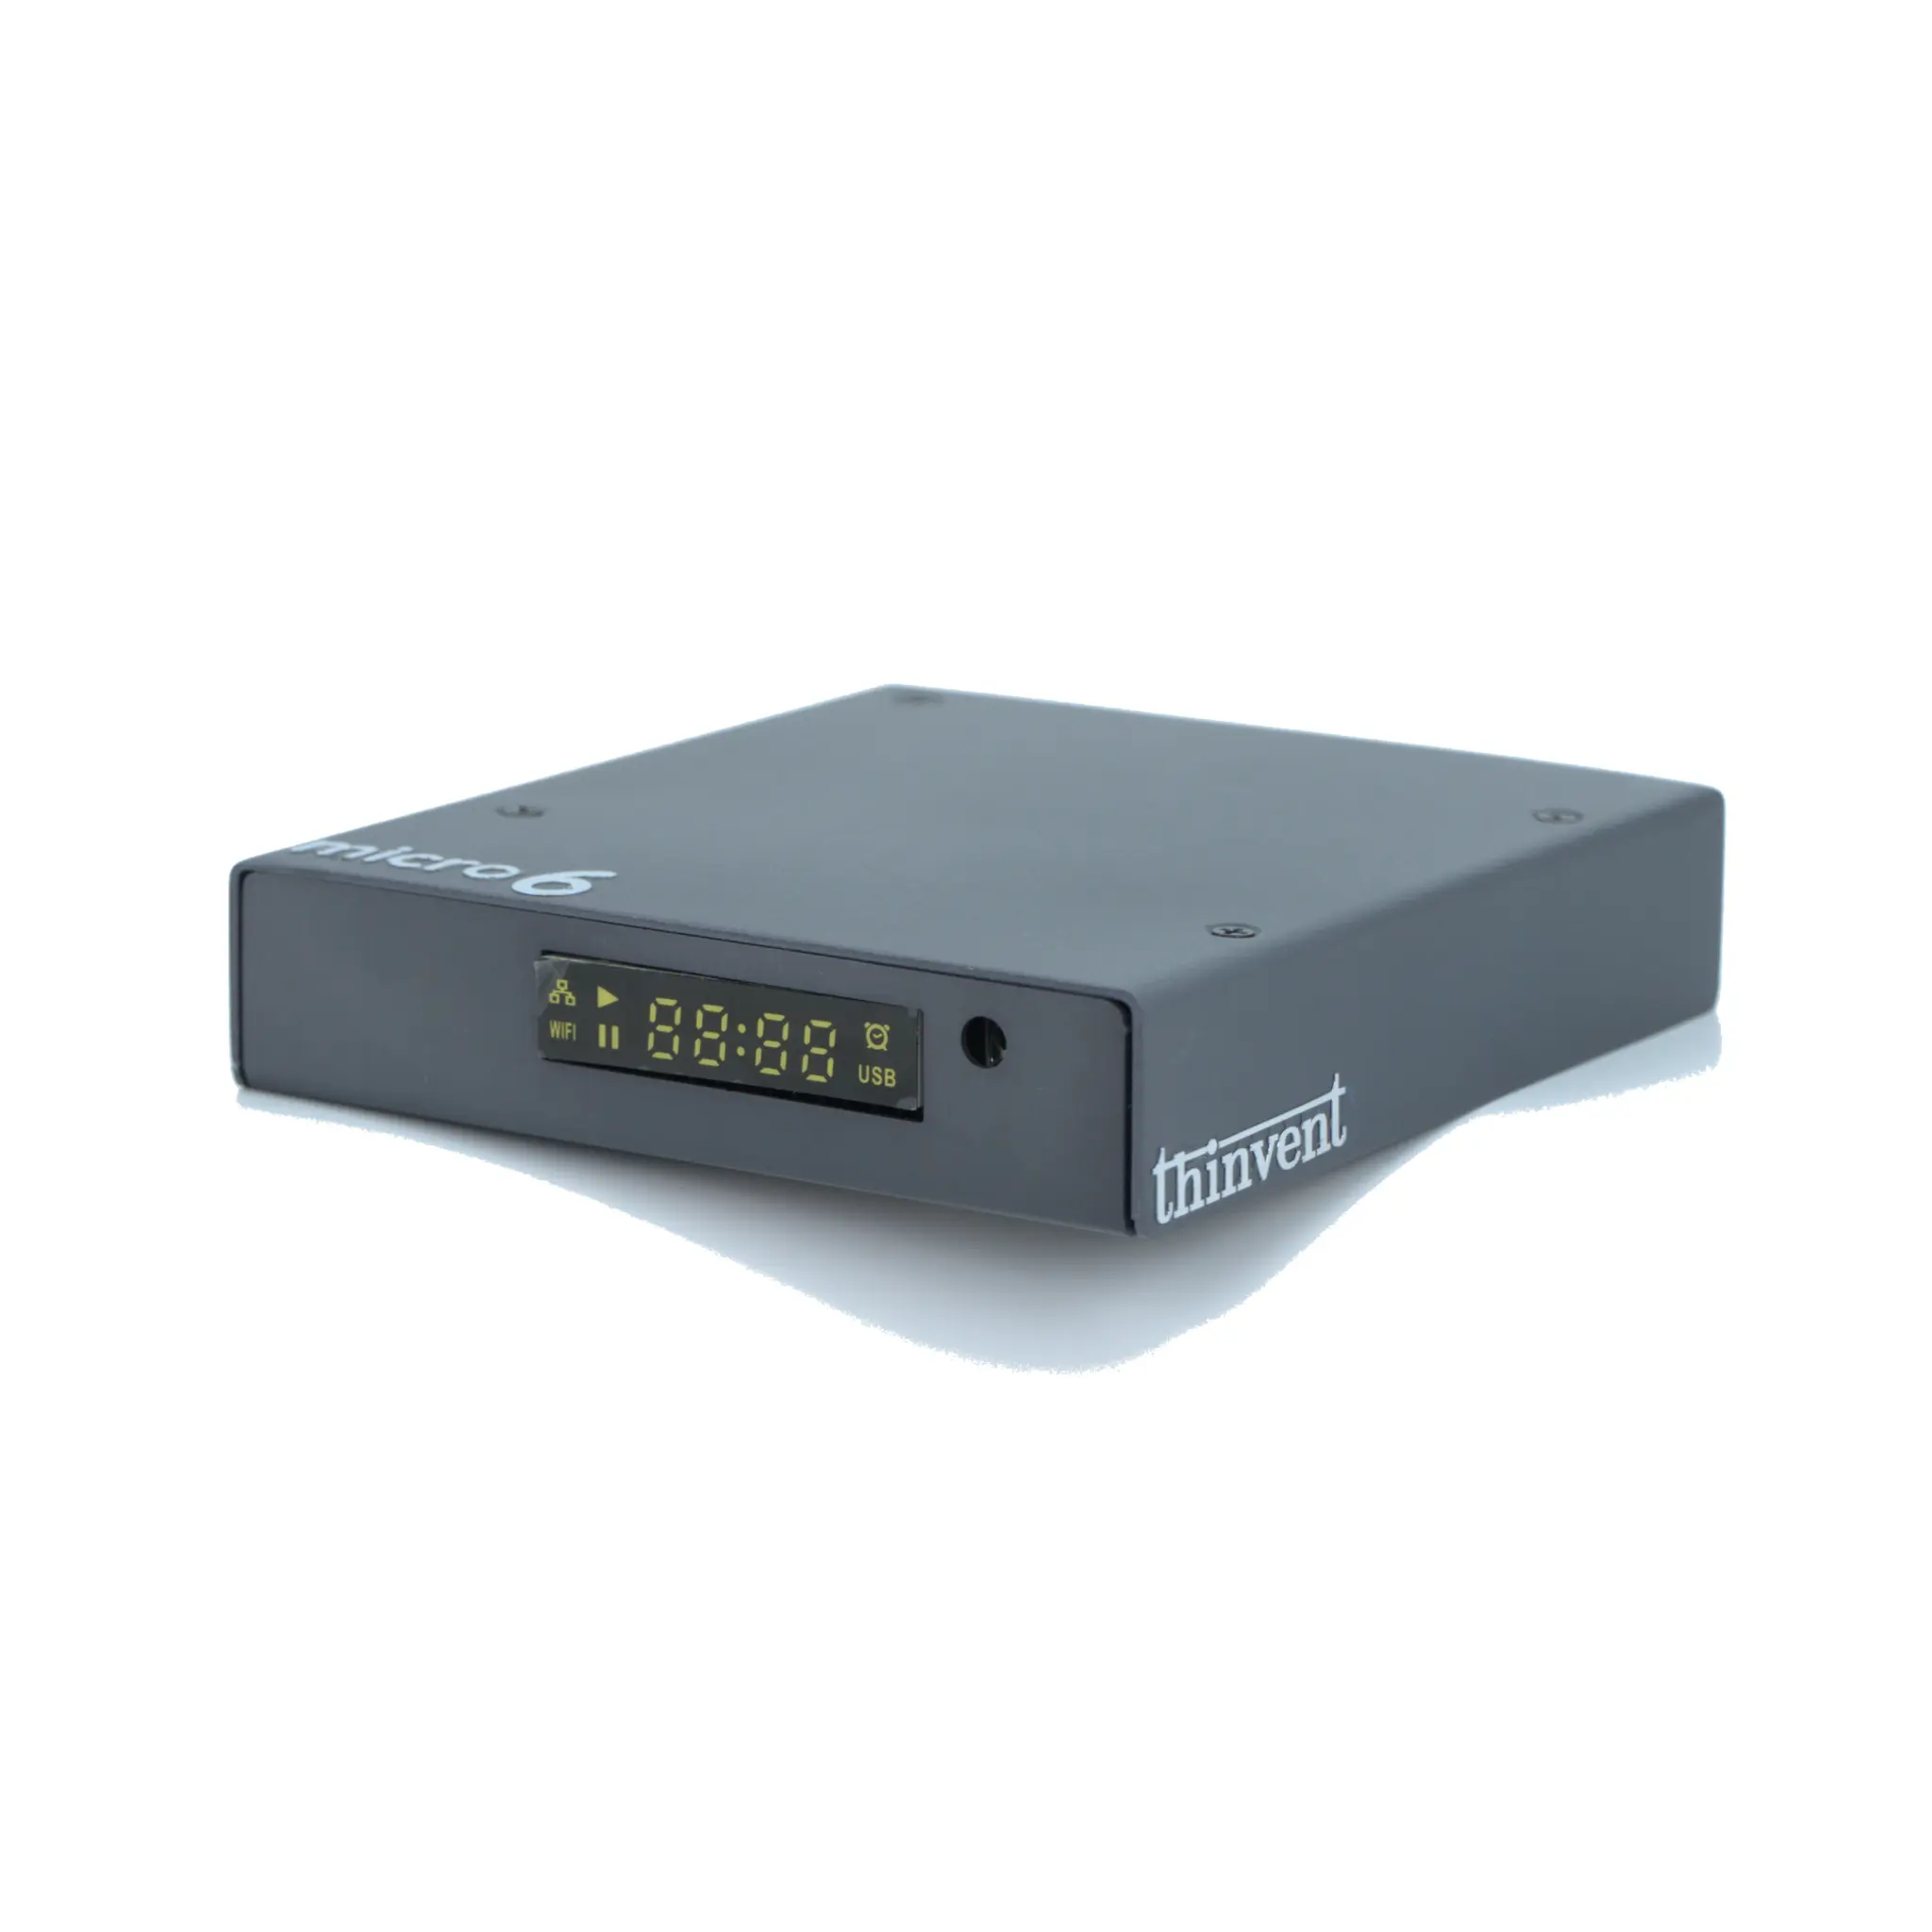
| Micro Thin Client Series | Micro 6 Pro (ARM) | ARM Cortex A55 | Secure thin client for VDI, cloud workloads | Thinux™ Embedded Linux provides a locked-down, secure environment. |
Our systems, whether powered by Intel or energy-efficient ARM processors, are designed with security as a foundational principle. The inclusion of TPM capabilities, either directly or through support for secure boot and measured boot processes in our Thinux™ Embedded Linux and Ubuntu configurations, ensures that Thinvent devices provide a trusted foundation for your most critical applications worldwide.