What is a Trusted Platform Module (TPM)?
A Trusted Platform Module (TPM) is a dedicated hardware security chip embedded on a computer's motherboard that provides hardware-based protection for cryptographic keys, passwords, and digital certificates. Unlike software-only security solutions, a TPM creates a secure enclave that is isolated from the main operating system, making it resistant to tampering and software attacks. TPM 2.0, the current industry standard, is required for modern operating systems like Windows 11 to ensure secure boot, disk encryption (BitLocker), and platform integrity verification.
Key Specifications and Technical Details
TPM 2.0 offers several critical features that enhance system security:
| Feature | Description |
|---|---|
| Secure Boot | Verifies that only trusted software loads during startup, preventing rootkits and bootkits |
| Hardware Key Storage | Stores encryption keys in tamper-resistant hardware, not on the main drive |
| Remote Attestation | Allows systems to prove their integrity to remote servers for network access |
| Measured Boot | Logs all boot components for verification against known-good values |
| Sealed Storage | Protects data such that it can only be decrypted when the system is in a trusted state |
TPM 2.0 supports multiple cryptographic algorithms including RSA, ECC, SHA-1, SHA-256, and AES, providing flexibility for various security protocols. The module typically communicates with the system via LPC or SPI bus interfaces.
Use Cases and Applications
TPM technology is essential across numerous industries where data security and system integrity are paramount:
-
Point-of-Sale (POS) Systems: Protects payment card data and ensures tamper-proof transaction processing
-
Medical Devices: Safeguards patient data and ensures only authorized software runs on diagnostic equipment
-
Industrial Control: Secures SCADA systems and prevents unauthorized modifications to critical infrastructure
-
Digital Signage: Ensures content integrity and prevents unauthorized access to display networks
-
Kiosk Systems: Provides secure authentication and protects sensitive user information in self-service terminals
For organizations requiring compliance with regulations like GDPR, HIPAA, or PCI-DSS, TPM 2.0 provides the hardware root of trust necessary for meeting stringent security requirements.
Thinvent's TPM-Enabled Product Range
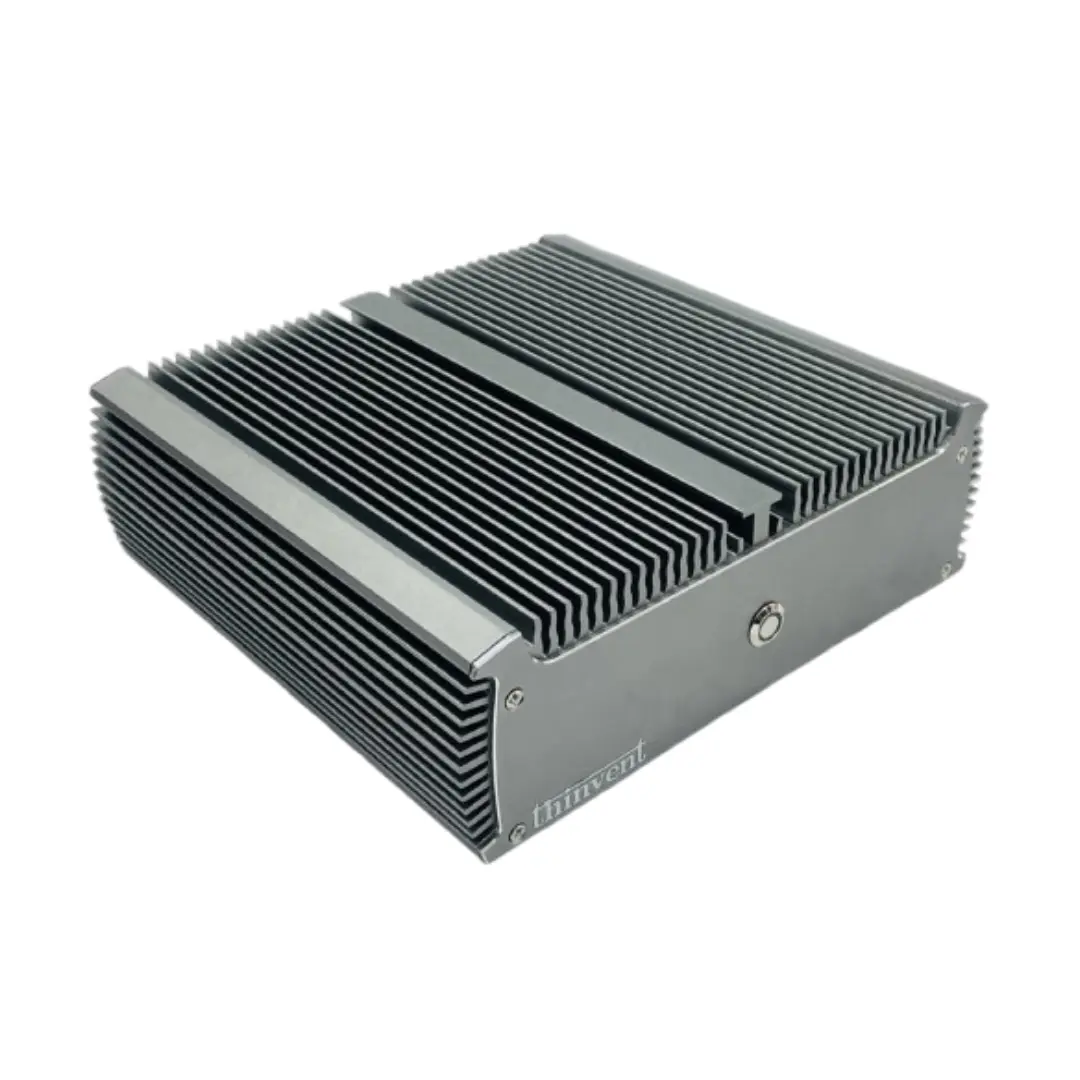
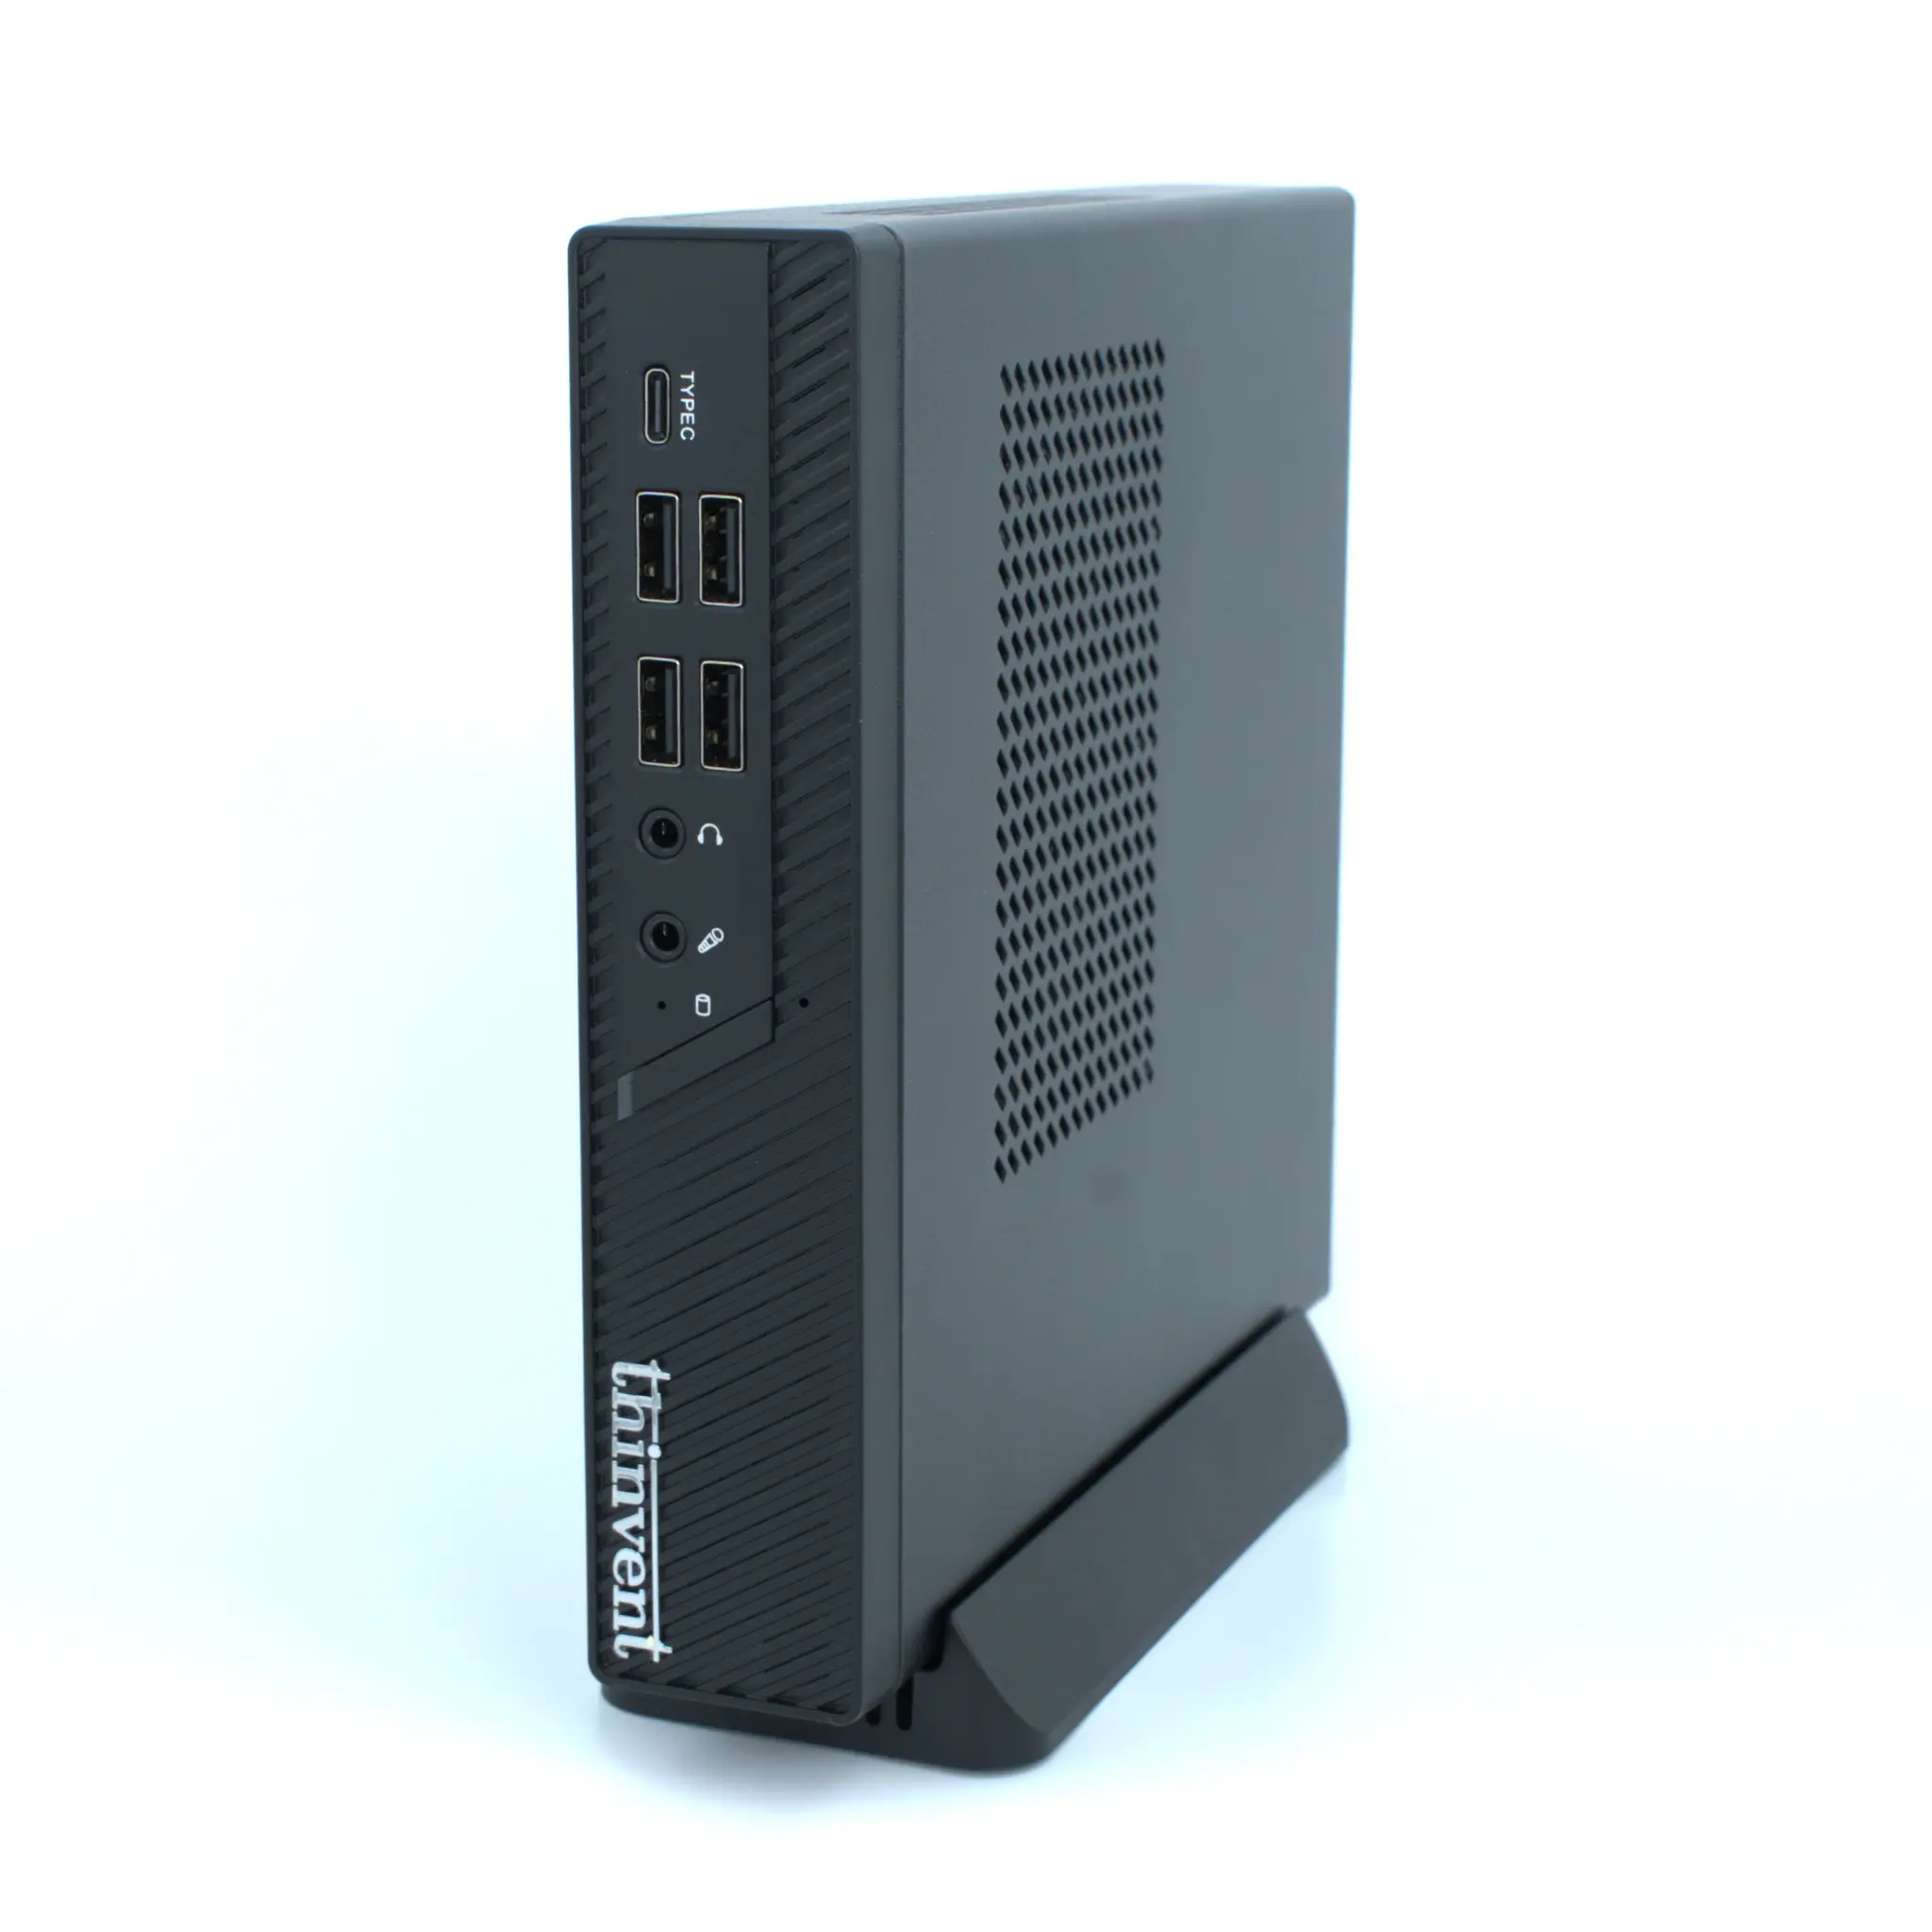
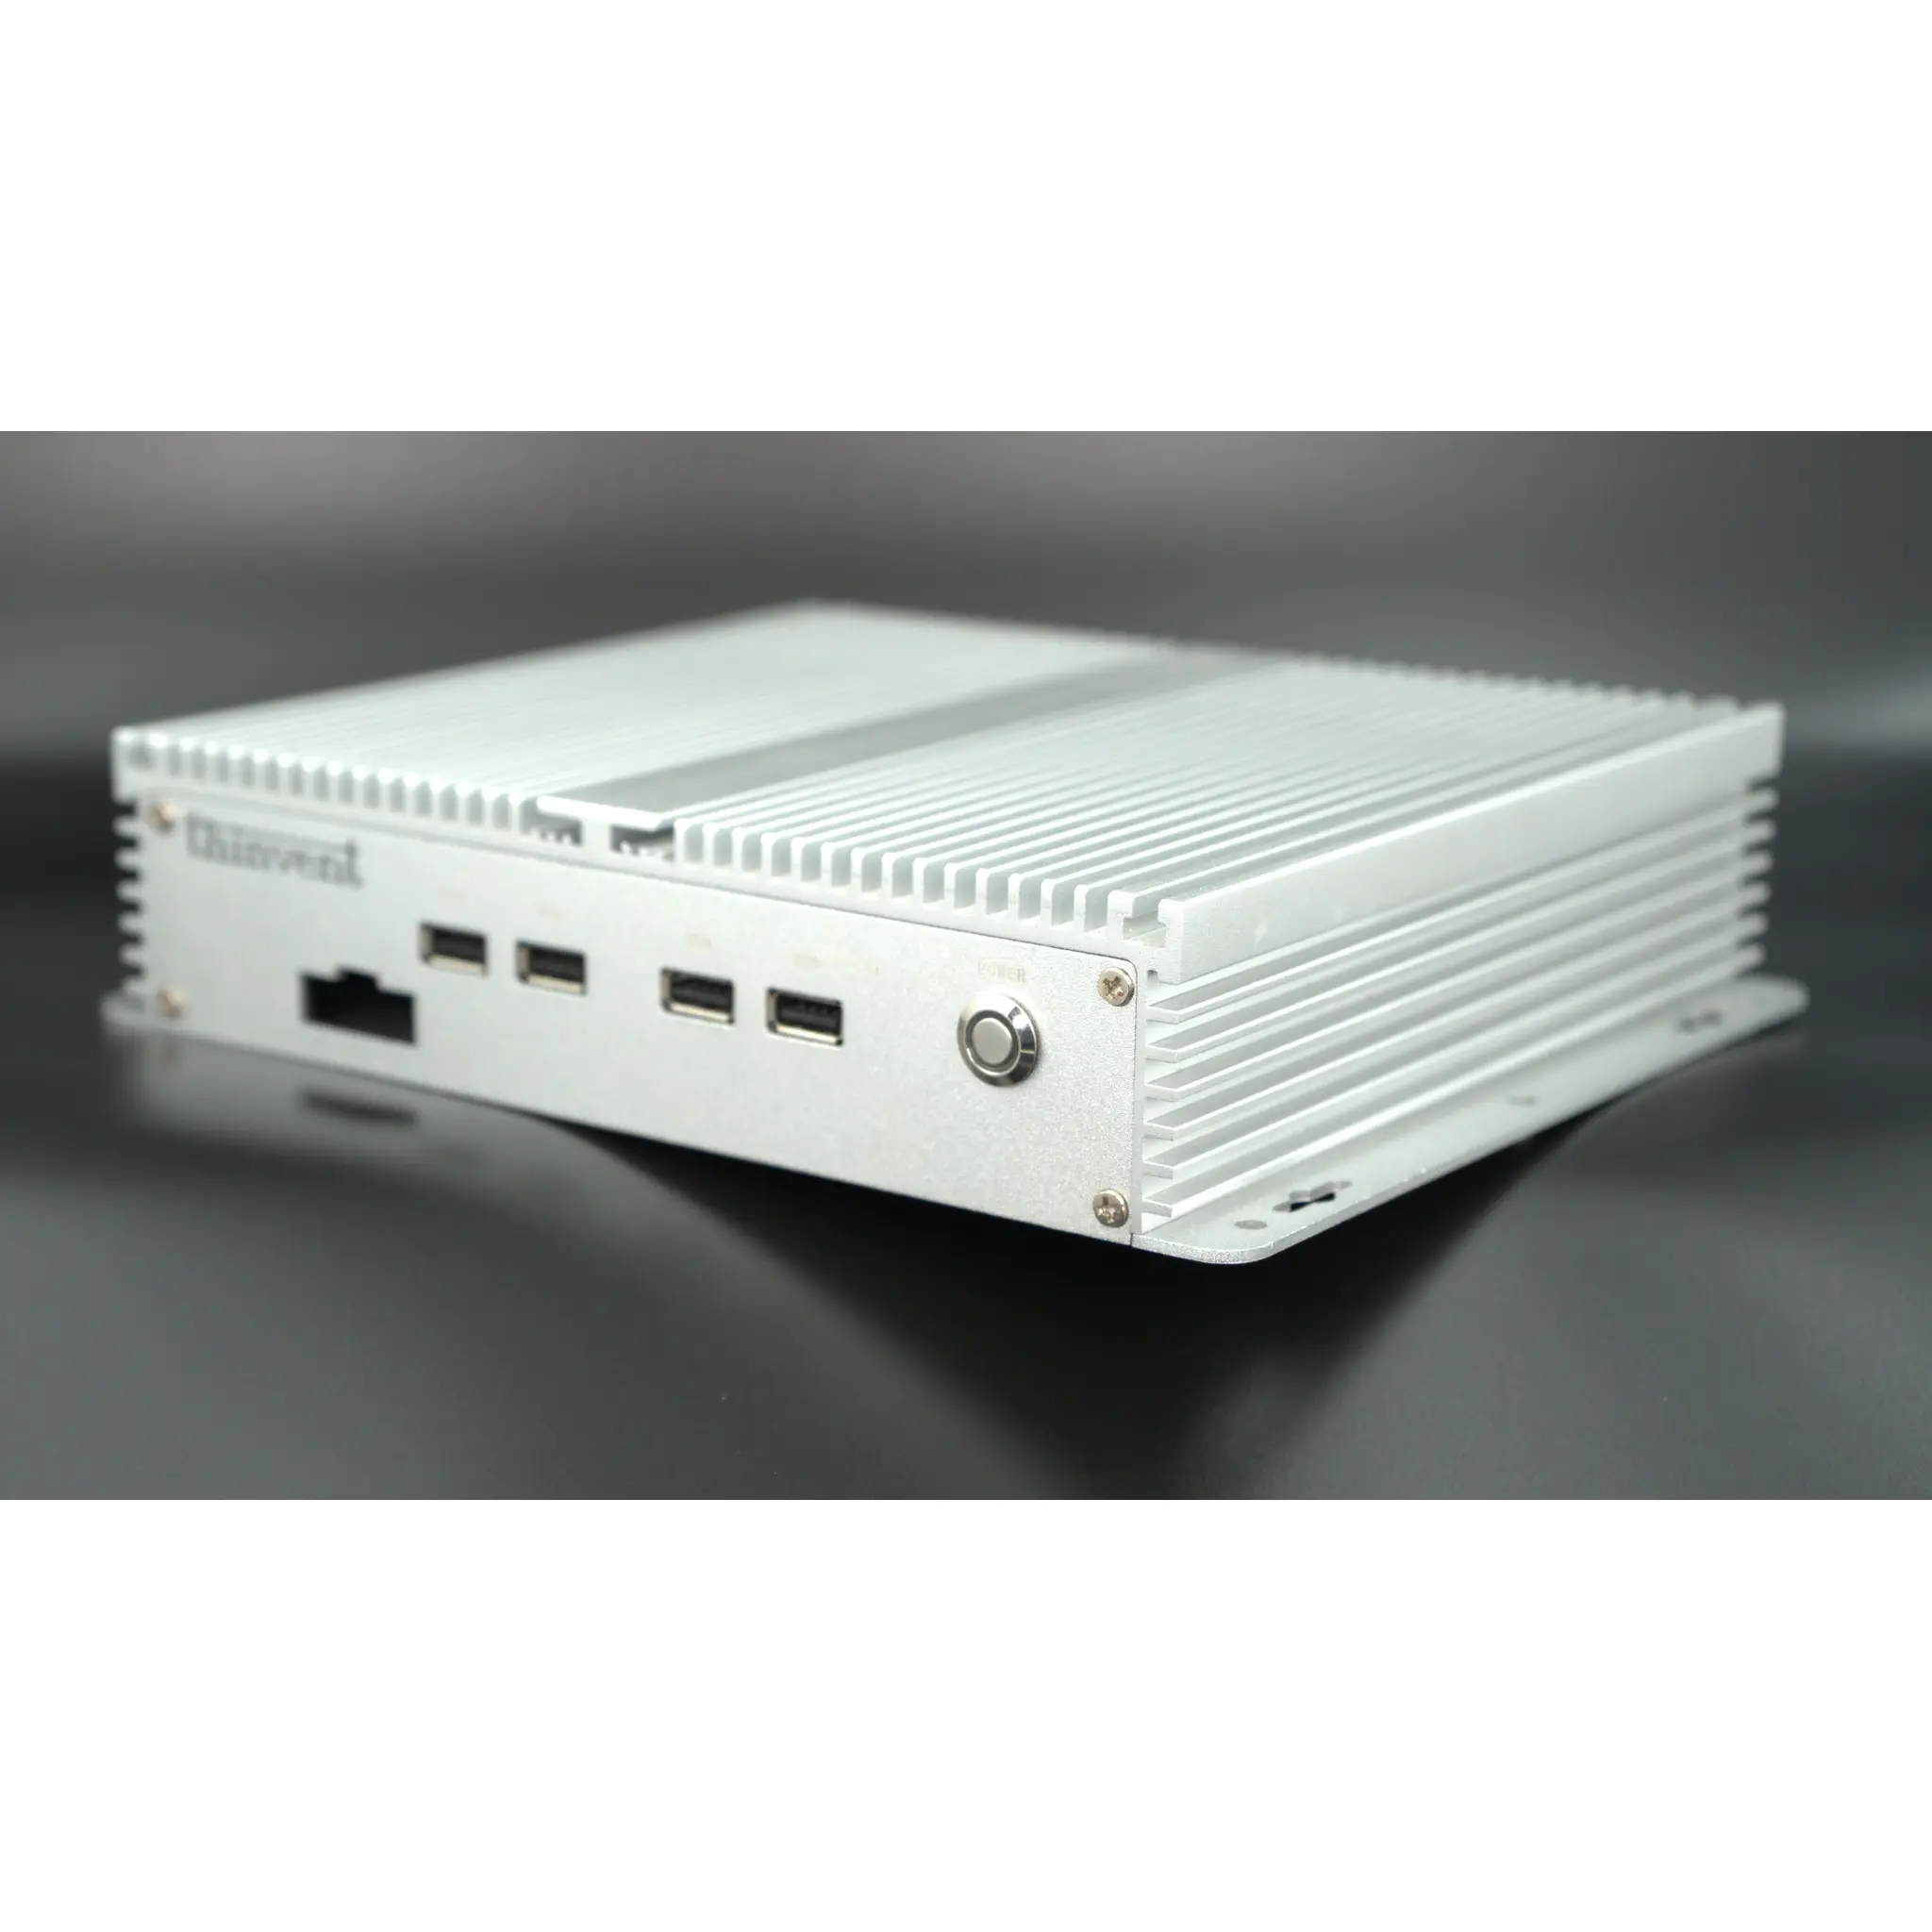
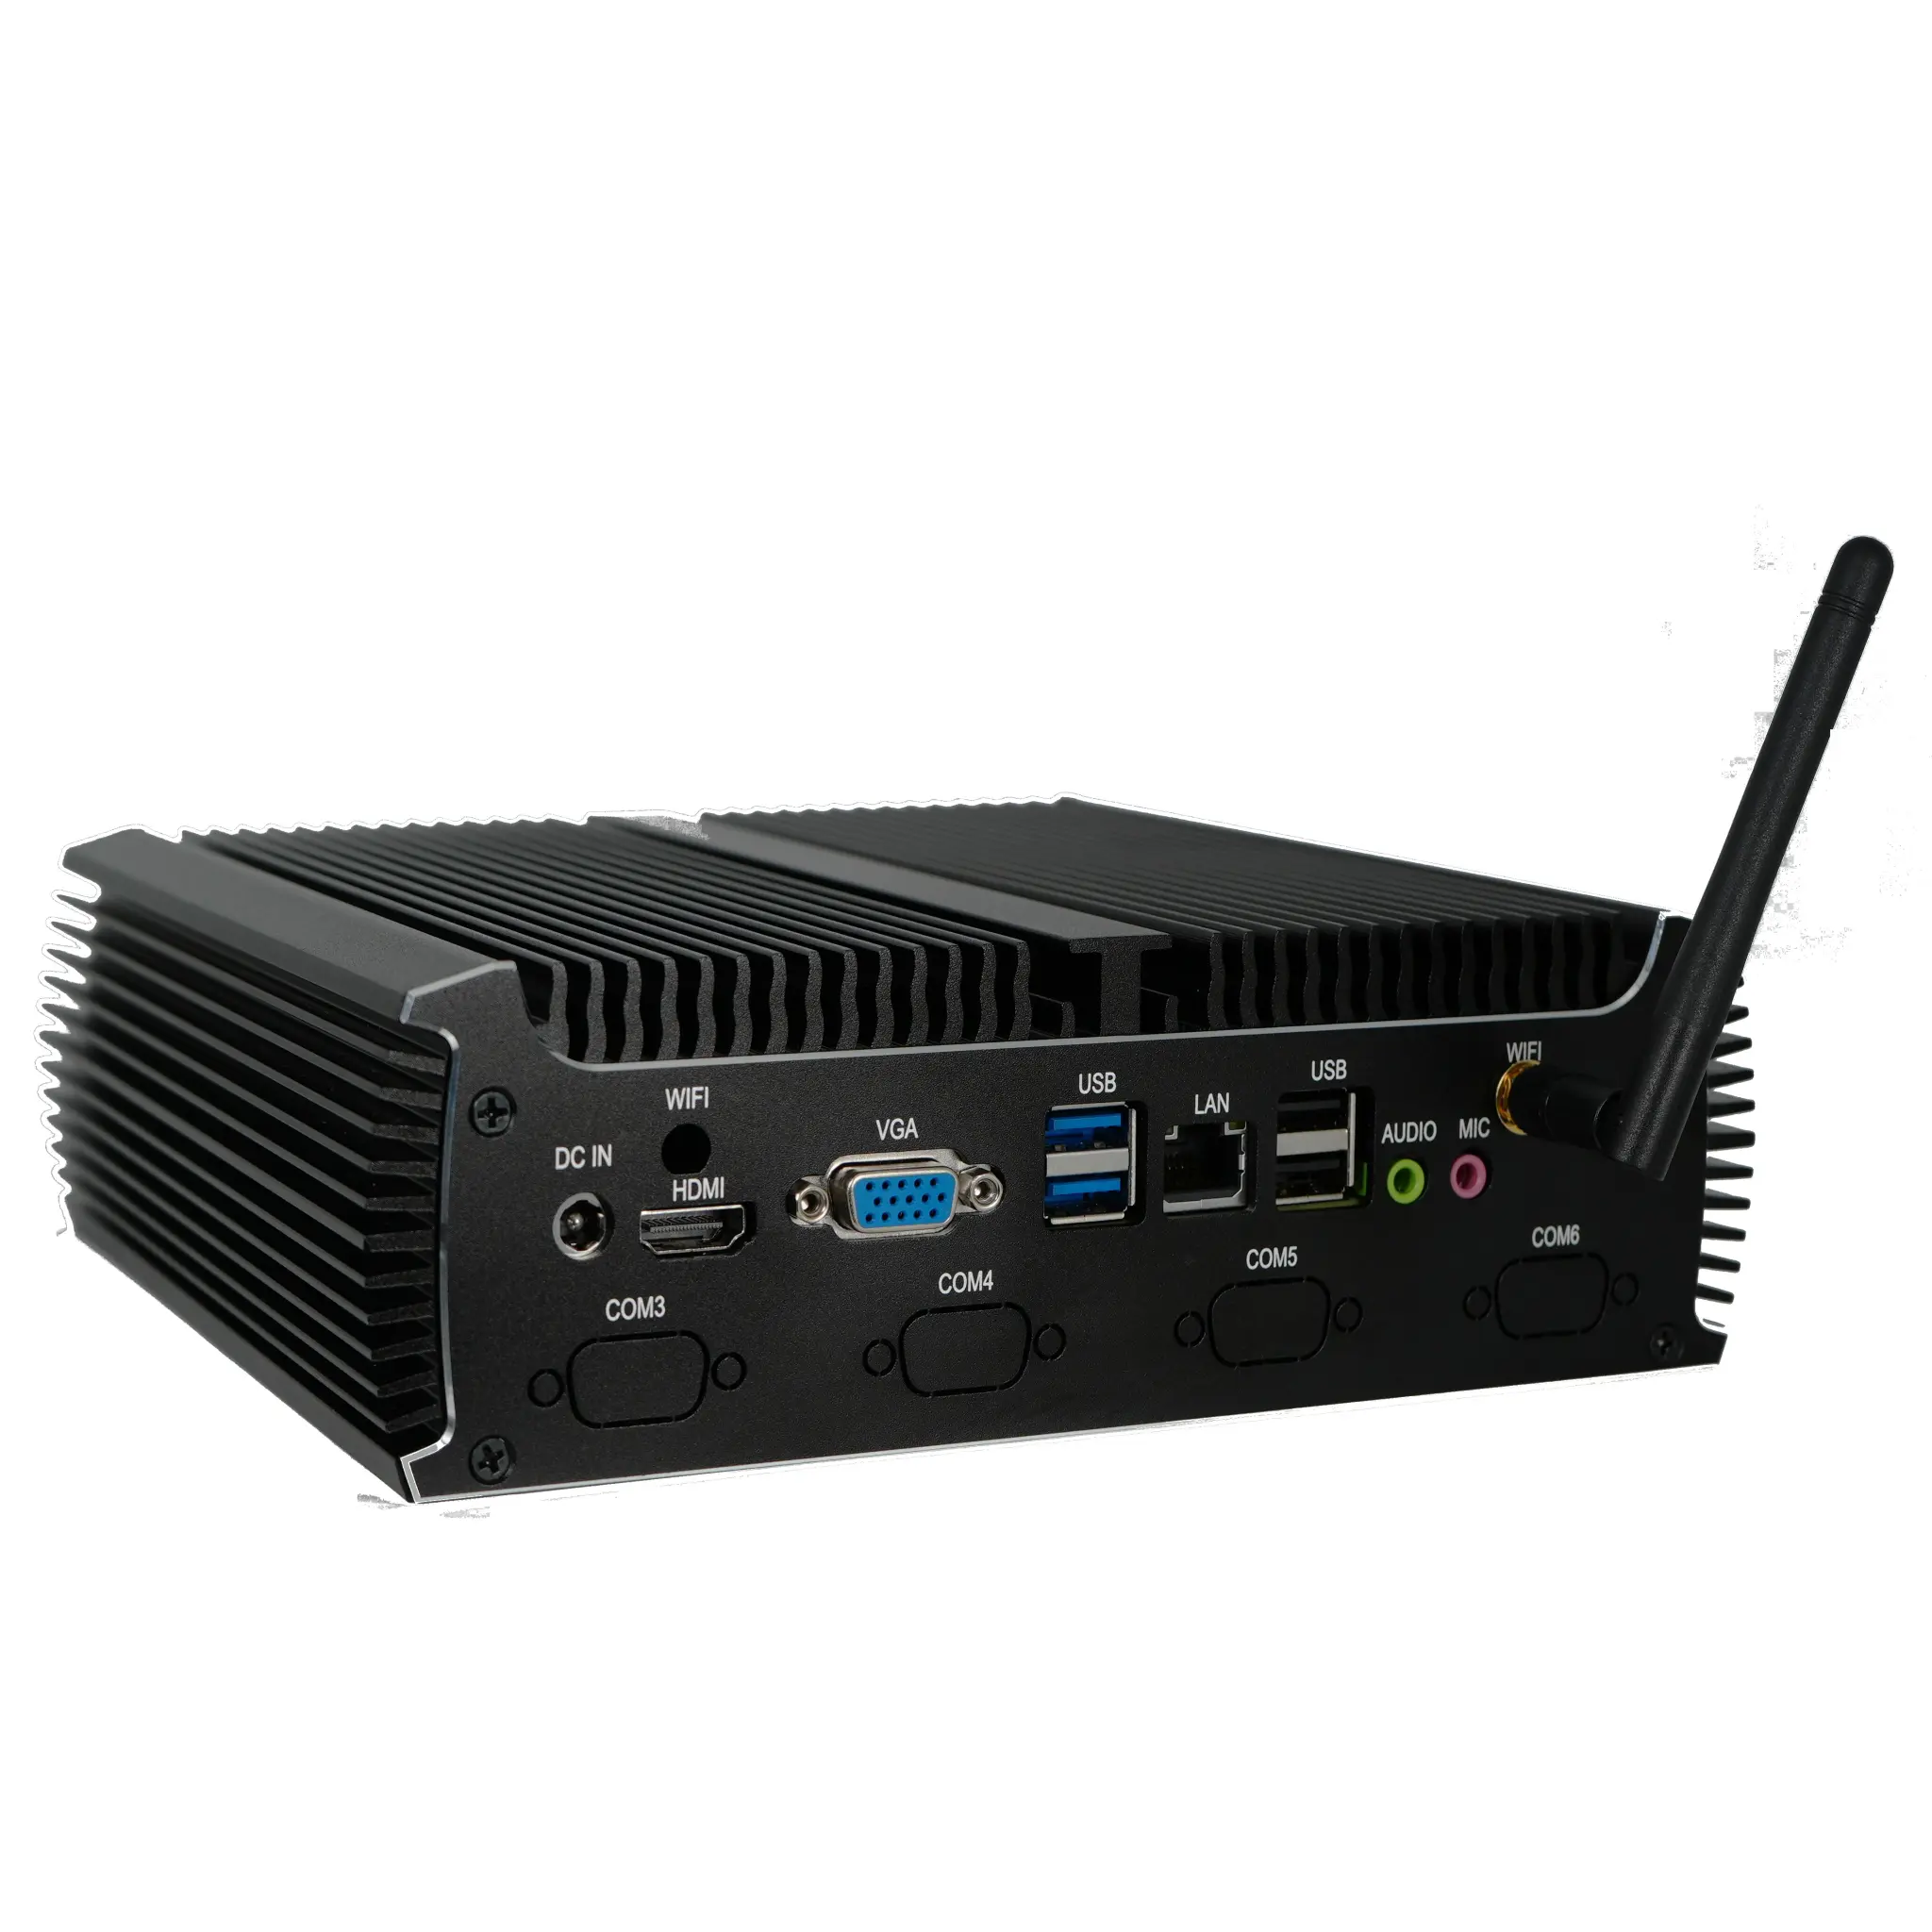
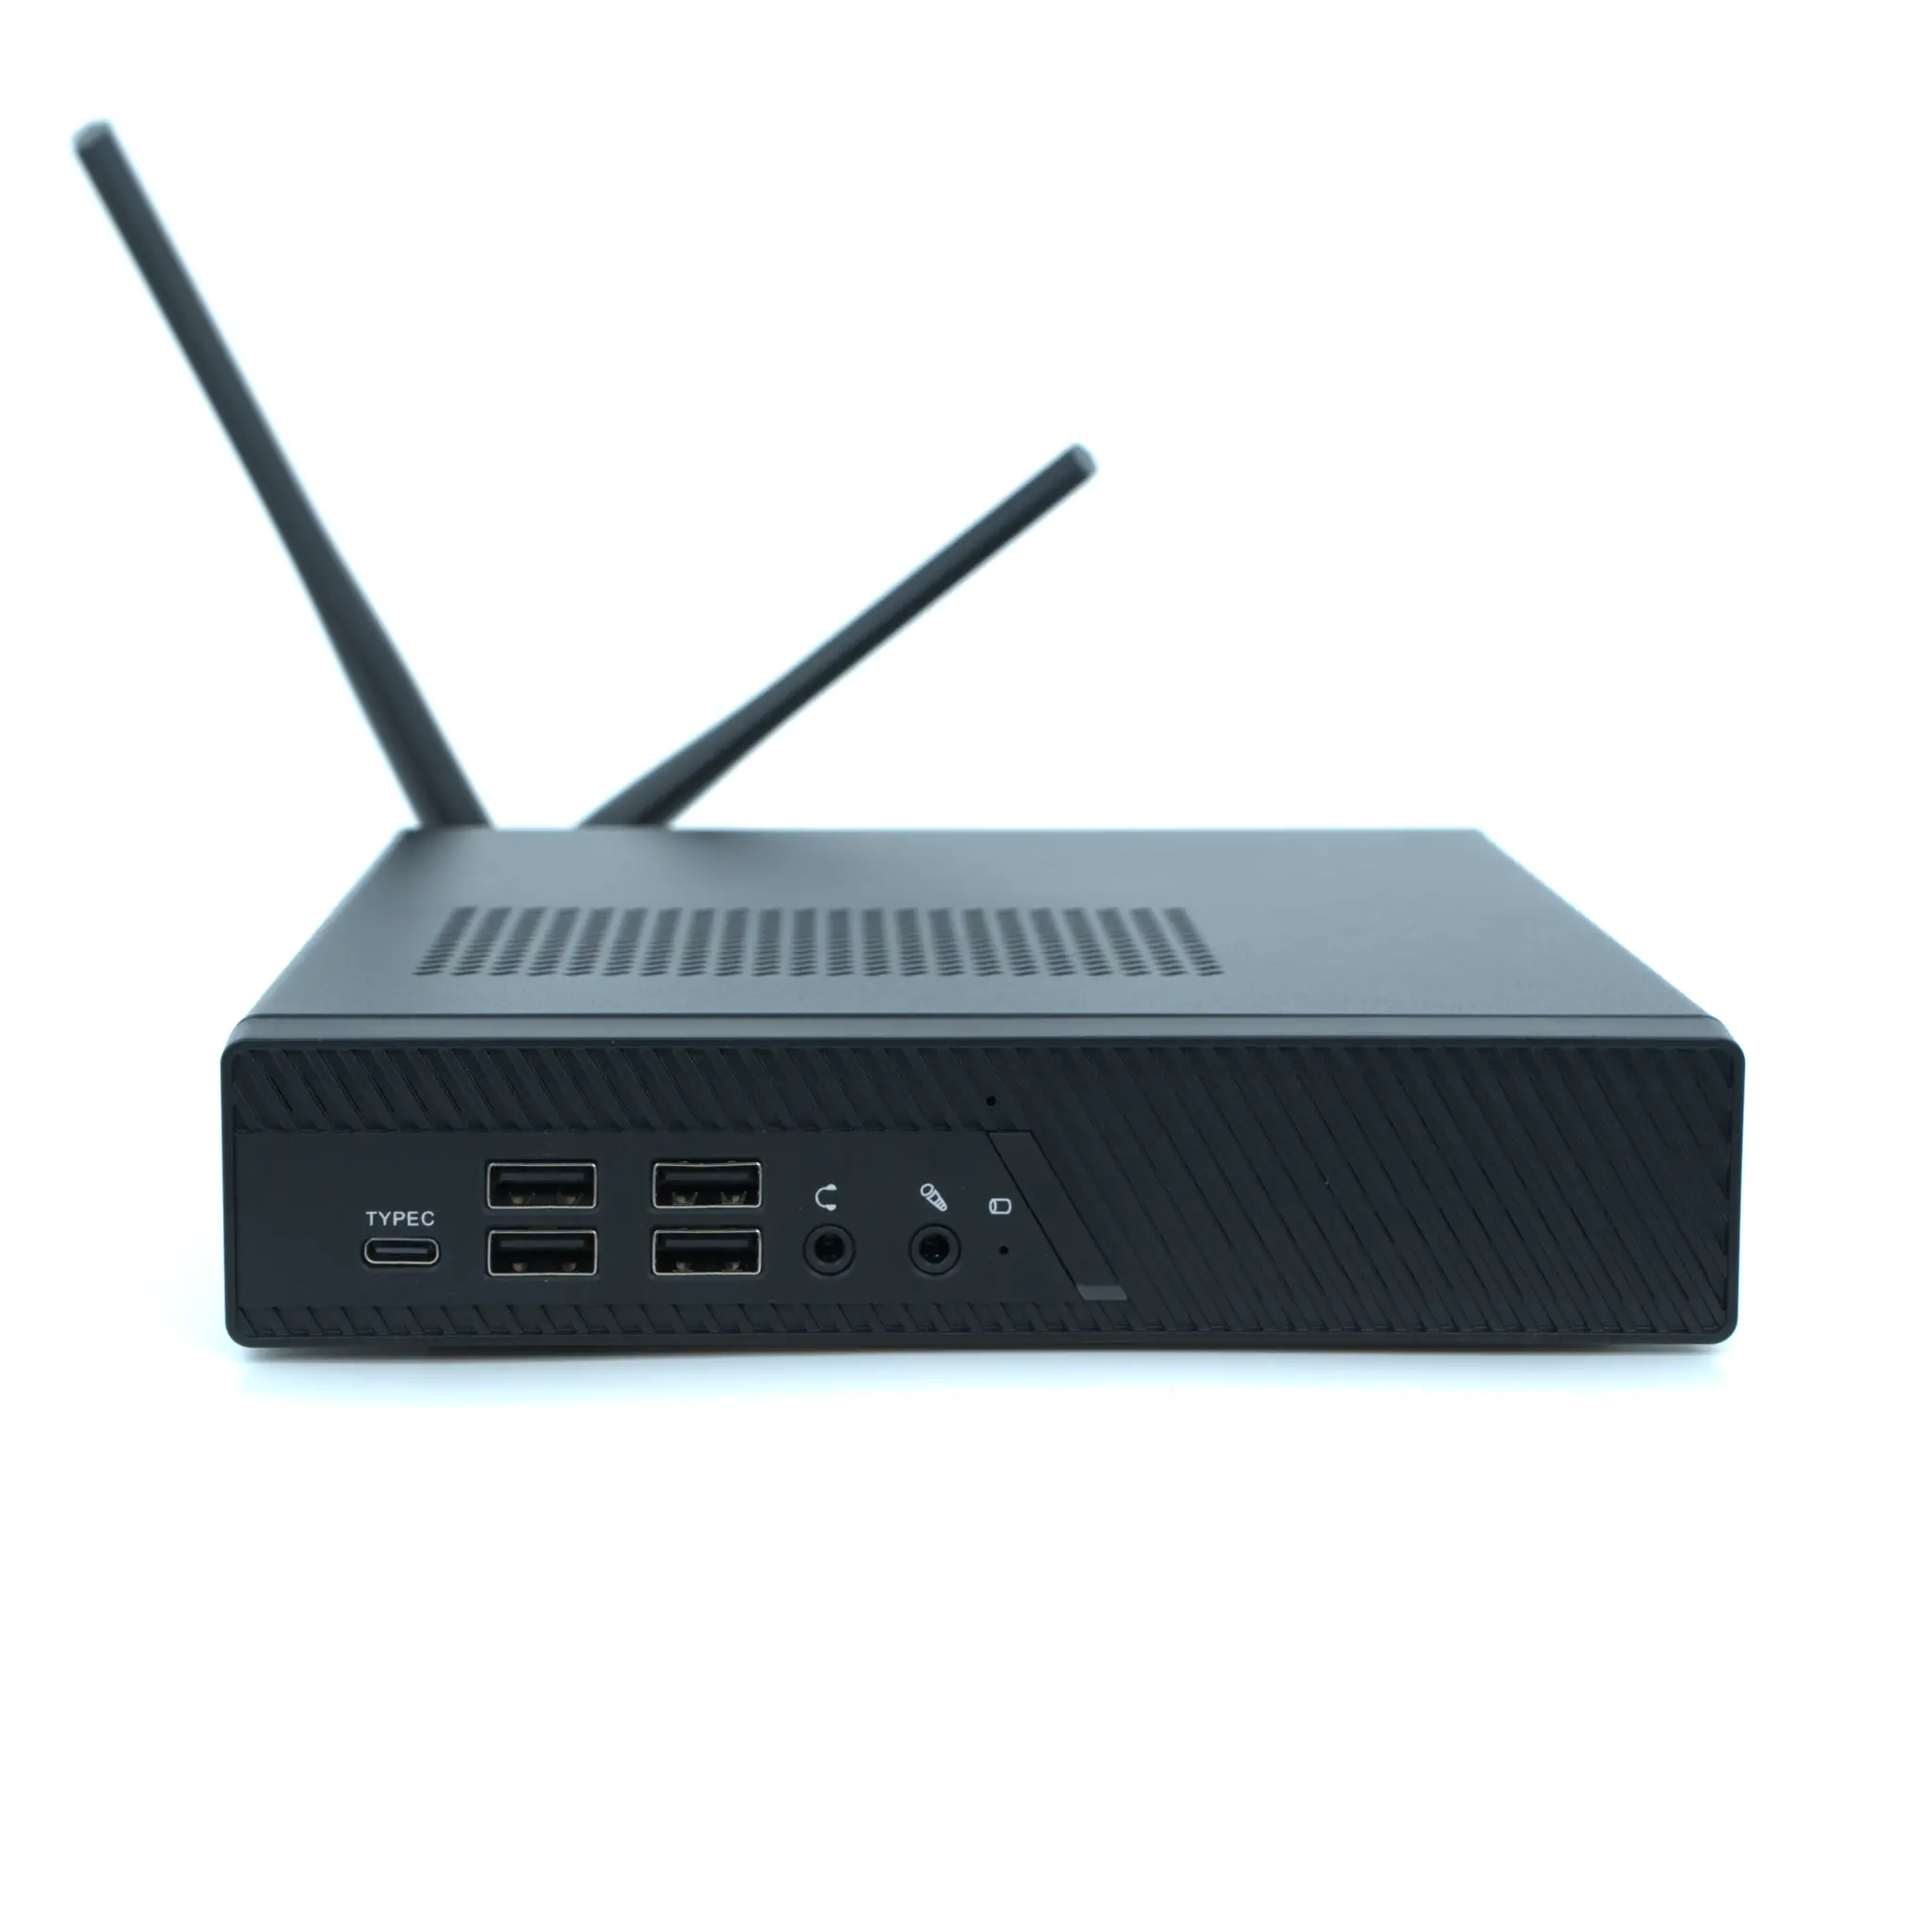
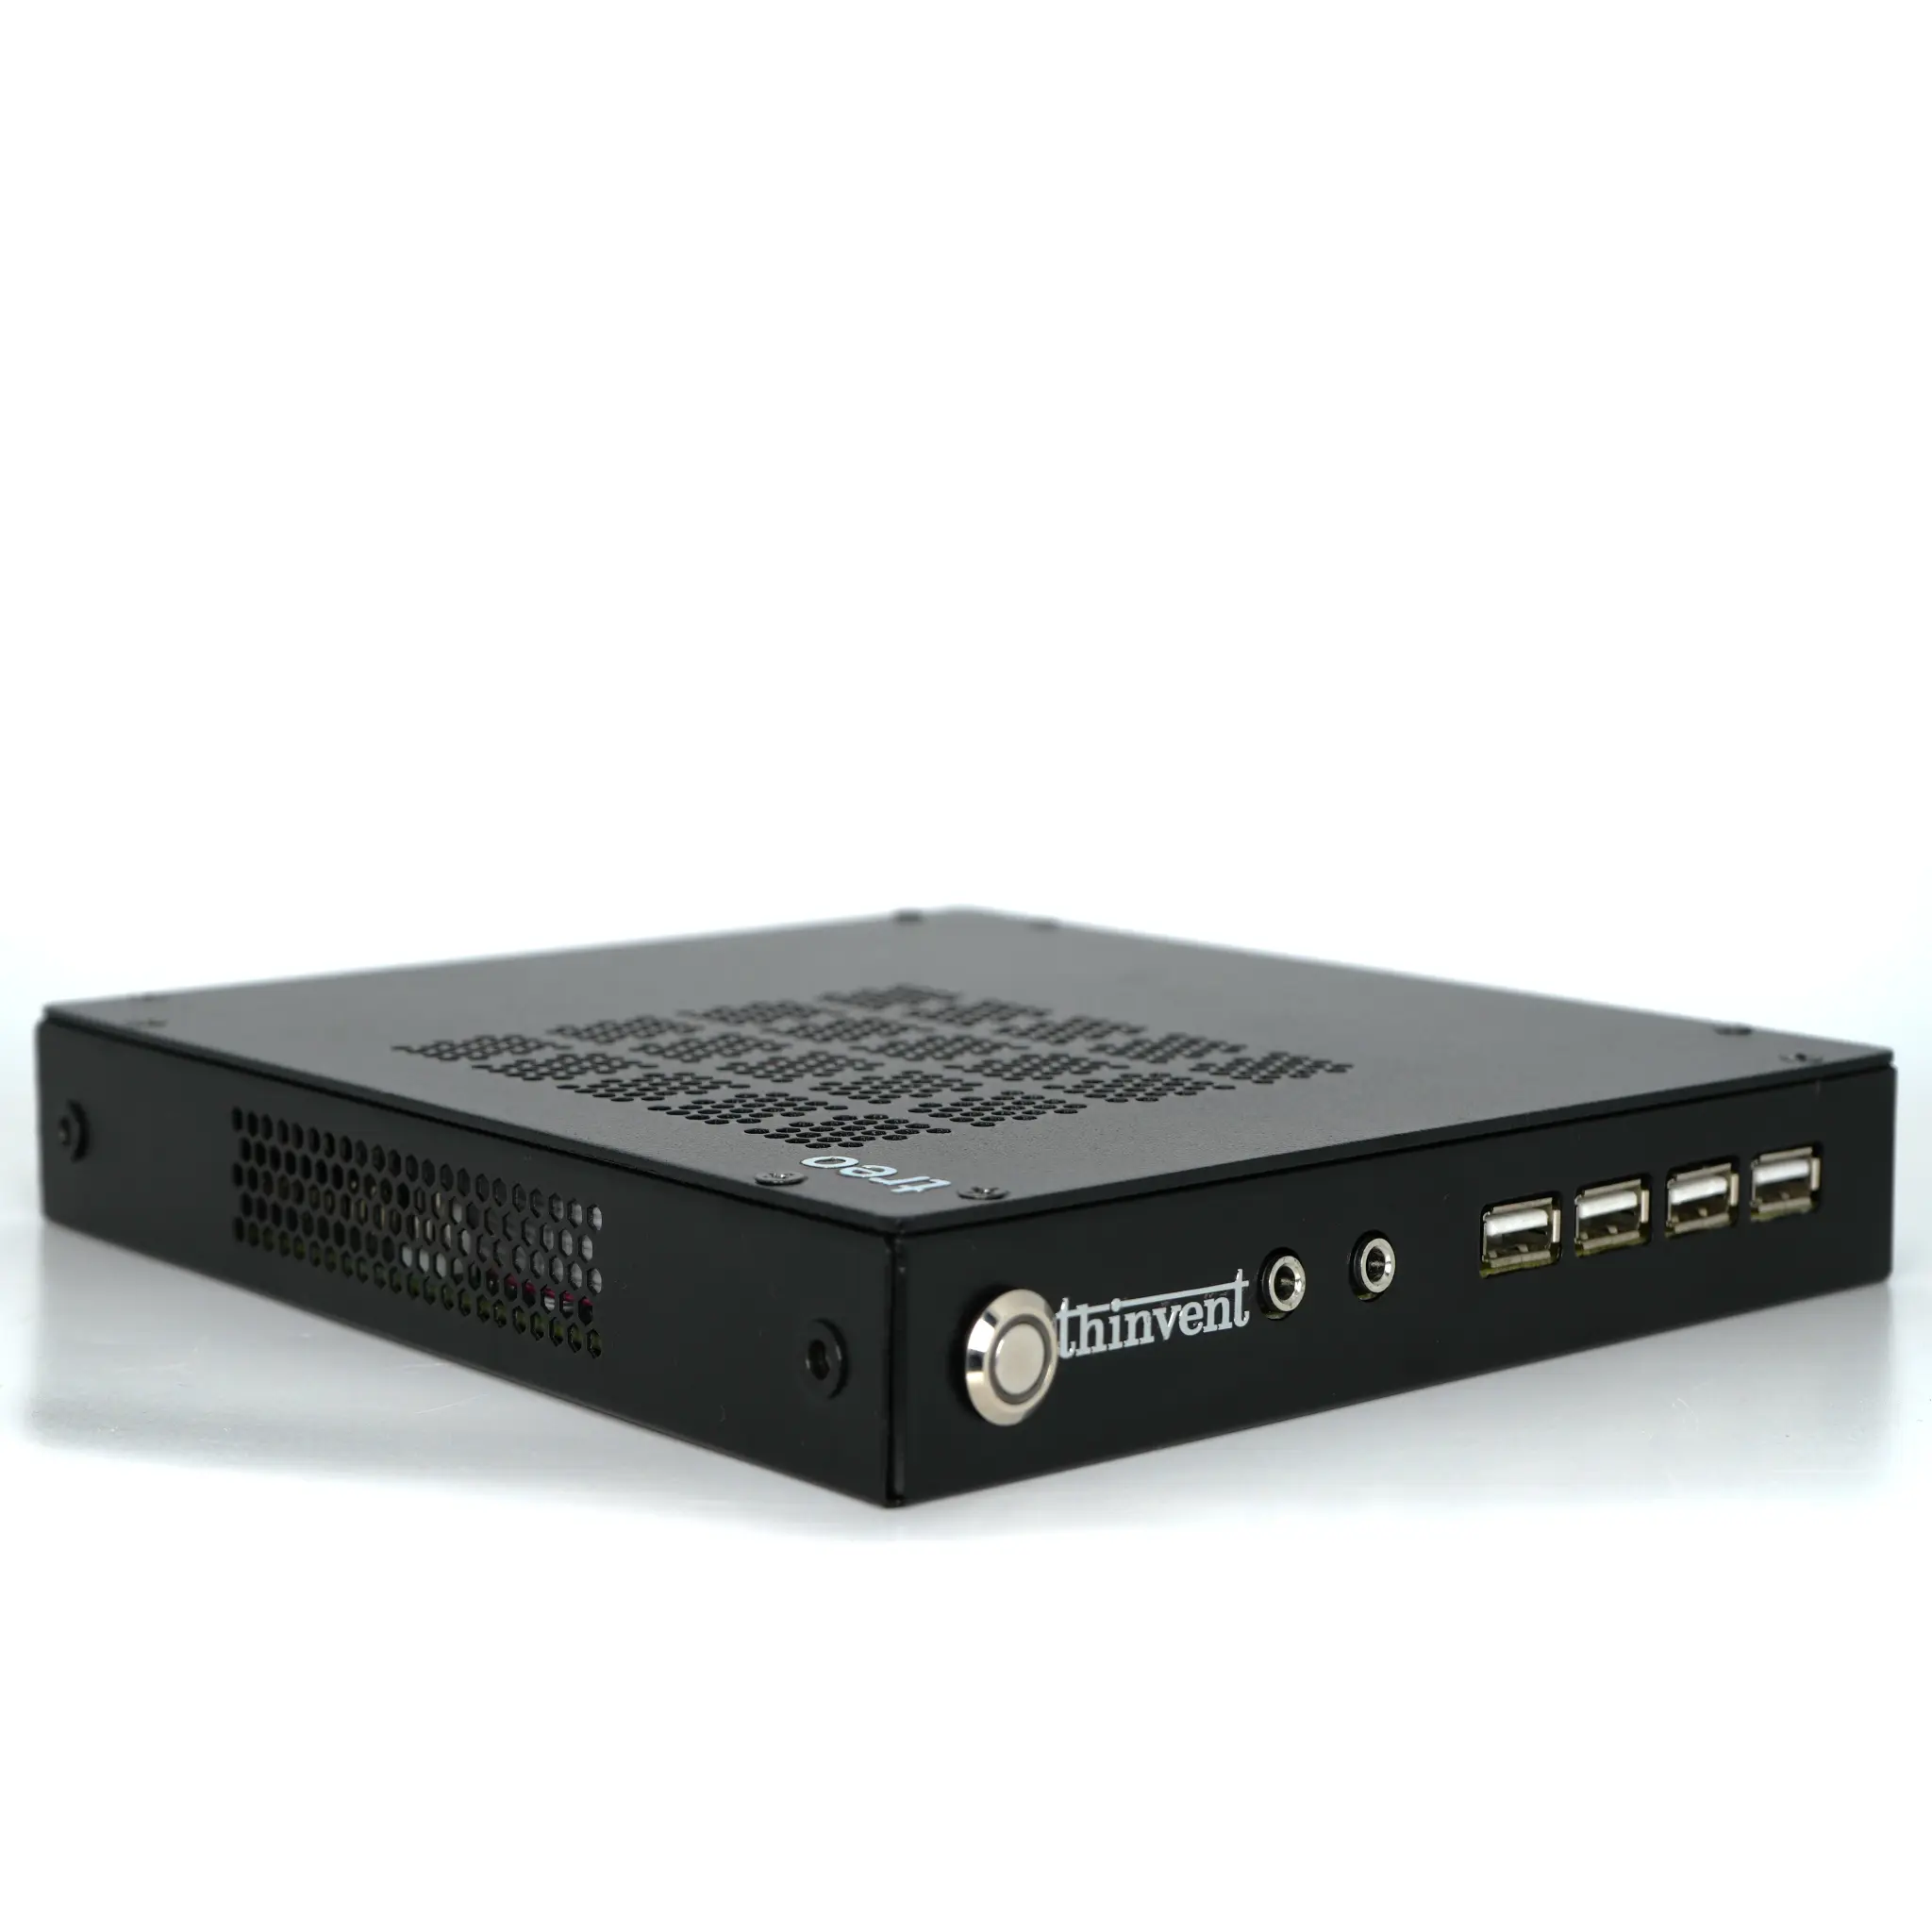
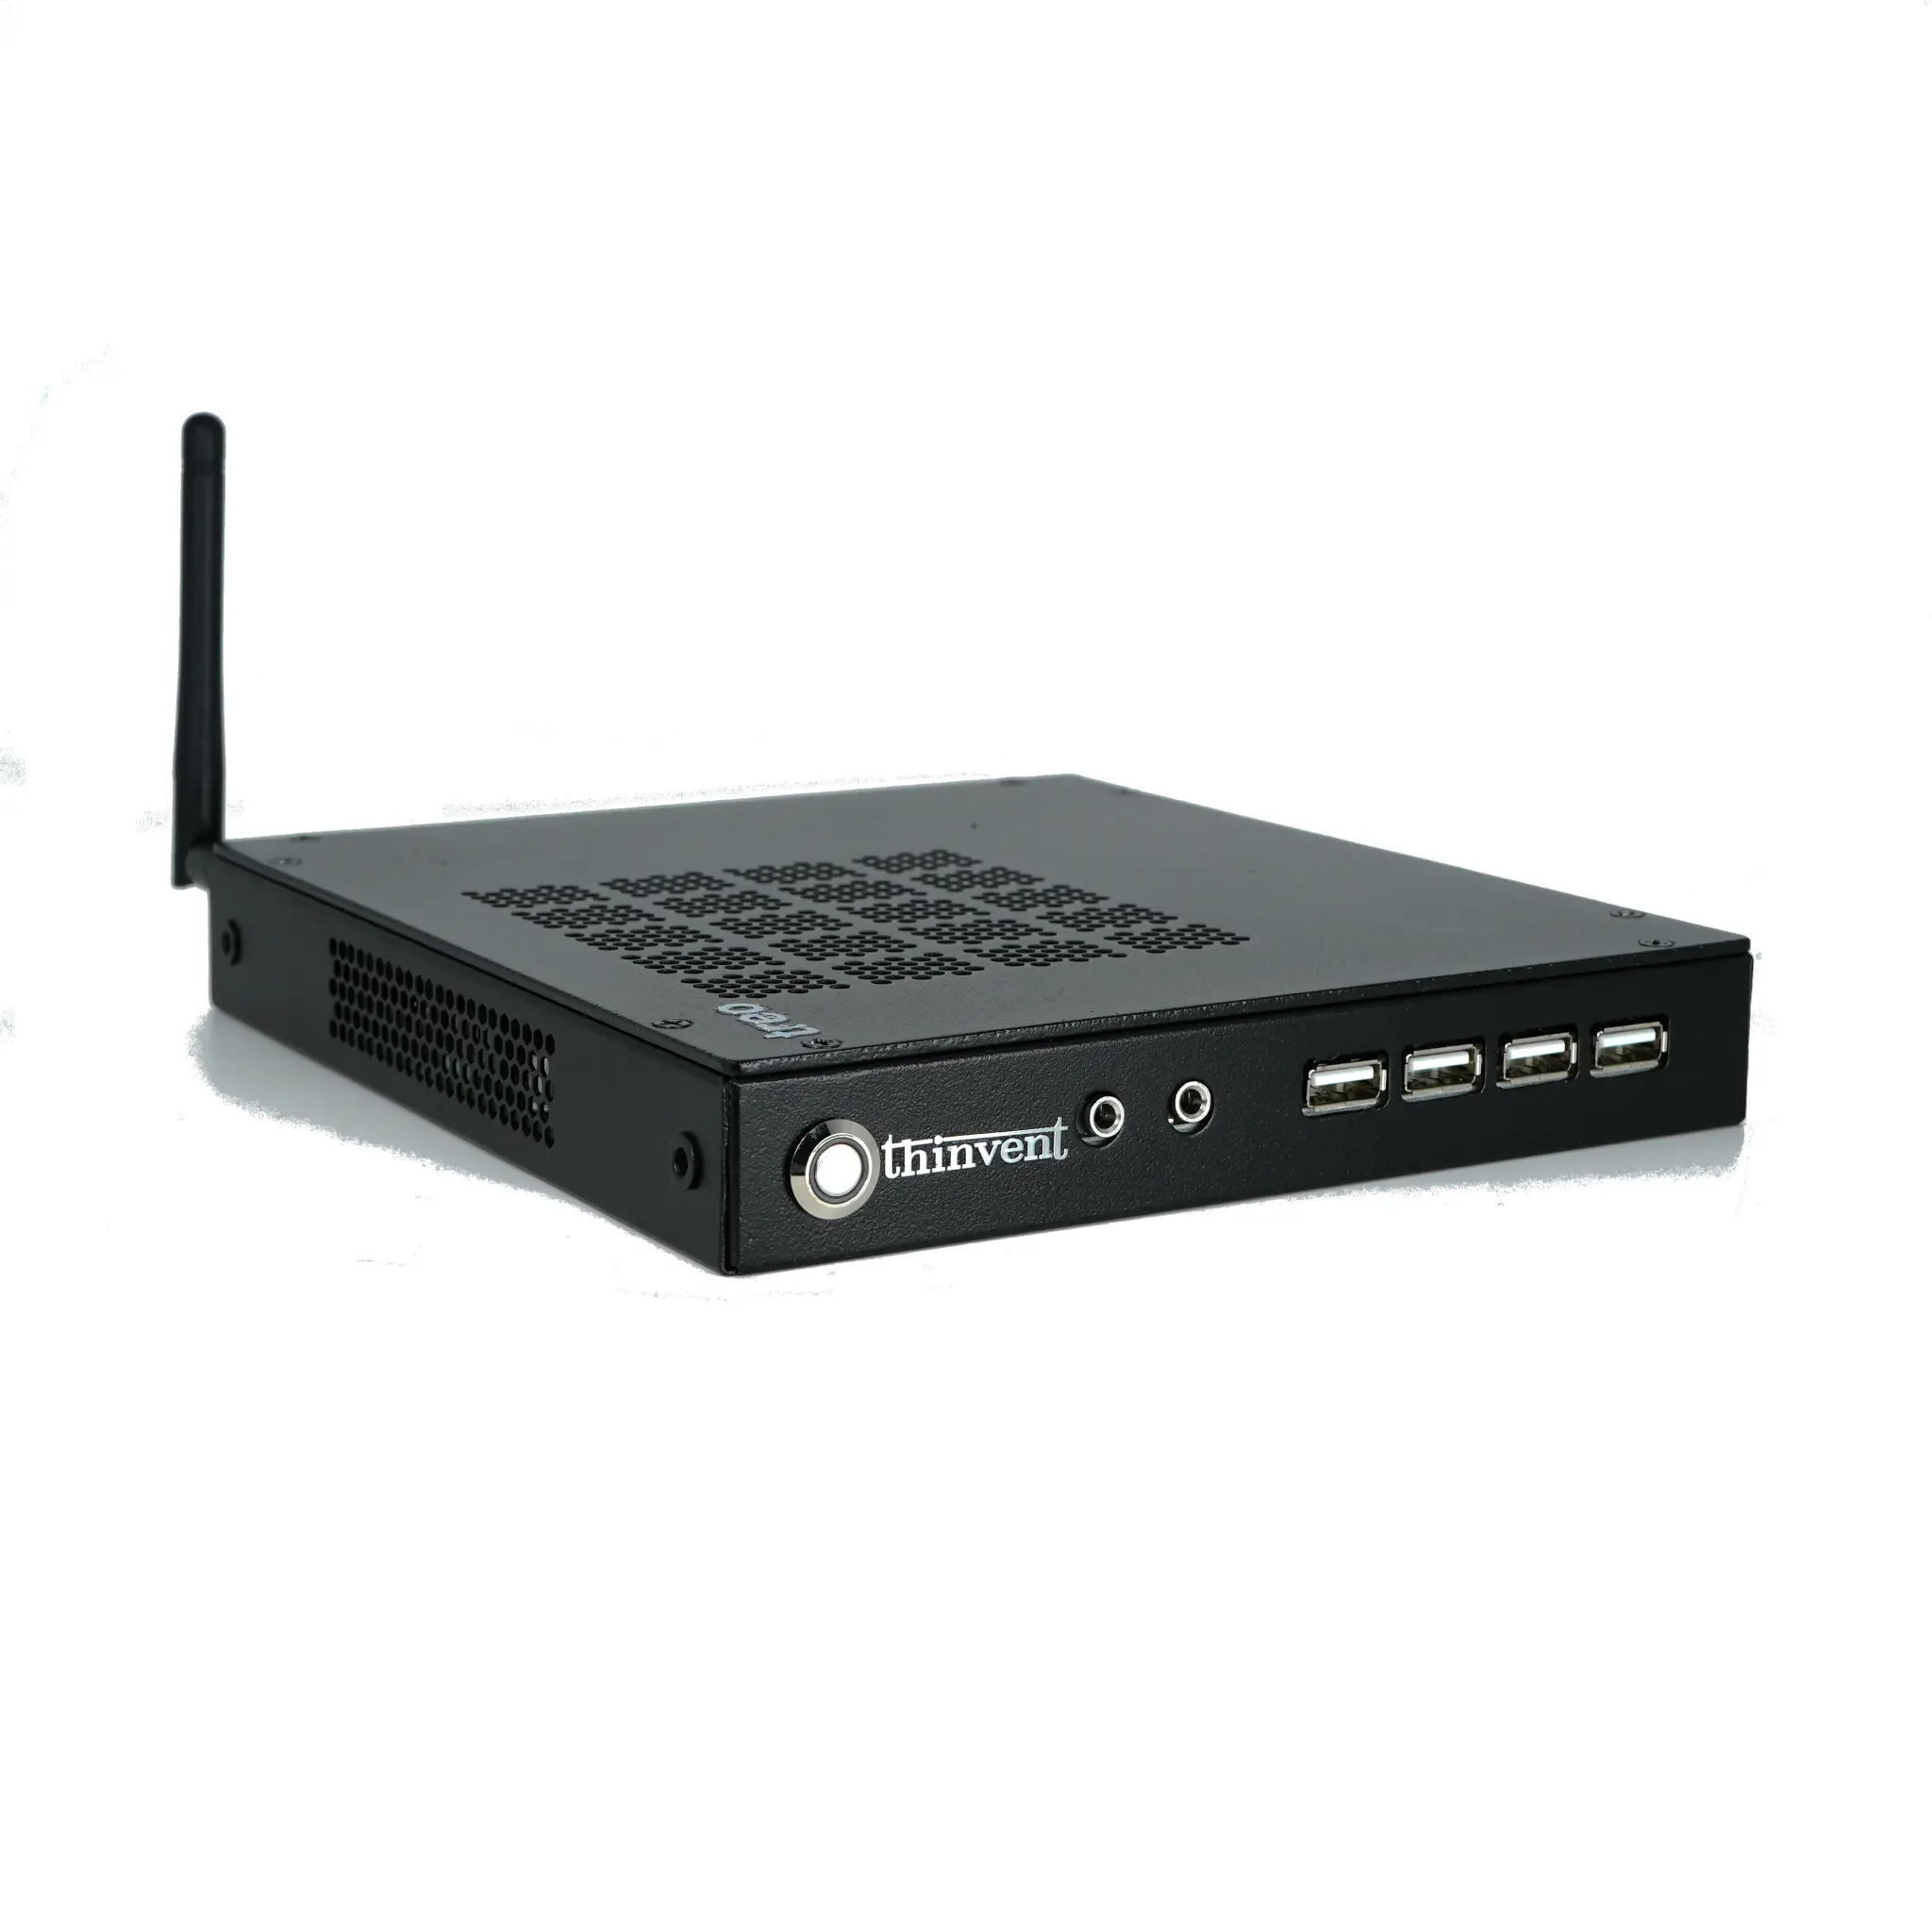
Thinvent integrates Trusted Platform Module 2.0 technology across its industrial computing portfolio, ensuring robust security for demanding environments. Our Aero Mini PC series, powered by Intel N100 processors (4 cores, up to 3.4 GHz), comes standard with TPM 2.0 support, making them ideal for secure deployments in retail, healthcare, and industrial settings. These systems are available with Windows 11 IoT, Windows 11 Pro, Ubuntu Linux, or Thinux™ Embedded Linux, all of which leverage TPM for enhanced security features like BitLocker drive encryption and Secure Boot. For applications requiring maximum data protection, Thinvent's TPM-ready mini PCs provide the hardware foundation for comprehensive security strategies without compromising on performance or reliability.