What is a Trusted Platform Module (TPM)?
A Trusted Platform Module (TPM) is a dedicated microcontroller designed to secure hardware by integrating cryptographic keys into devices. It provides a hardware-based root of trust, enabling secure generation, storage, and management of sensitive data like encryption keys, digital certificates, and passwords. Unlike software-based security, a TPM chip is physically attached to the motherboard, making it far more resistant to tampering and remote software attacks. This technology is crucial for implementing robust security features such as device identity verification, platform integrity checking, and full-disk encryption.
Key Specifications and Security Functions
A TPM chip performs several critical security functions. Its core capabilities include secure cryptographic key generation and storage, remote attestation (proving a system's state is trustworthy), and binding/sealing data to a specific hardware configuration. Modern TPM 2.0 modules support advanced encryption algorithms and are a foundational requirement for security standards like Windows 11. Key specifications involve the type of TPM (discrete, firmware, or integrated), compliance with international standards (ISO/IEC 11889), and the supported cryptographic suites for hashing and asymmetric encryption.
Applications and Use Cases for TPM Security
TPM security is essential across various demanding sectors. In industrial automation and IoT, it secures machine-to-machine communication and protects intellectual property on the factory floor. For digital signage and kiosks, it prevents unauthorized OS or application changes and secures transactions. In healthcare and finance, it enables strong full-disk encryption to protect sensitive patient or customer data, ensuring compliance with regulations like HIPAA and GDPR. It is also vital for secure network booting, zero-trust architectures, and creating secure digital workspaces for remote access.
TPM Implementation in Computing Devices
TPM functionality can be implemented in different ways, influencing the security level and application suitability.
| Implementation Type | Description | Typical Use Case |
|---|---|---|
| Discrete TPM (dTPM) | A dedicated, physical chip on the motherboard. Offers the highest level of physical security and isolation. | High-security industrial PCs, financial terminals, government systems. |
| Firmware TPM (fTPM) | A firmware-based solution that runs in a trusted execution environment of a processor (e.g., Intel PTT, AMD fTPM). | Consumer and commercial mini PCs, laptops, where cost and space are constraints. |
| Integrated TPM | Security functionality integrated directly into a main processor or chipset. | Modern system-on-chips (SoCs) for embedded and mobile devices. |
Thinvent Products with TPM Security Solutions
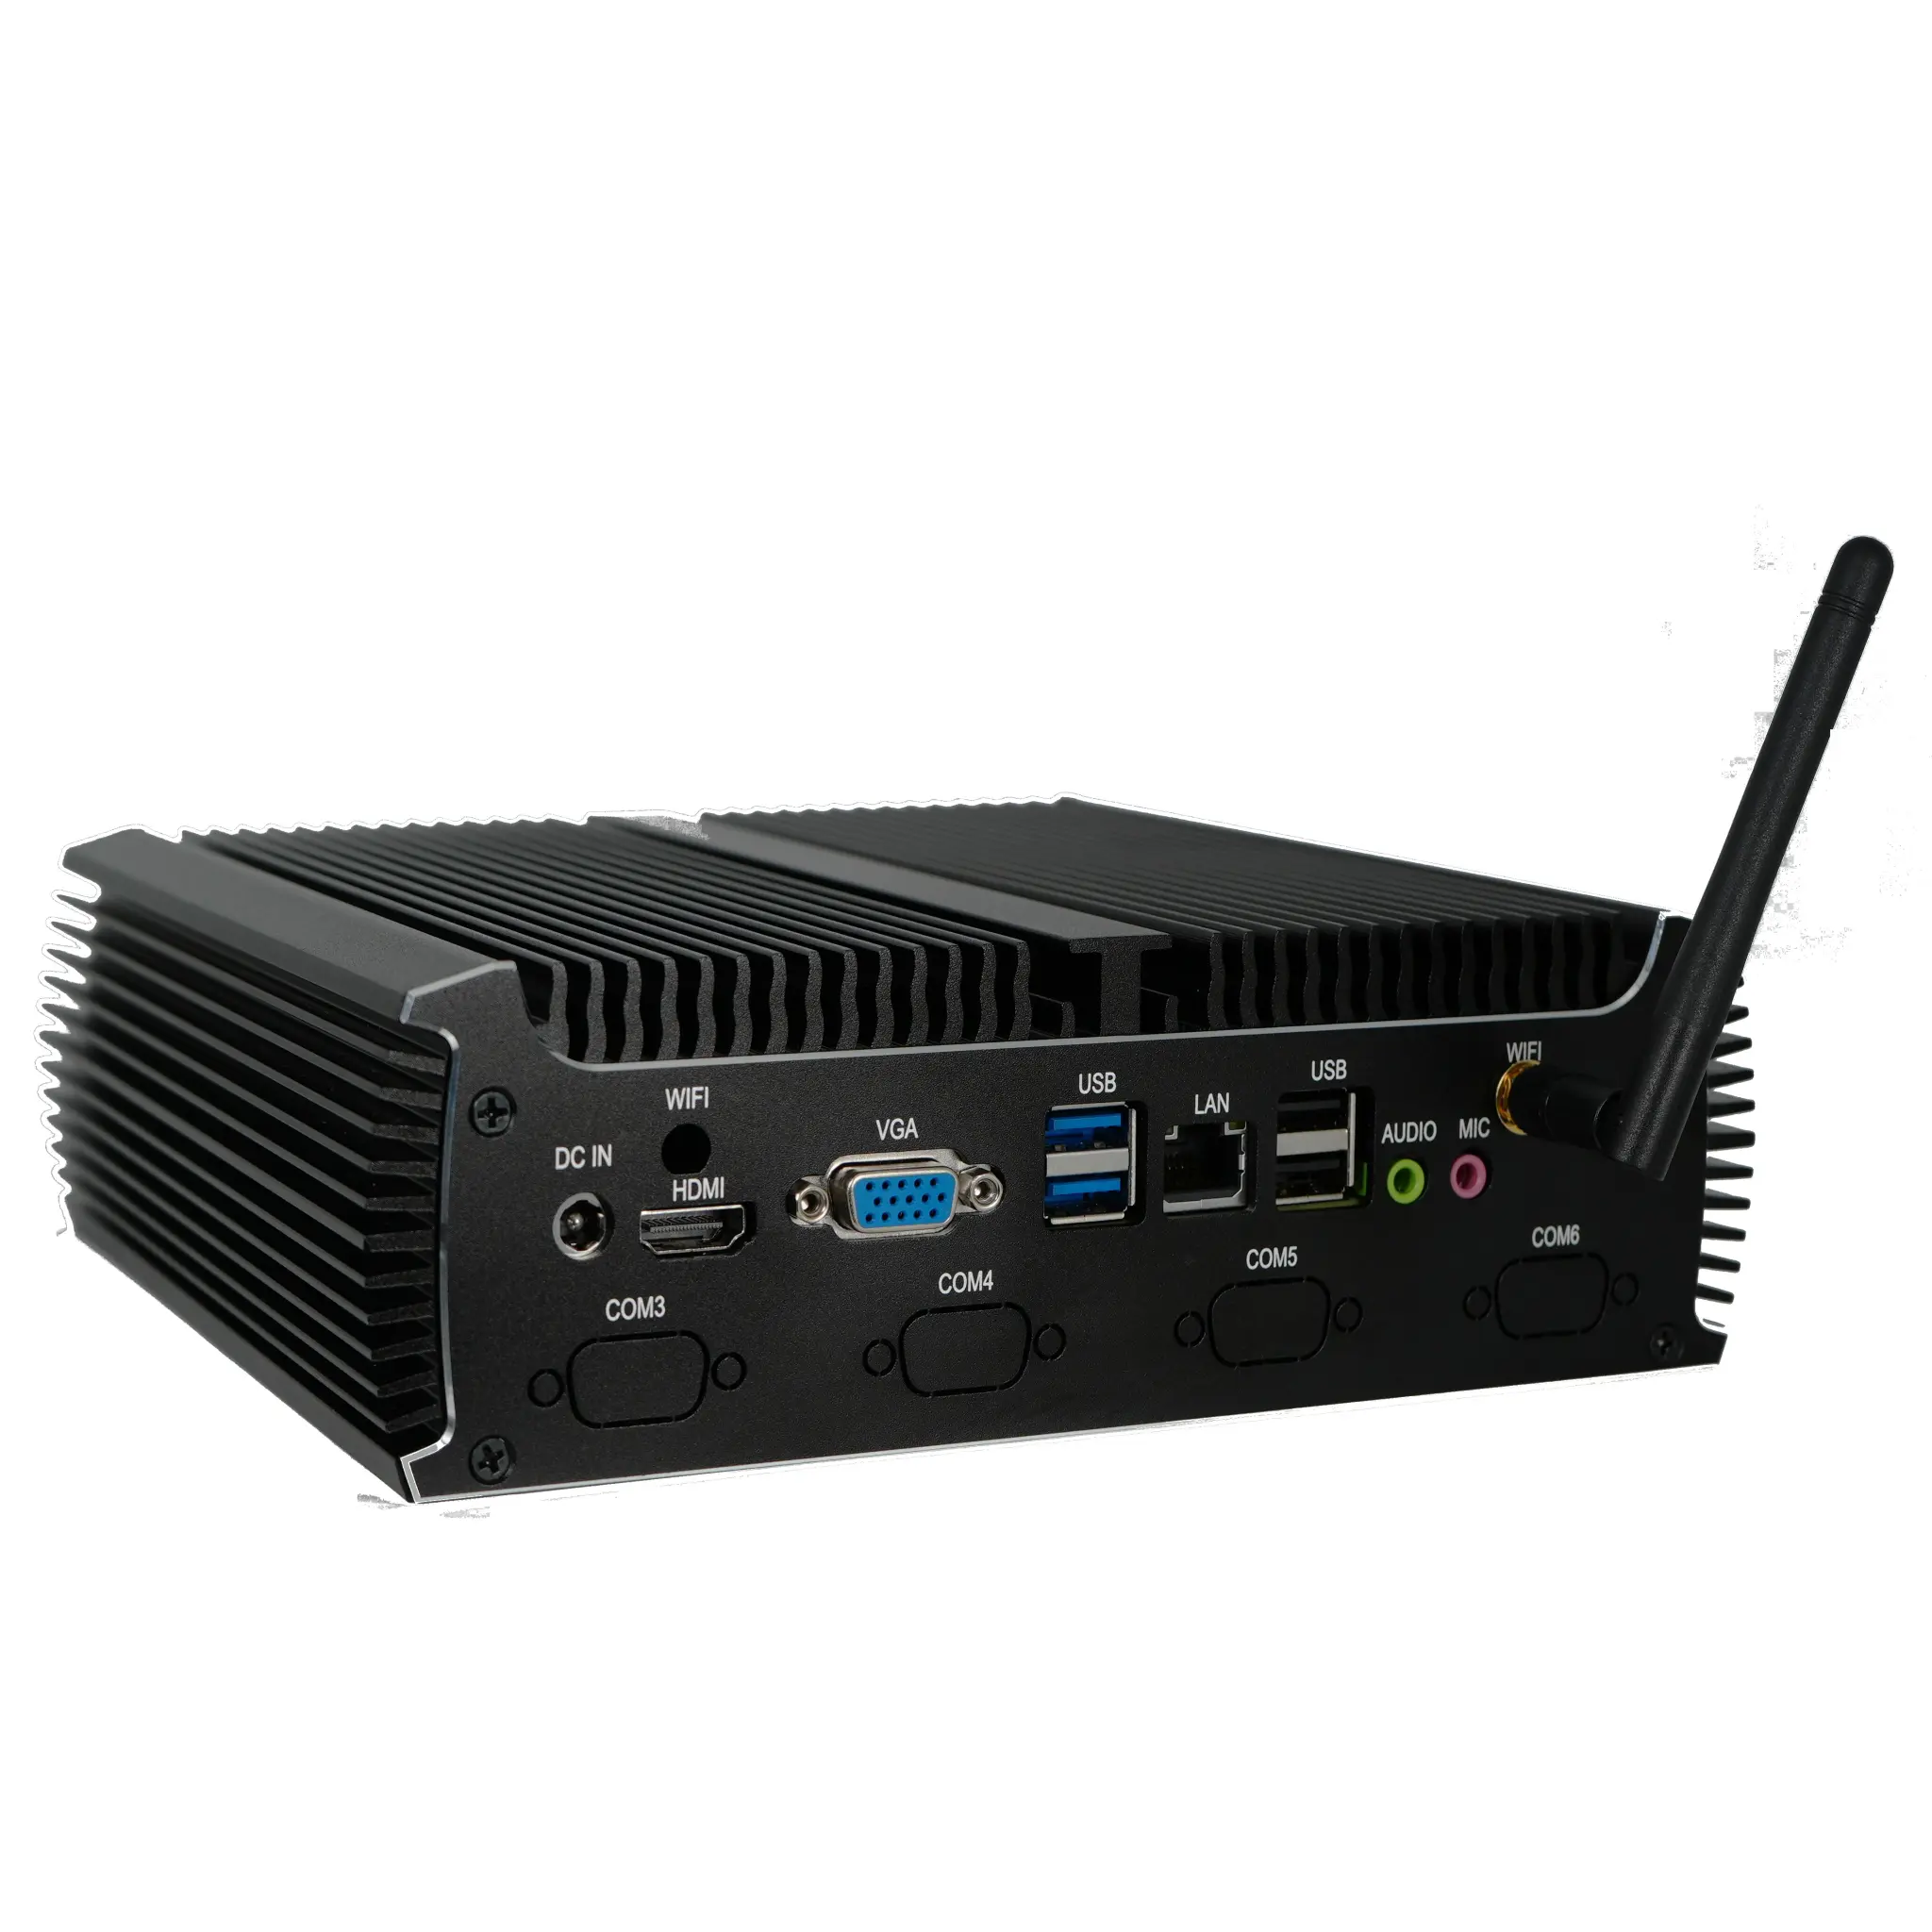
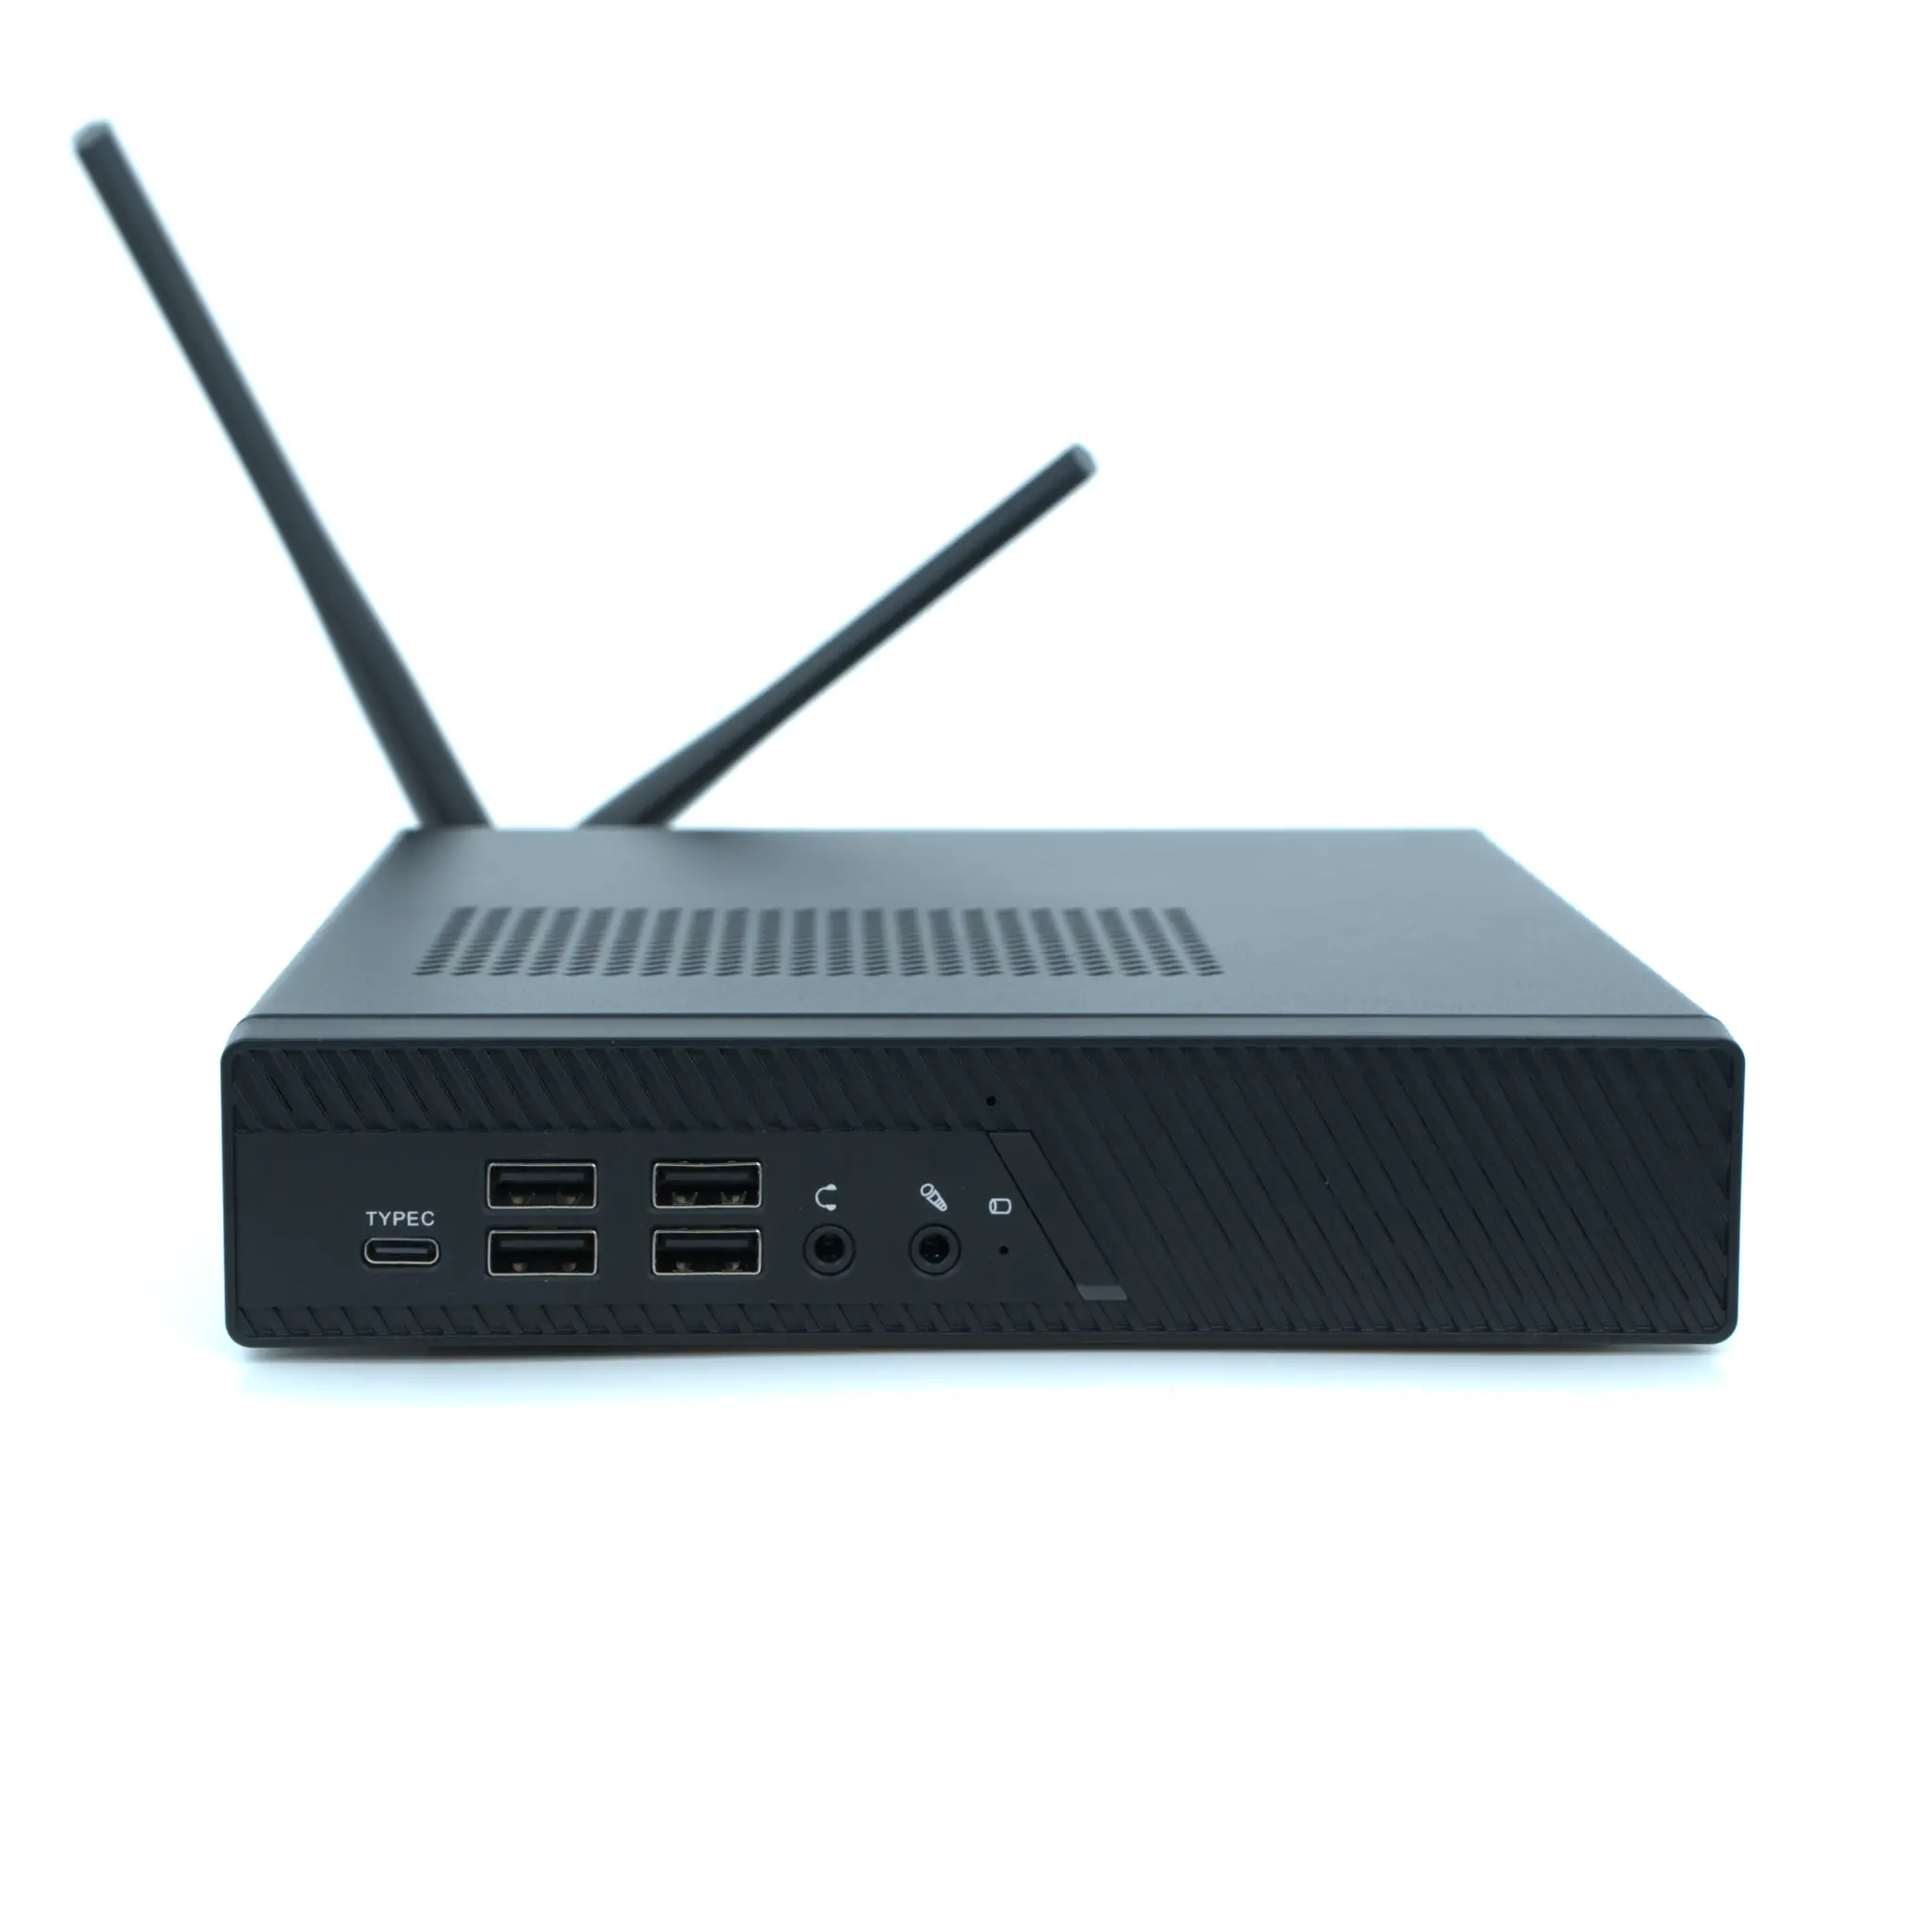
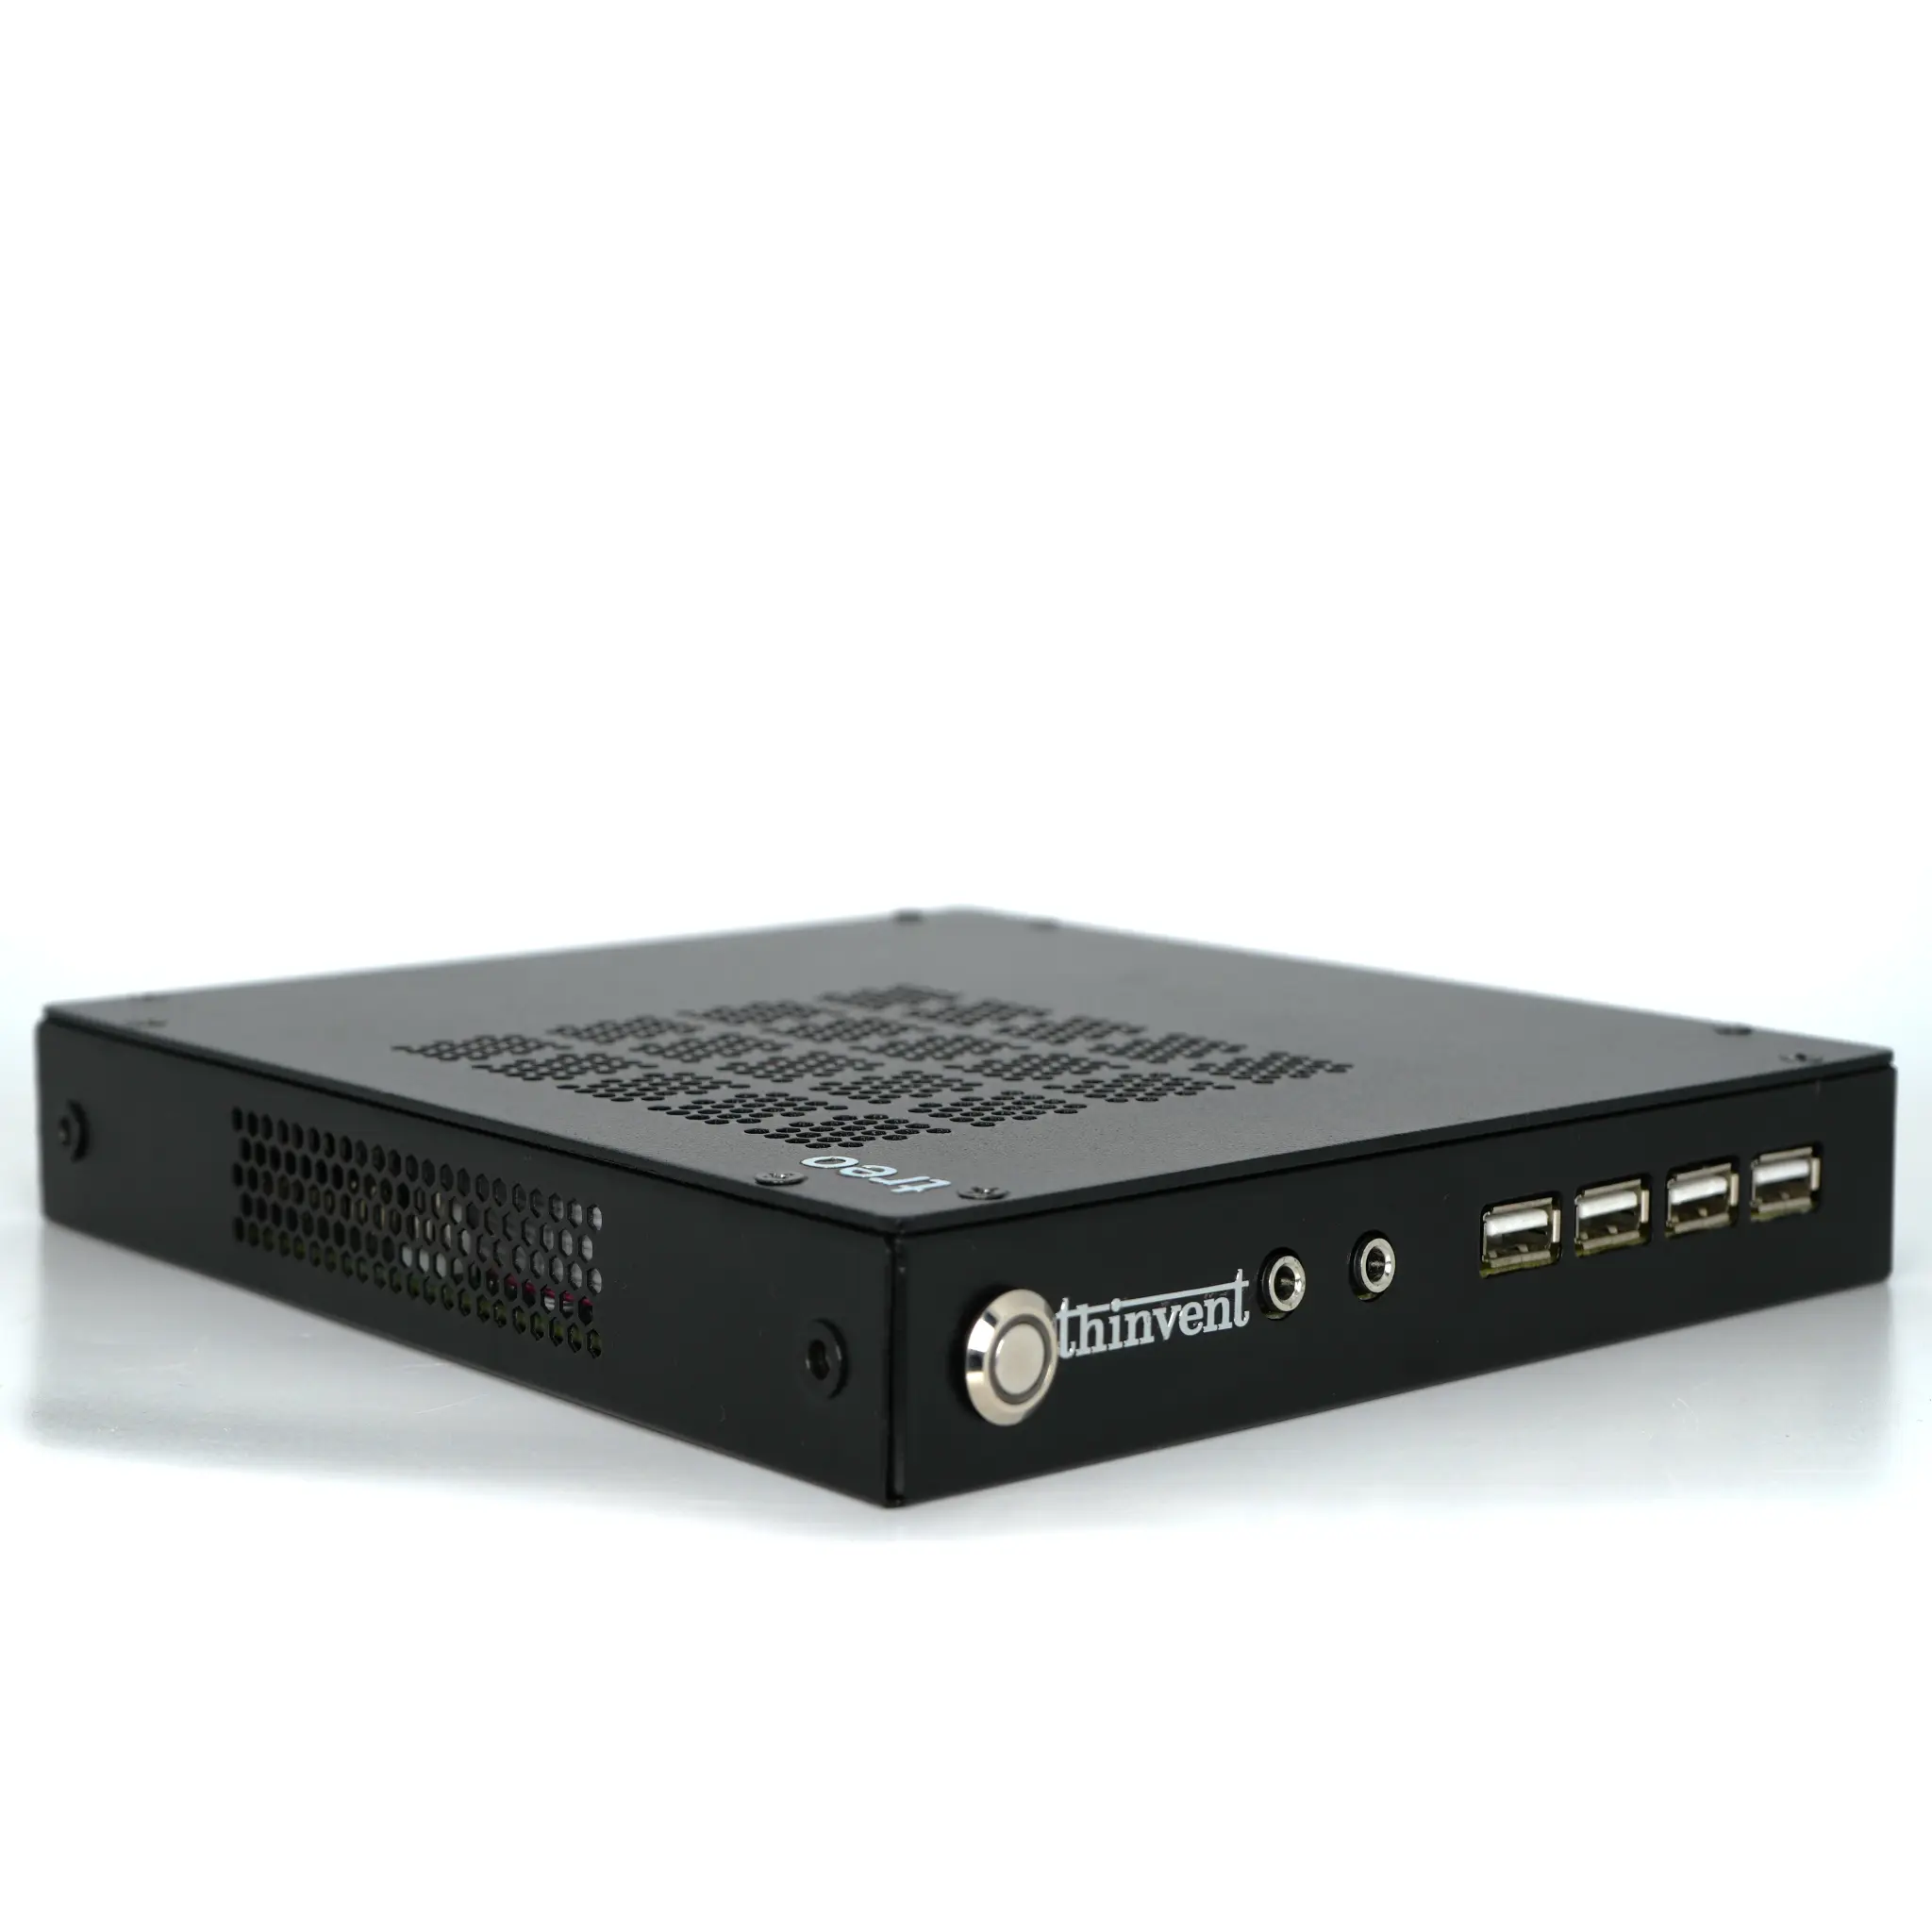
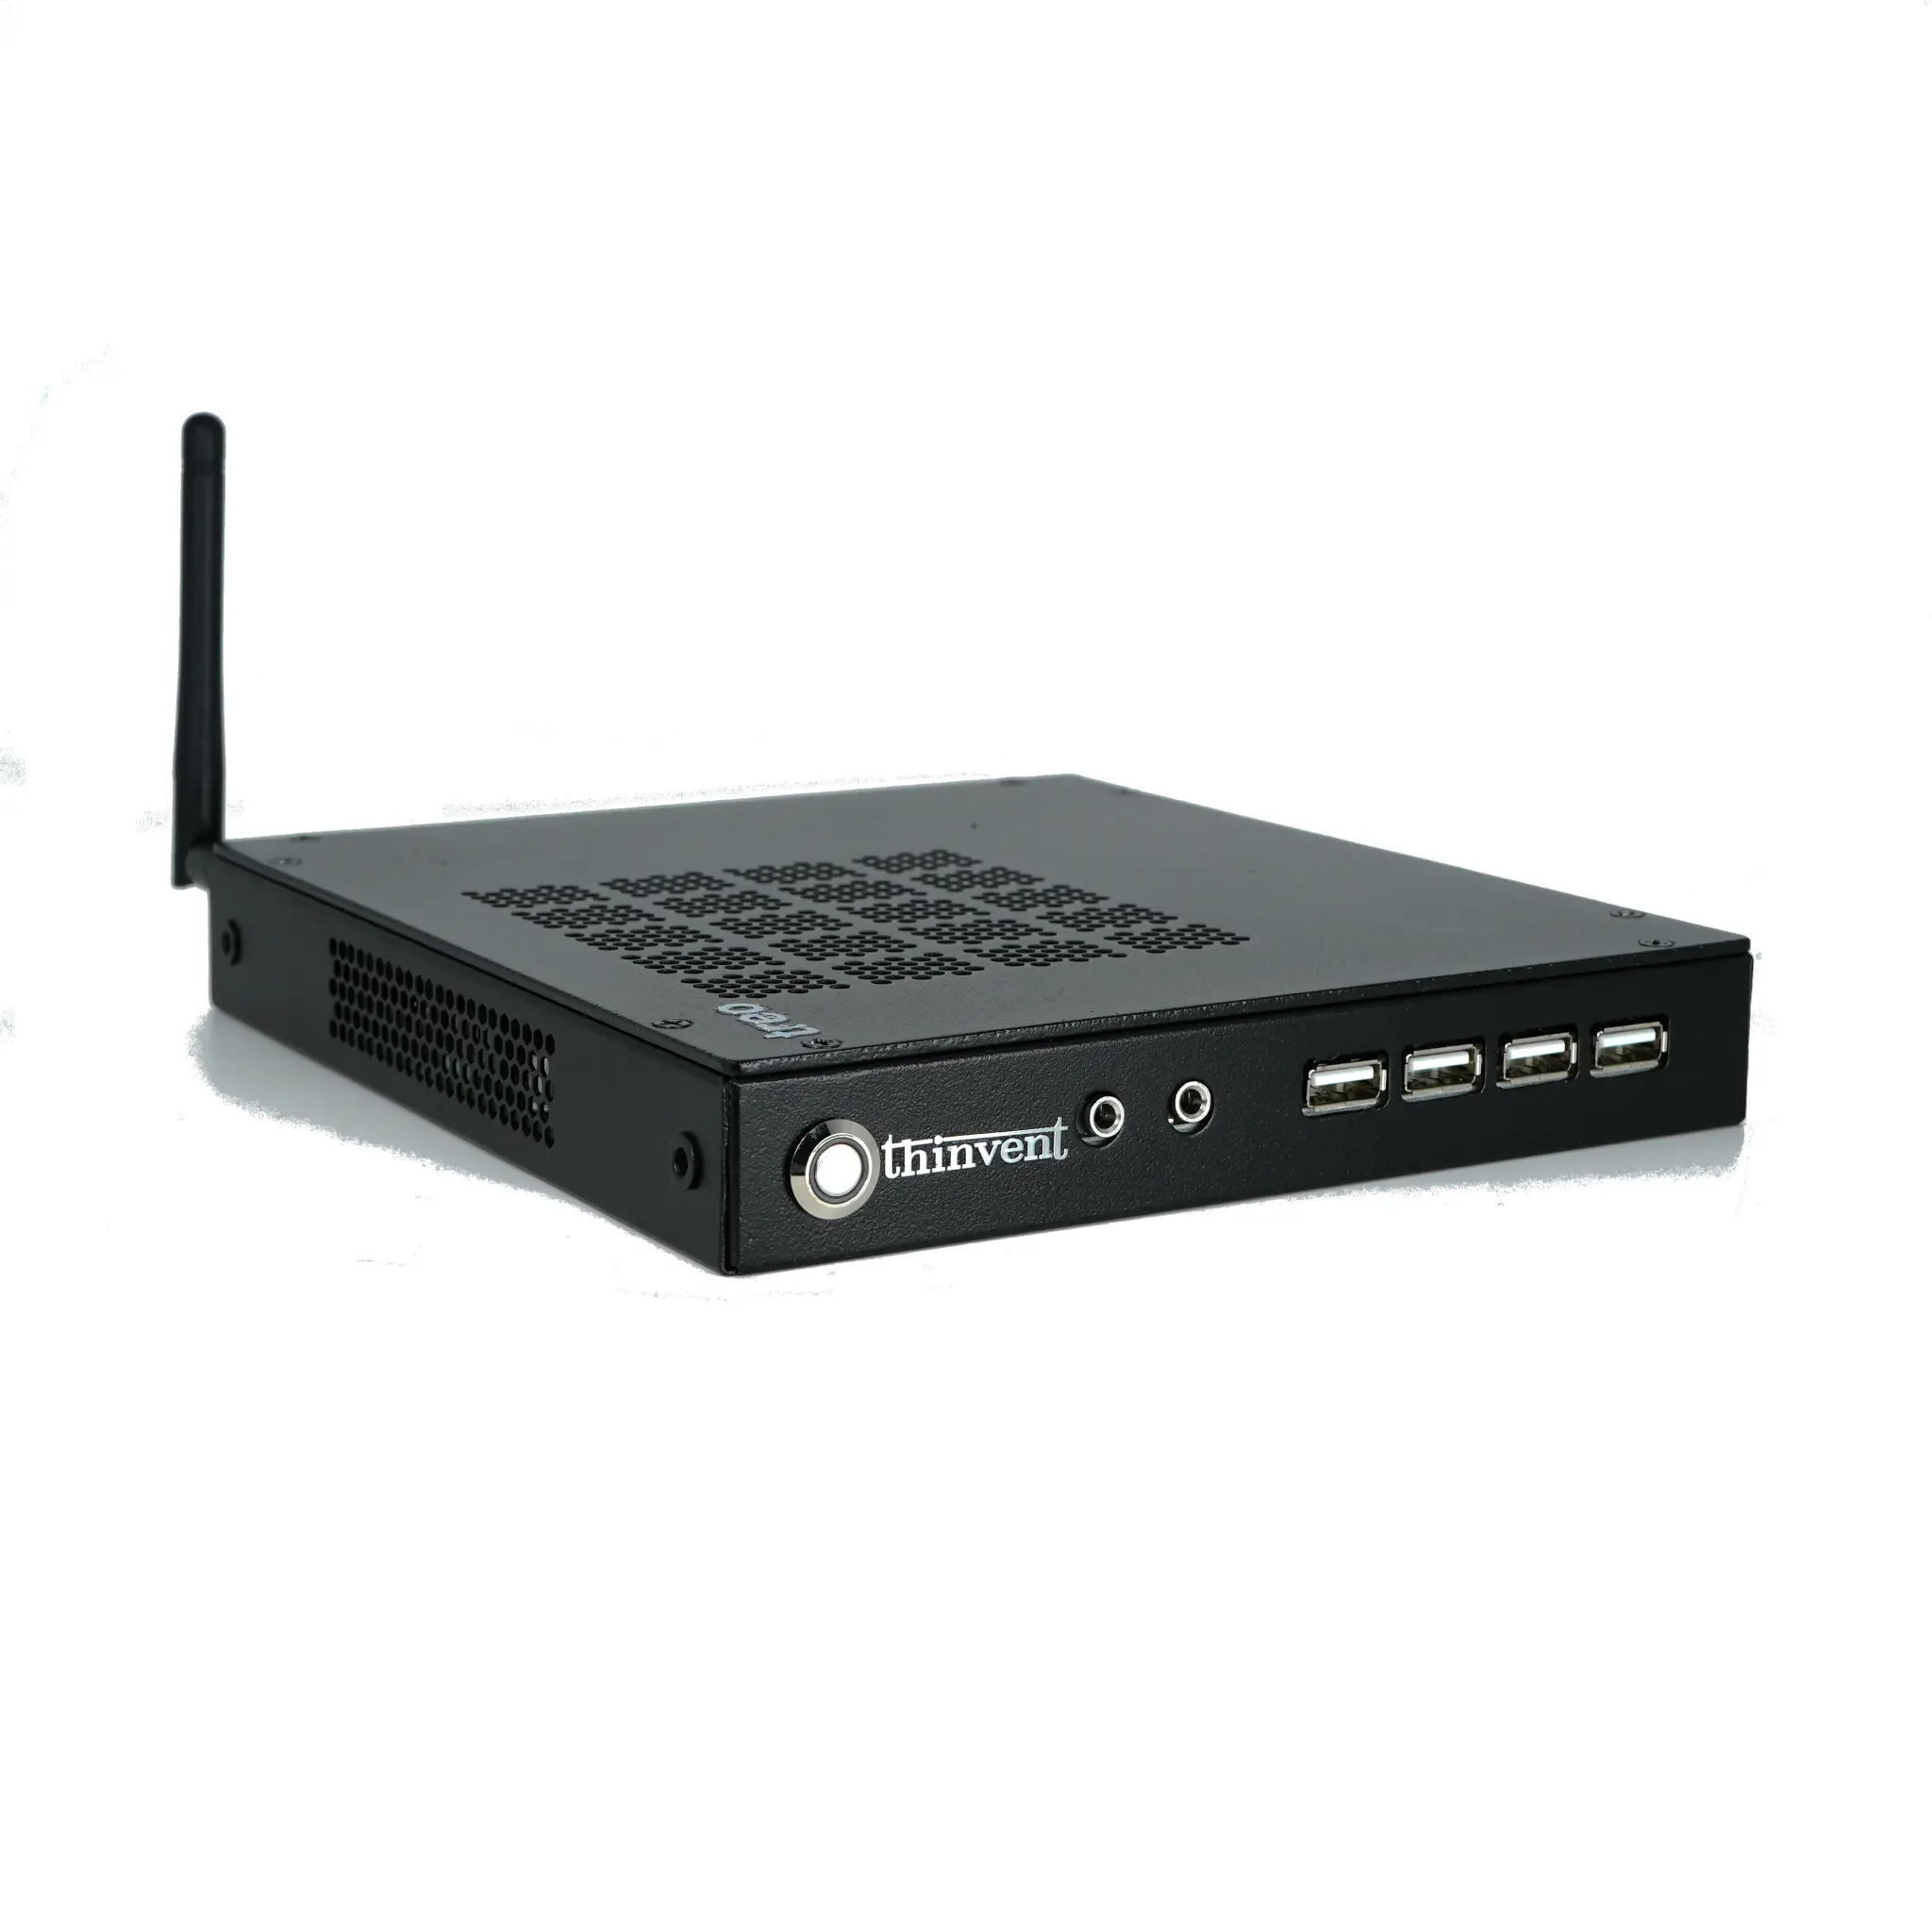
Thinvent integrates robust TPM security solutions across its product portfolio to meet diverse industrial and commercial needs. Our Industrial PC IPC5 with Intel Core i5 processors and our Aero Mini PC series with Intel Core processors are designed to support discrete or firmware TPM (fTPM via Intel PTT), providing a hardware root of trust for secure boot, BitLocker encryption, and device integrity in demanding environments. For embedded and lower-power applications, our Treo Mini PC and Industrial PC IPC1 series, powered by Intel N100 processors, also leverage firmware TPM capabilities to deliver essential hardware-based security for IoT gateways and digital signage. Thinvent's commitment to security ensures each device, from compact thin clients to powerful industrial computers, offers a foundation for building trusted and resilient computing solutions.