What is a Trusted Platform Module (TPM)?
Trusted Platform Module (TPM) is a dedicated microcontroller designed to secure hardware through integrated cryptographic keys. It provides a hardware-based root of trust, enabling secure generation and storage of encryption keys, platform integrity verification, and protection against unauthorized firmware and software modifications. TPM is a critical component for implementing robust security in computing environments, ensuring that a system boots with legitimate software and that sensitive data remains encrypted and inaccessible to attackers.
Key Specifications and Security Functions
A TPM chip offers several core security functions. It securely generates, stores, and limits the use of cryptographic keys. It can perform remote attestation, which creates a nearly unforgeable hash-key summary of the hardware and software configuration, allowing a third party to verify its trustworthiness. It also supports binding data to a specific platform configuration, meaning the data can only be decrypted on that same system. Modern TPM 2.0 modules offer enhanced algorithms and flexibility compared to the older TPM 1.2 standard, making them essential for compliance with security standards like Windows 11's hardware requirements.
Use Cases and Applications
TPM security is vital across numerous industries. In digital signage and kiosks, it prevents tampering with content and protects payment data. For industrial automation and control systems, it ensures the integrity of operational software and protects intellectual property. In healthcare, it secures patient data and ensures medical devices operate with trusted software. Financial institutions and government agencies rely on TPM for full-disk encryption, secure boot, and to meet stringent regulatory compliance mandates, safeguarding against data breaches and cyber-attacks.
Thinvent Products with TPM Security
Thinvent integrates advanced security features, including TPM capabilities, across its range of industrial and commercial computing solutions. Our products are engineered for reliability in demanding environments.
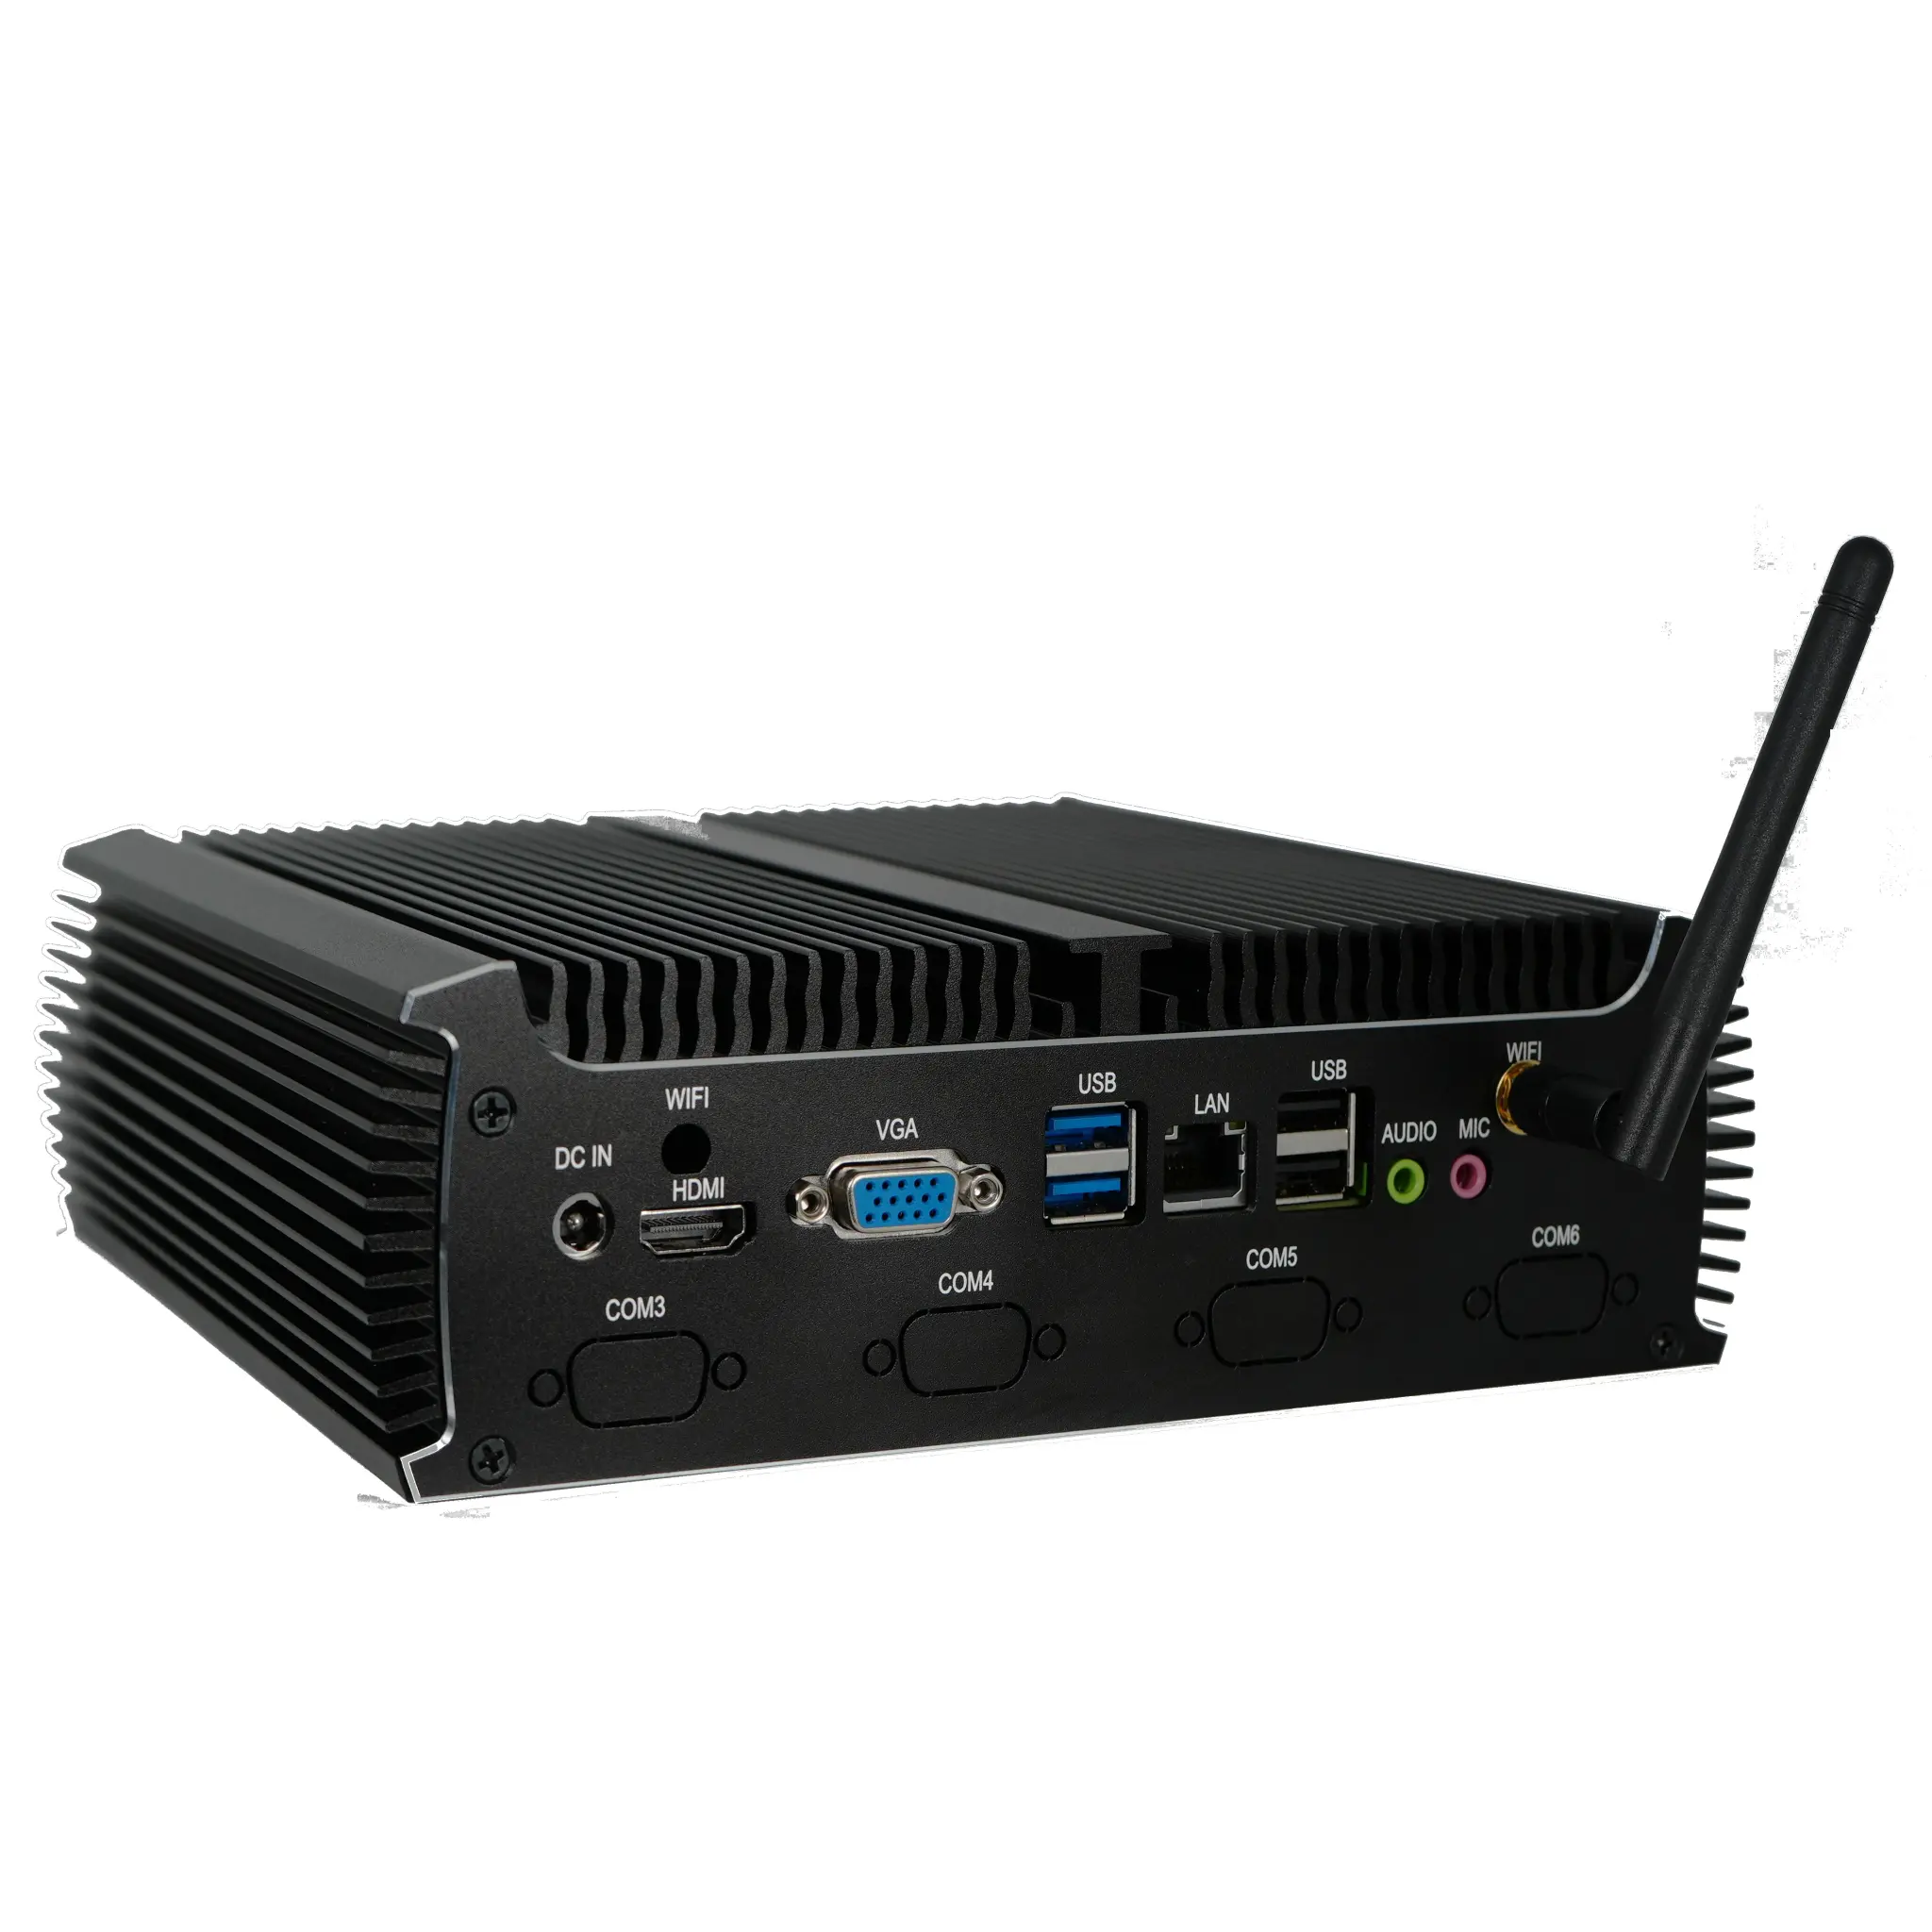
Thinvent® Industrial PC IPC5: Featuring a powerful Intel® Core™ i5-1250P processor, this system is built for high-performance computing tasks where data security is paramount. Its robust architecture is ideal for secure industrial automation, data analysis, and control systems.
Thinvent® Aero Mini PC: Available with Intel® Core™ i5-120U or i3-1215U processors, the Aero series combines performance with a compact form factor. These systems are perfect for secure office workstations, digital signage, and point-of-sale terminals requiring trusted boot and data encryption.
Thinvent® Treo & IPC1 Mini PCs: Powered by the efficient Intel® processor N100, these fanless mini PCs offer a balance of performance and energy efficiency. They are excellent for embedded applications, thin client setups, and edge computing nodes where hardware-based security enhances overall system integrity.
Our ARM-based Micro 5 Wifi and Micro 6 Pro thin clients run on the secure Thinux™ Embedded Linux platform, providing a locked-down, reliable endpoint solution for virtual desktop infrastructures (VDI), further complemented by system-level security principles.