What Is a Zero Client, and Why Does It Matter for VDI?
A zero client is the most locked-down endpoint in the desktop virtualization family. Unlike a thin client, which runs a general-purpose operating system and can execute local applications, a zero client contains no local operating system, no local storage of user data, and no local application environment. Its firmware does one job: establish a secure session to a remote desktop or virtual desktop infrastructure (VDI) host and render the pixels that come back. Because there is nothing on the endpoint to infect, patch, or steal, zero clients are widely chosen for environments where endpoint security, regulatory compliance, and low administrative overhead matter more than local flexibility.
For VDI specifically, zero clients typically connect over protocols such as PCoIP, HDX, Blast Extreme, or RDP, and they are usually managed centrally through a connection broker or device management console. That architecture means a single administrator can configure hundreds of endpoints, enforce policy, and push firmware updates without touching a single desk.
Security Characteristics of a Well-Designed Zero Client
The security advantage of a zero client comes from what it does not have. There is no writable user storage, so data cannot be copied off the device. There is no browser, no email client, and no local OS shell, so malware has no standard execution surface. Many zero clients also support signed firmware, secure boot, and encrypted session transport (TLS or protocol-native encryption), and can be configured to talk only to approved brokers or hosts.
Physical security matters too. USB port control — allowing keyboards and mice while blocking mass storage, or disabling USB entirely — is a common requirement in healthcare, finance, and government deployments. Combined with centralized authentication (Active Directory, LDAP, or smart-card / CAC), this creates an endpoint that is both hard to attack and easy to audit.
Zero Client vs. Thin Client: Choosing the Right Endpoint
| Aspect | Zero Client | Thin Client |
|---|---|---|
| Local OS | None (firmware only) | Windows IoT, Linux, or similar |
| Local storage of user data | None | Limited, sometimes writable |
| Local applications | Not supported | Limited support possible |
| Attack surface | Very small | Small but larger than zero client |
| Protocol flexibility | Often fixed at purchase | Usually multiple protocols |
| Management | Fully centralized | Centralized with more options |
| Best fit | High-security VDI, task workers, kiosks | Mixed workloads, local peripherals, offline use |
The practical rule: if every user works entirely inside a hosted desktop and you want the smallest possible attack surface, a zero client is the cleaner choice. If users need a local browser, local printing stacks, or occasional offline capability, a thin client or a compact mini PC running a locked-down OS is more appropriate.
Where Secure Zero Client Deployments Fit Best
Typical zero client and locked-down thin endpoint deployments include hospital wards and clinics (patient data must not leave the device), bank branches and insurance back offices, government and defence desks, call centres and BPO floors, CAD and design workgroups that need centralized GPU-backed virtual workstations, and education labs where machines are shared by many users. In each case the pattern is the same: sensitive data stays in the data centre, the endpoint is disposable and interchangeable, and IT manages one image instead of hundreds of desks.
Thinvent's Products for Secure VDI Endpoints
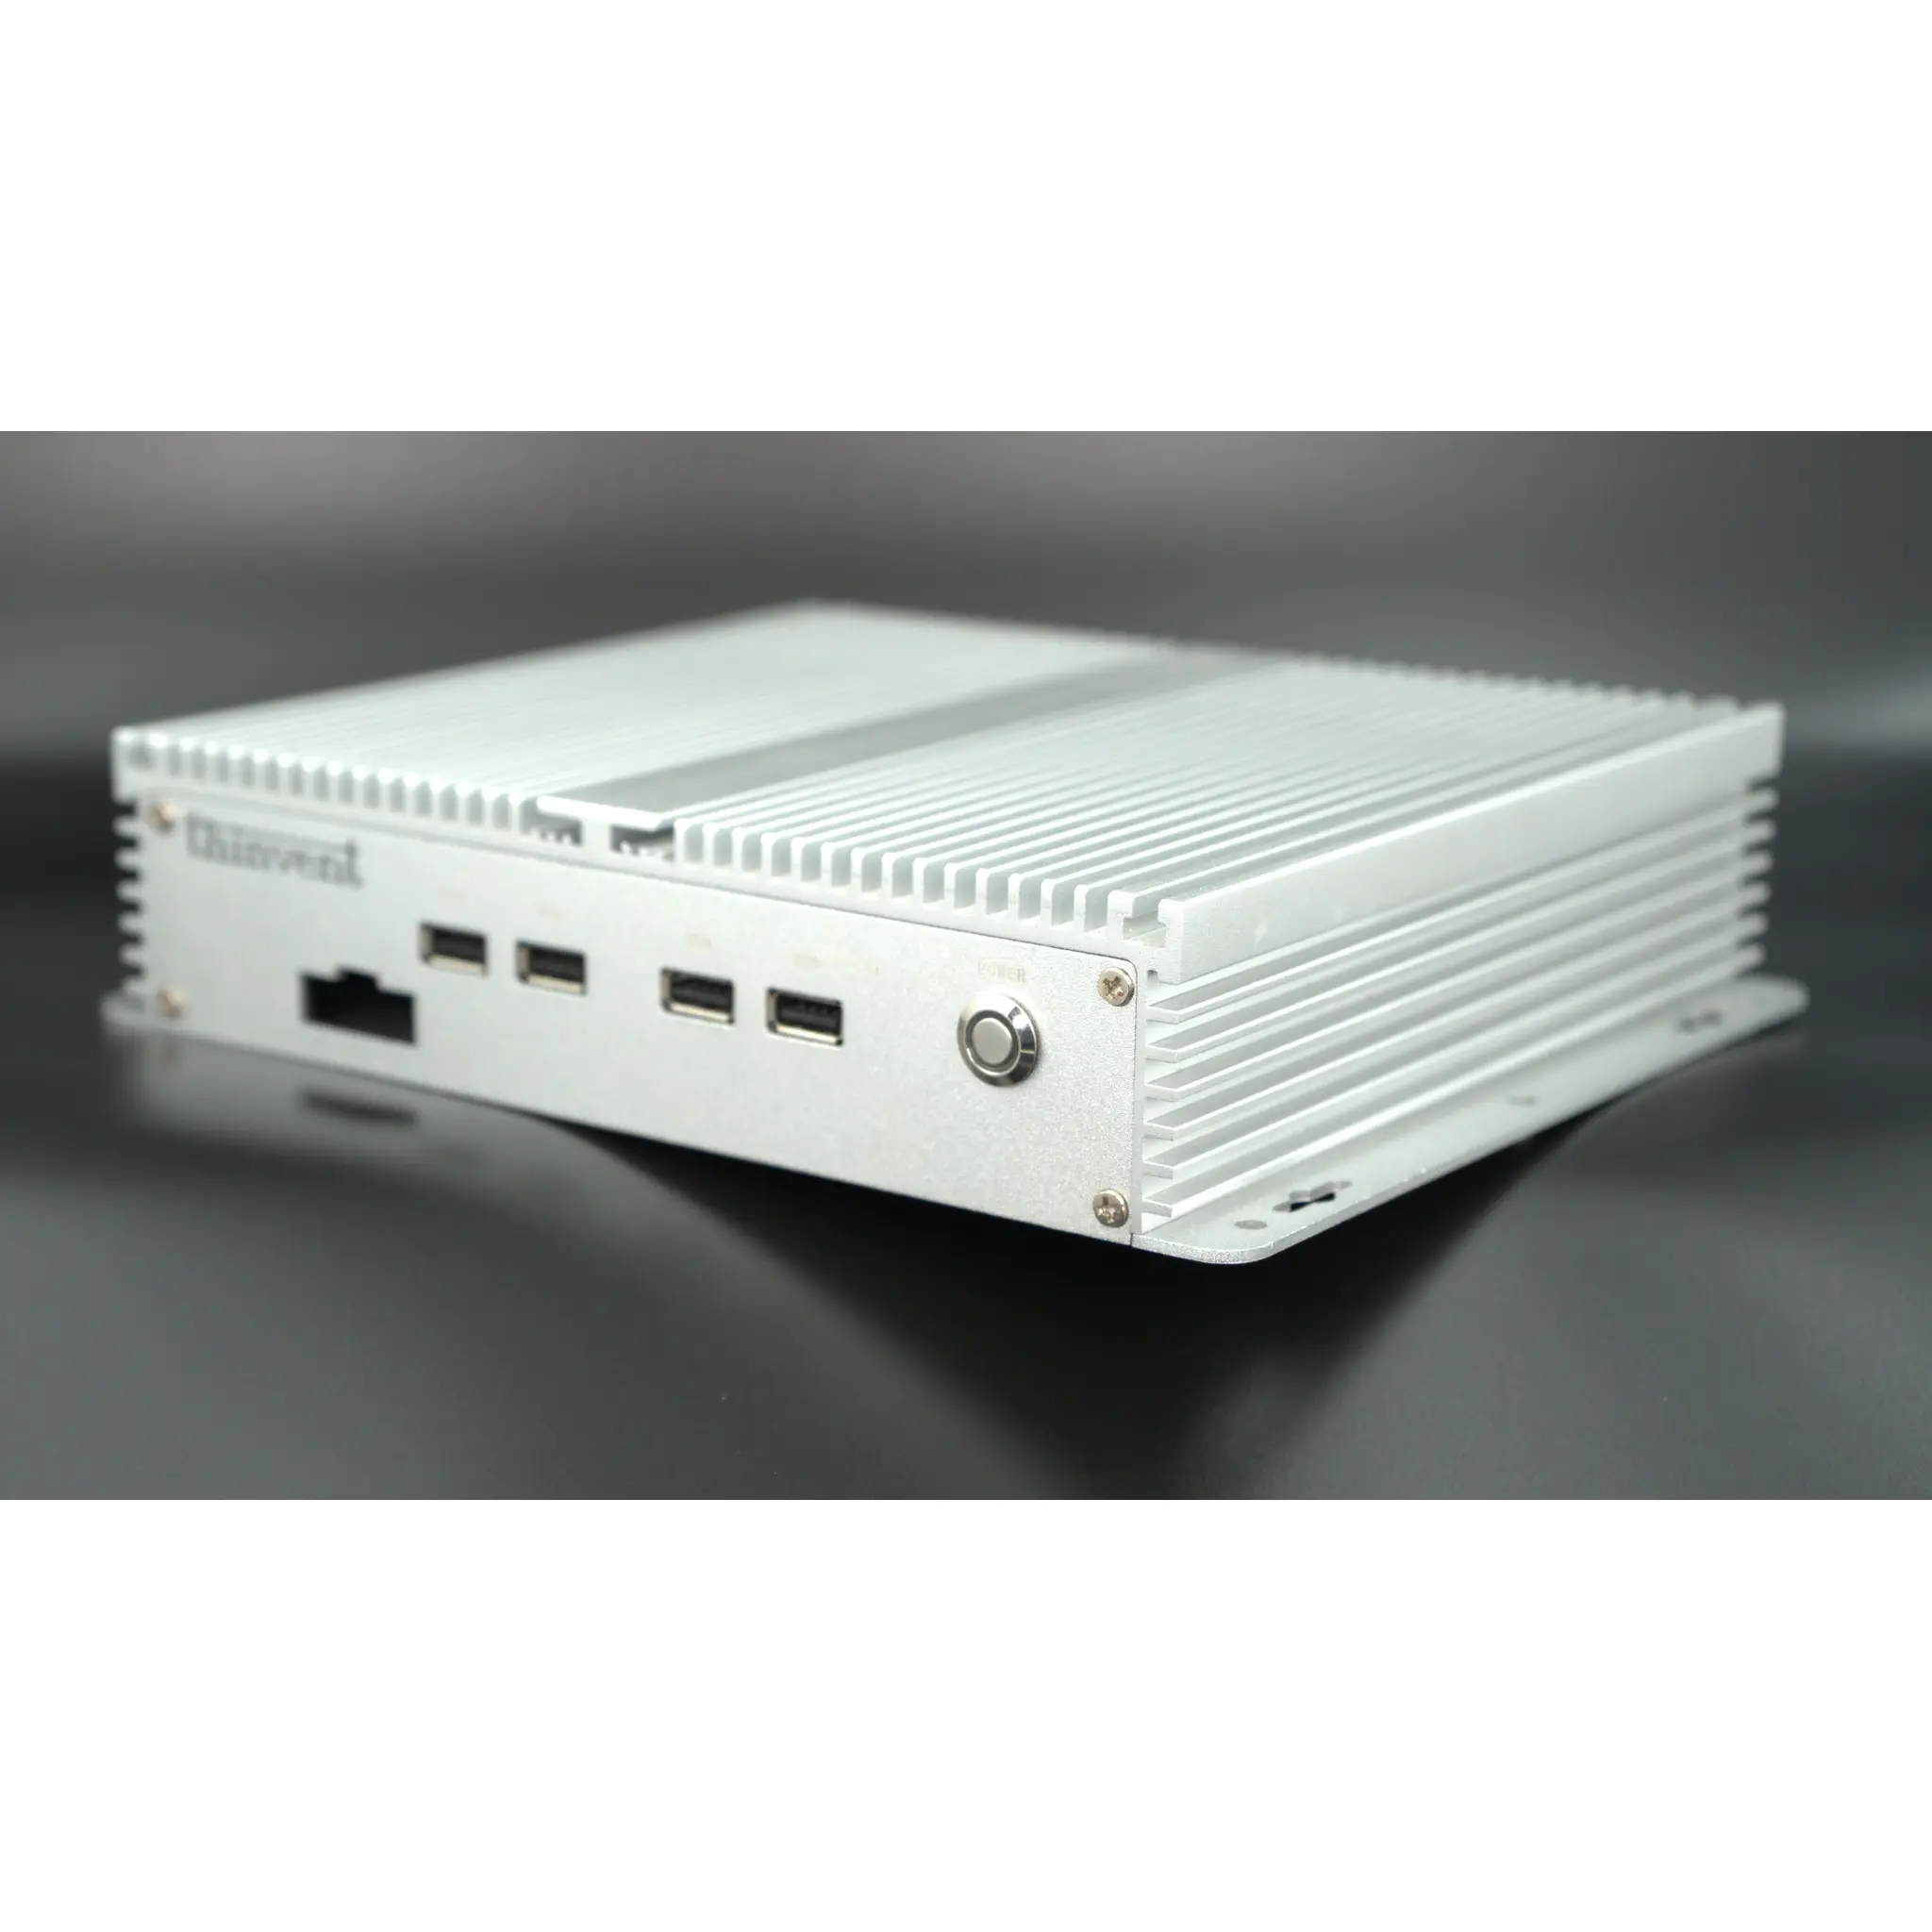
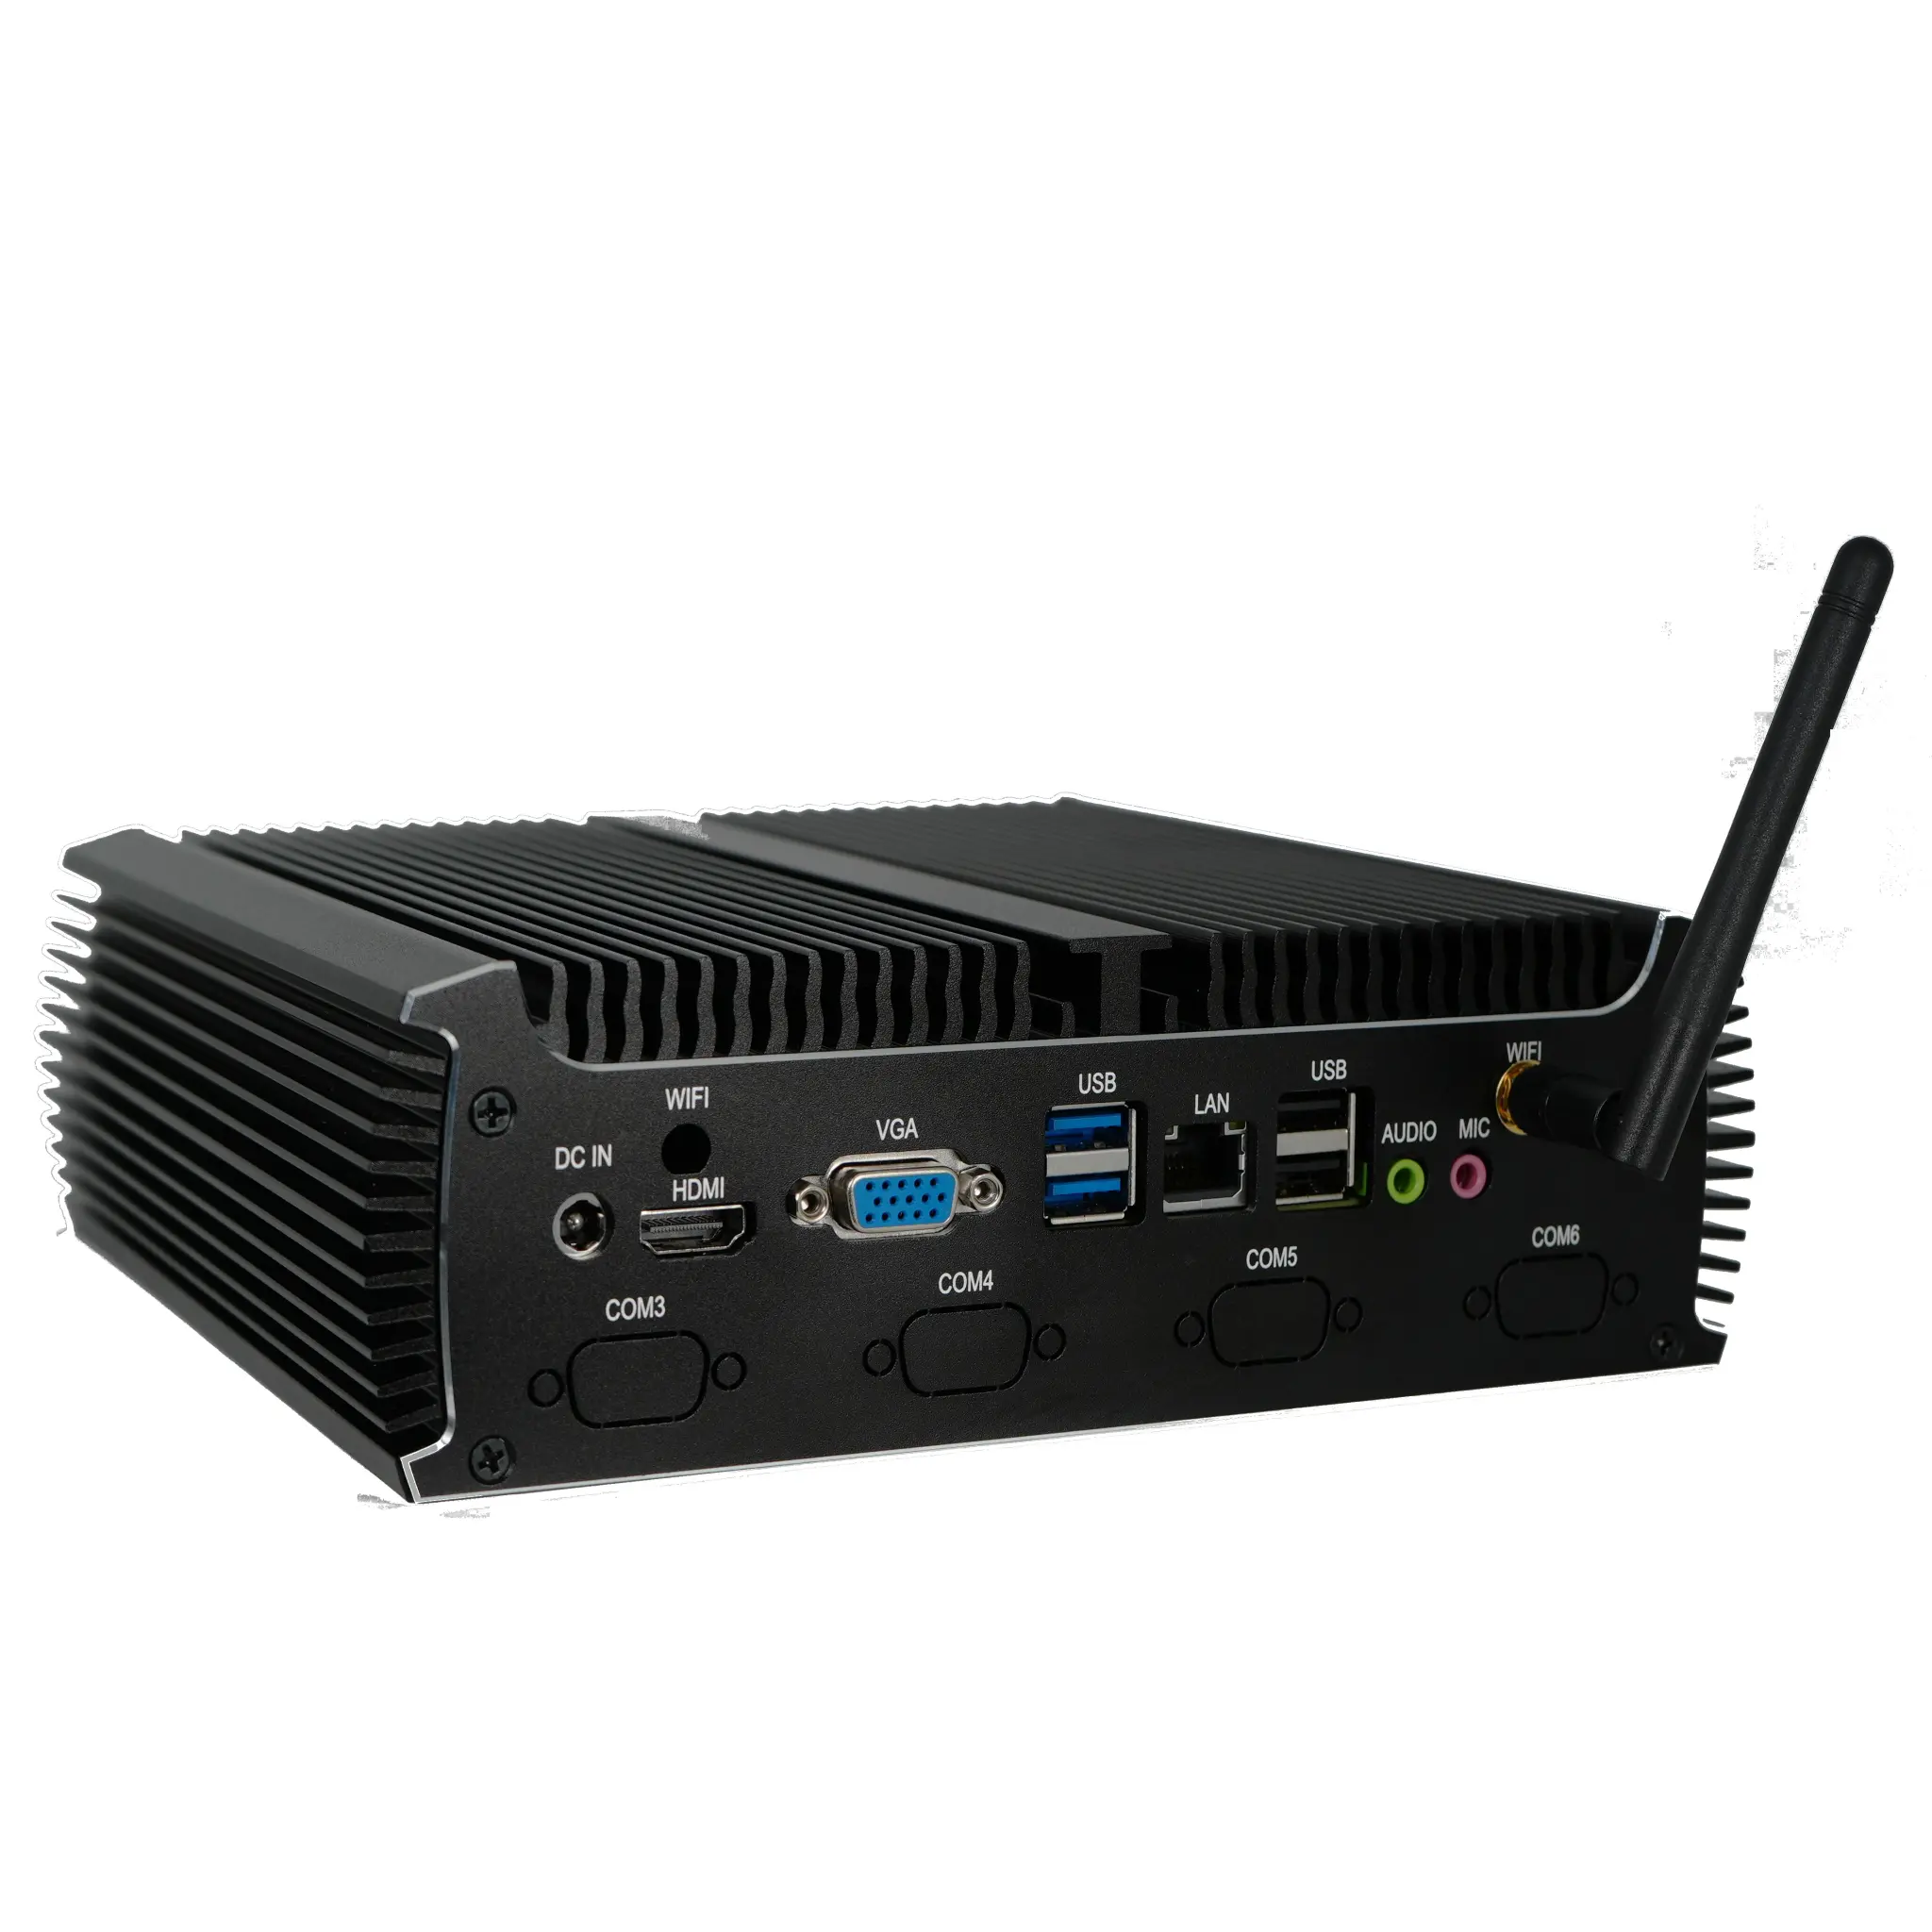
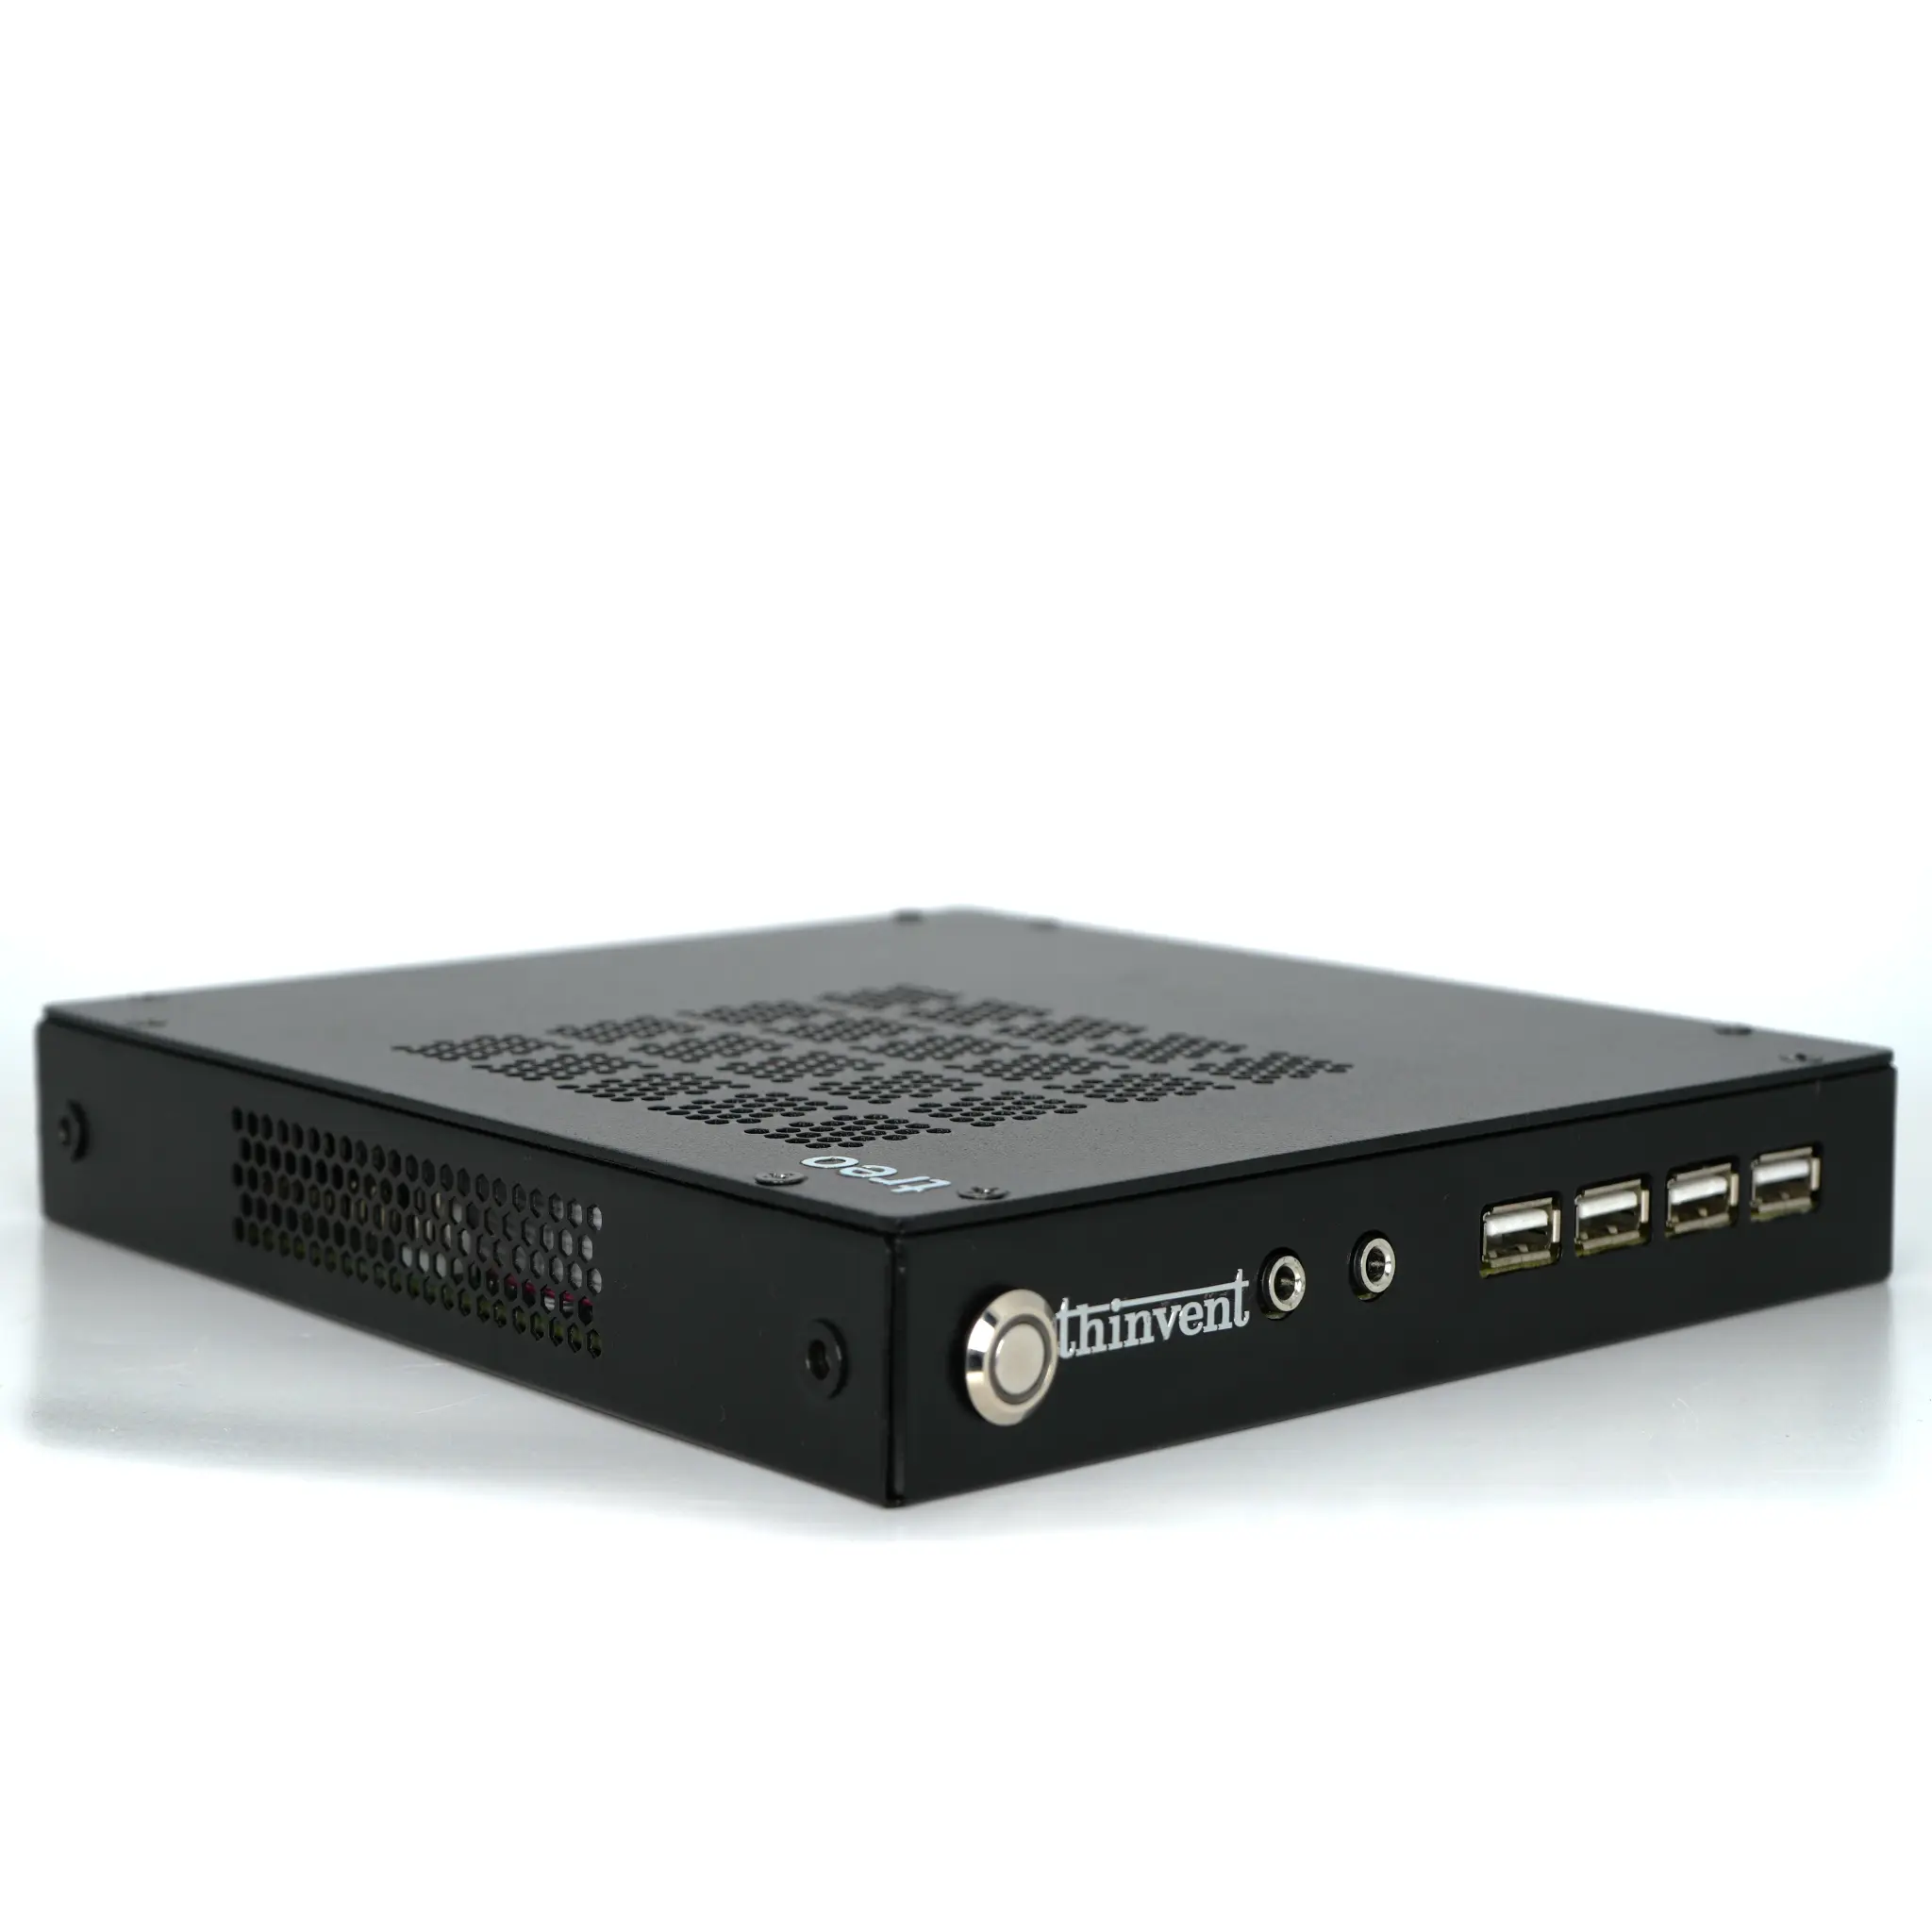
Thinvent builds thin clients, mini PCs, industrial PCs, and all-in-one PCs that are widely deployed as secure VDI endpoints. Because our devices ship with a choice of operating systems — Microsoft Windows 11 Pro, Ubuntu Linux 24.04 LTS, Thinux™ Embedded Linux, FreeDOS, or no OS at all — integrators can lock the endpoint down to exactly the session client required, with no unnecessary services running. Configurations range from power-efficient Intel Celeron and N-series platforms for standard task-worker VDI, up to Intel Core i3 and i5 systems with 16 GB or more of memory for heavier virtual desktop and multi-session workloads. Dual Gigabit Ethernet ports, multiple HDMI outputs, USB 3.2 Gen 2 and USB-C connectivity, and fanless industrial form factors make them suitable for both office floors and dusty, high-temperature environments. For deployments where a true zero client is required, Thinvent thin clients running a minimal Linux image with only the remote display protocol enabled provide a comparable security posture with centralized management.