Understanding the Query
The input <body onload=alert("bingo")> is a classic cross-site scripting (XSS) test payload, not a product query. It attempts to inject JavaScript into a web page's onload event handler so that a script runs automatically when the page finishes loading. Security researchers, penetration testers, and developers use payloads like this to verify whether an application properly sanitizes user-supplied input before rendering it into HTML.
Why This Matters for Industrial and Edge Systems
XSS vulnerabilities are most commonly associated with web applications, but the systems that host those applications matter just as much. Industrial PCs, thin clients, kiosks, and all-in-one terminals frequently run browser-based dashboards, SCADA HMI panels, digital signage players, and point-of-sale front ends. If the underlying operating system or browser is outdated and unpatched, an injected script can steal session cookies, redirect a kiosk to a malicious page, or alter what an operator sees on screen. Hardening the endpoint — keeping the OS current, locking down the browser, and isolating user sessions — is a practical first line of defence.
Practical Mitigations
| Layer | Recommended Practice |
|---|---|
| Application | Escape and validate all user input; never build HTML by string concatenation |
| Browser | Enable Content Security Policy (CSP); disable inline script execution where possible |
| Operating System | Run a current, supported OS with regular security updates |
| Deployment | Kiosk mode, restricted user accounts, no unnecessary browser extensions |
| Network | Segment OT/IT traffic; restrict outbound access from operator terminals |
Use Cases
-
Kiosks and self-service terminals running web-based interfaces in public spaces
-
Factory HMI panels displaying browser-rendered dashboards on the shop floor
-
Digital signage players that pull content from a web CMS
-
Thin client deployments where users access web apps through a locked-down browser
-
Edge gateways that expose local configuration pages over the network
Thinvent's Products for Secure, Locked-Down Deployments
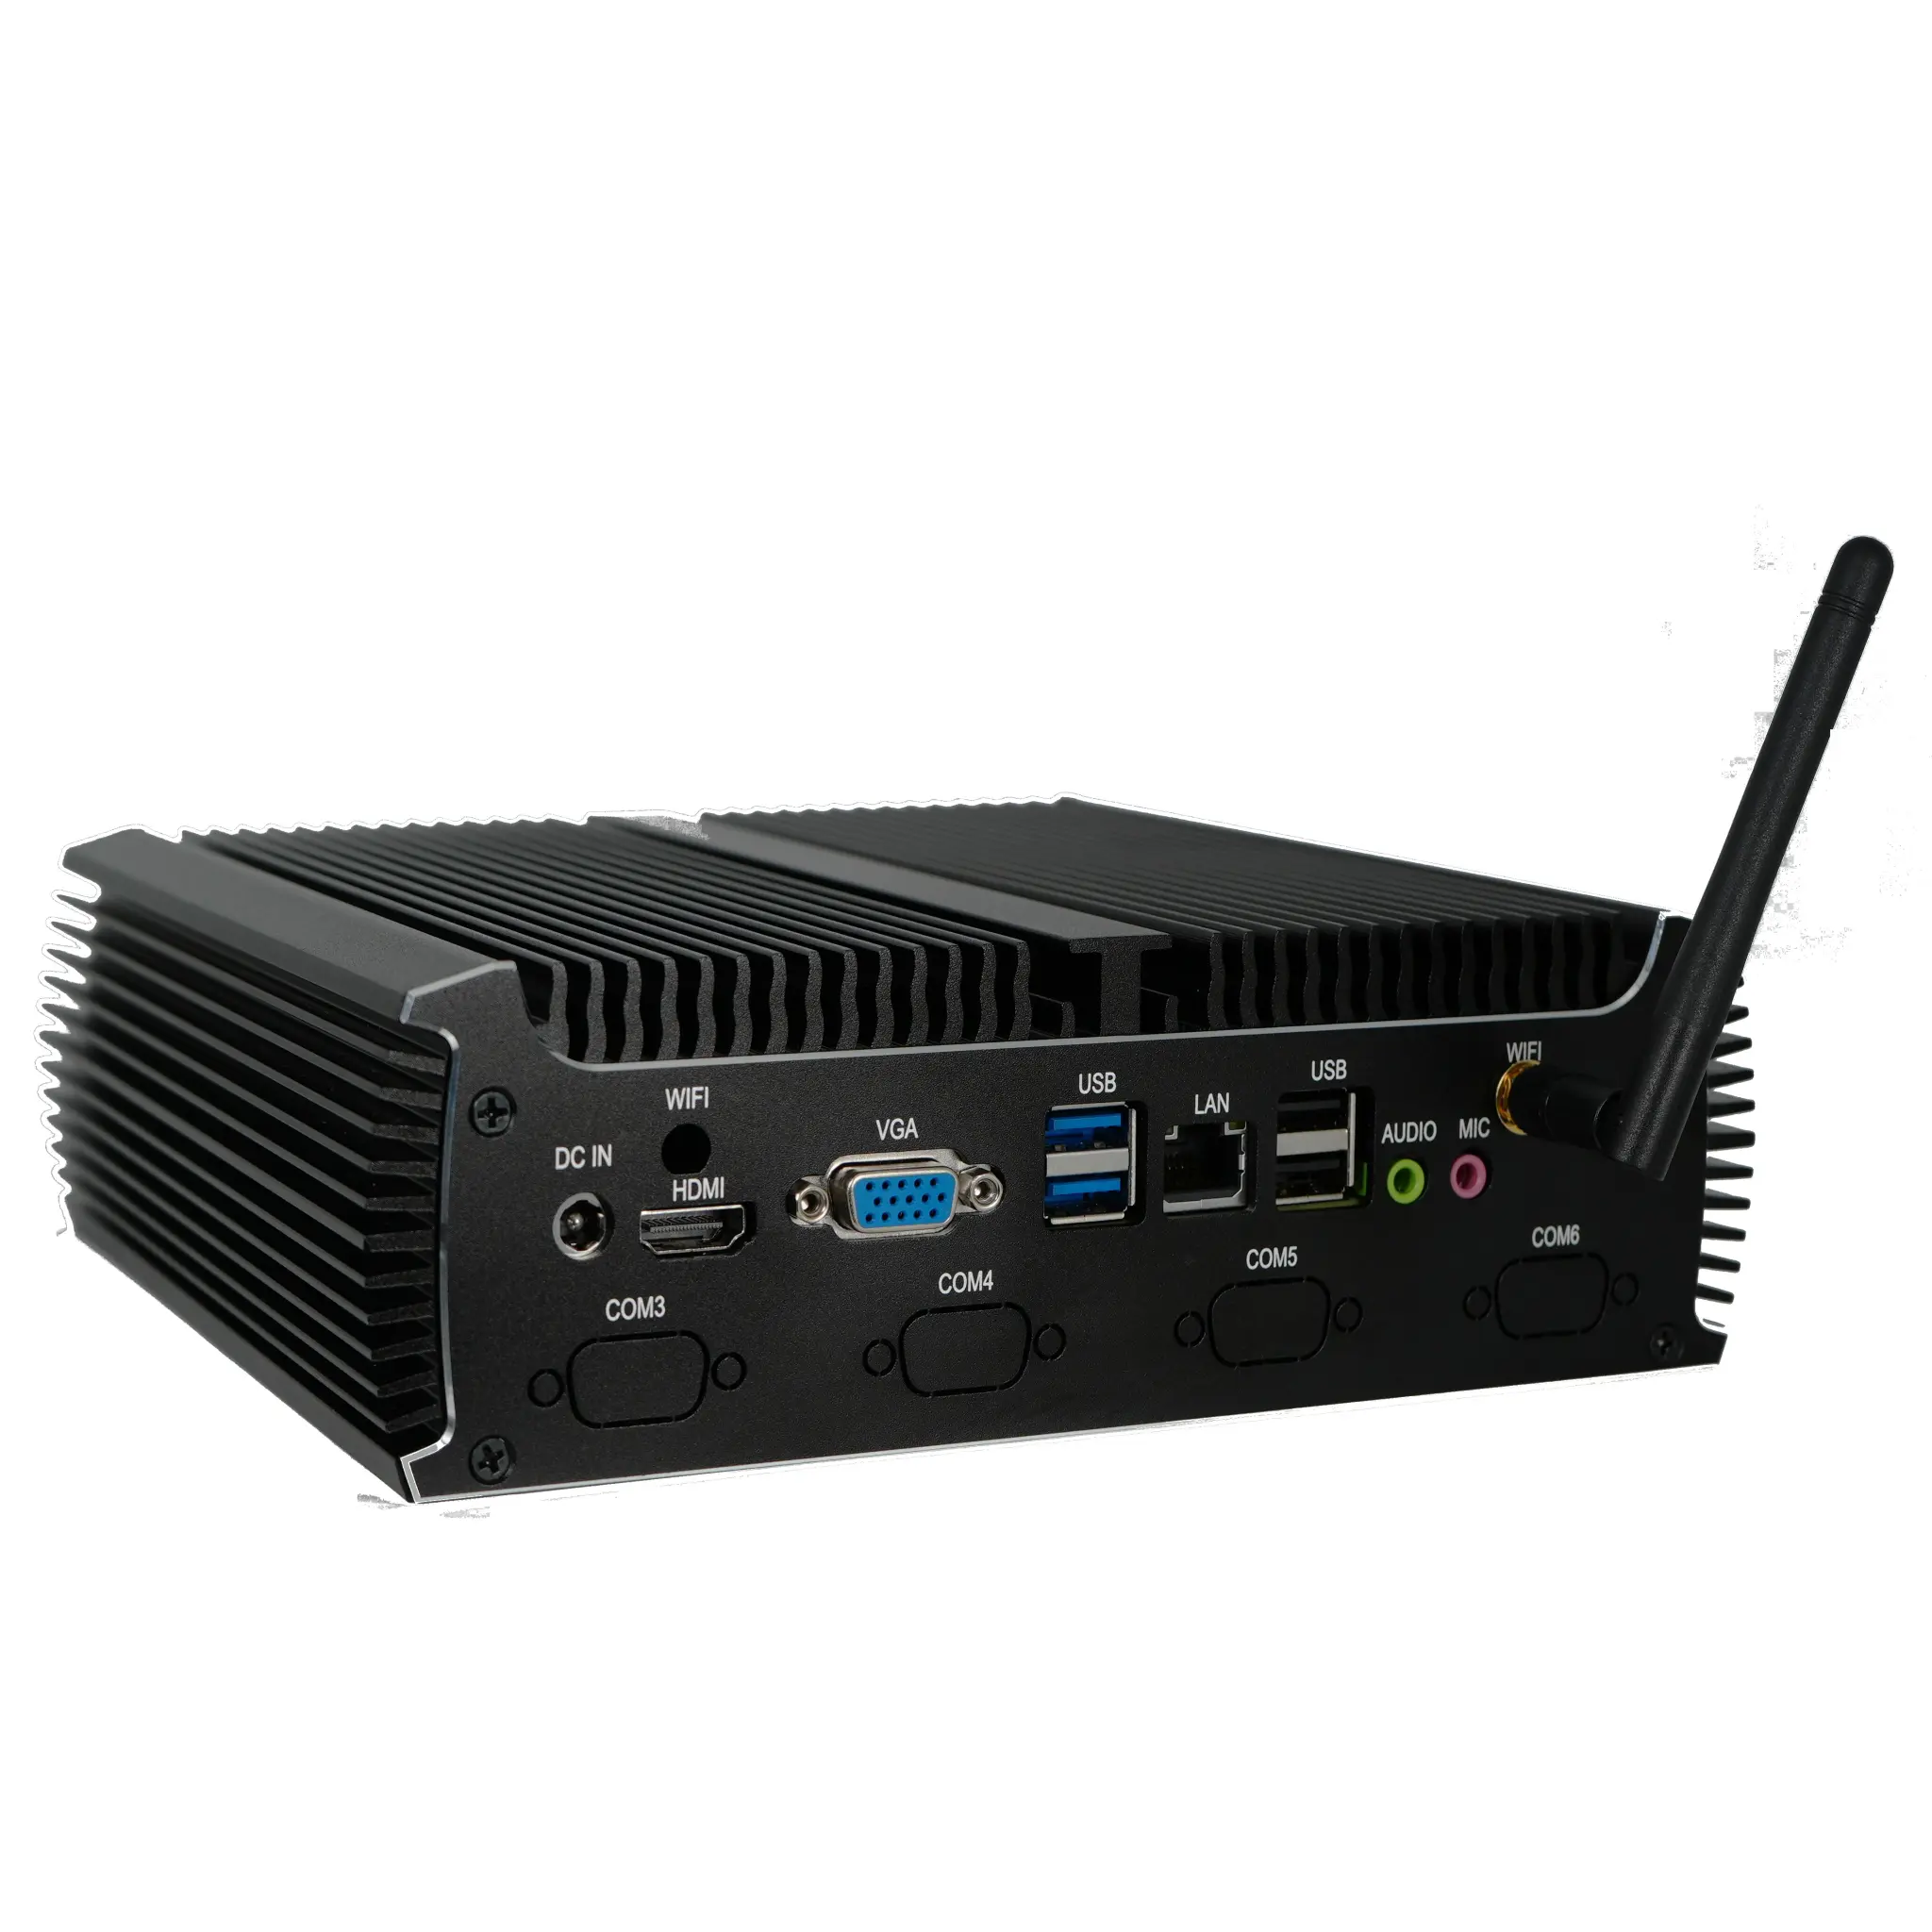
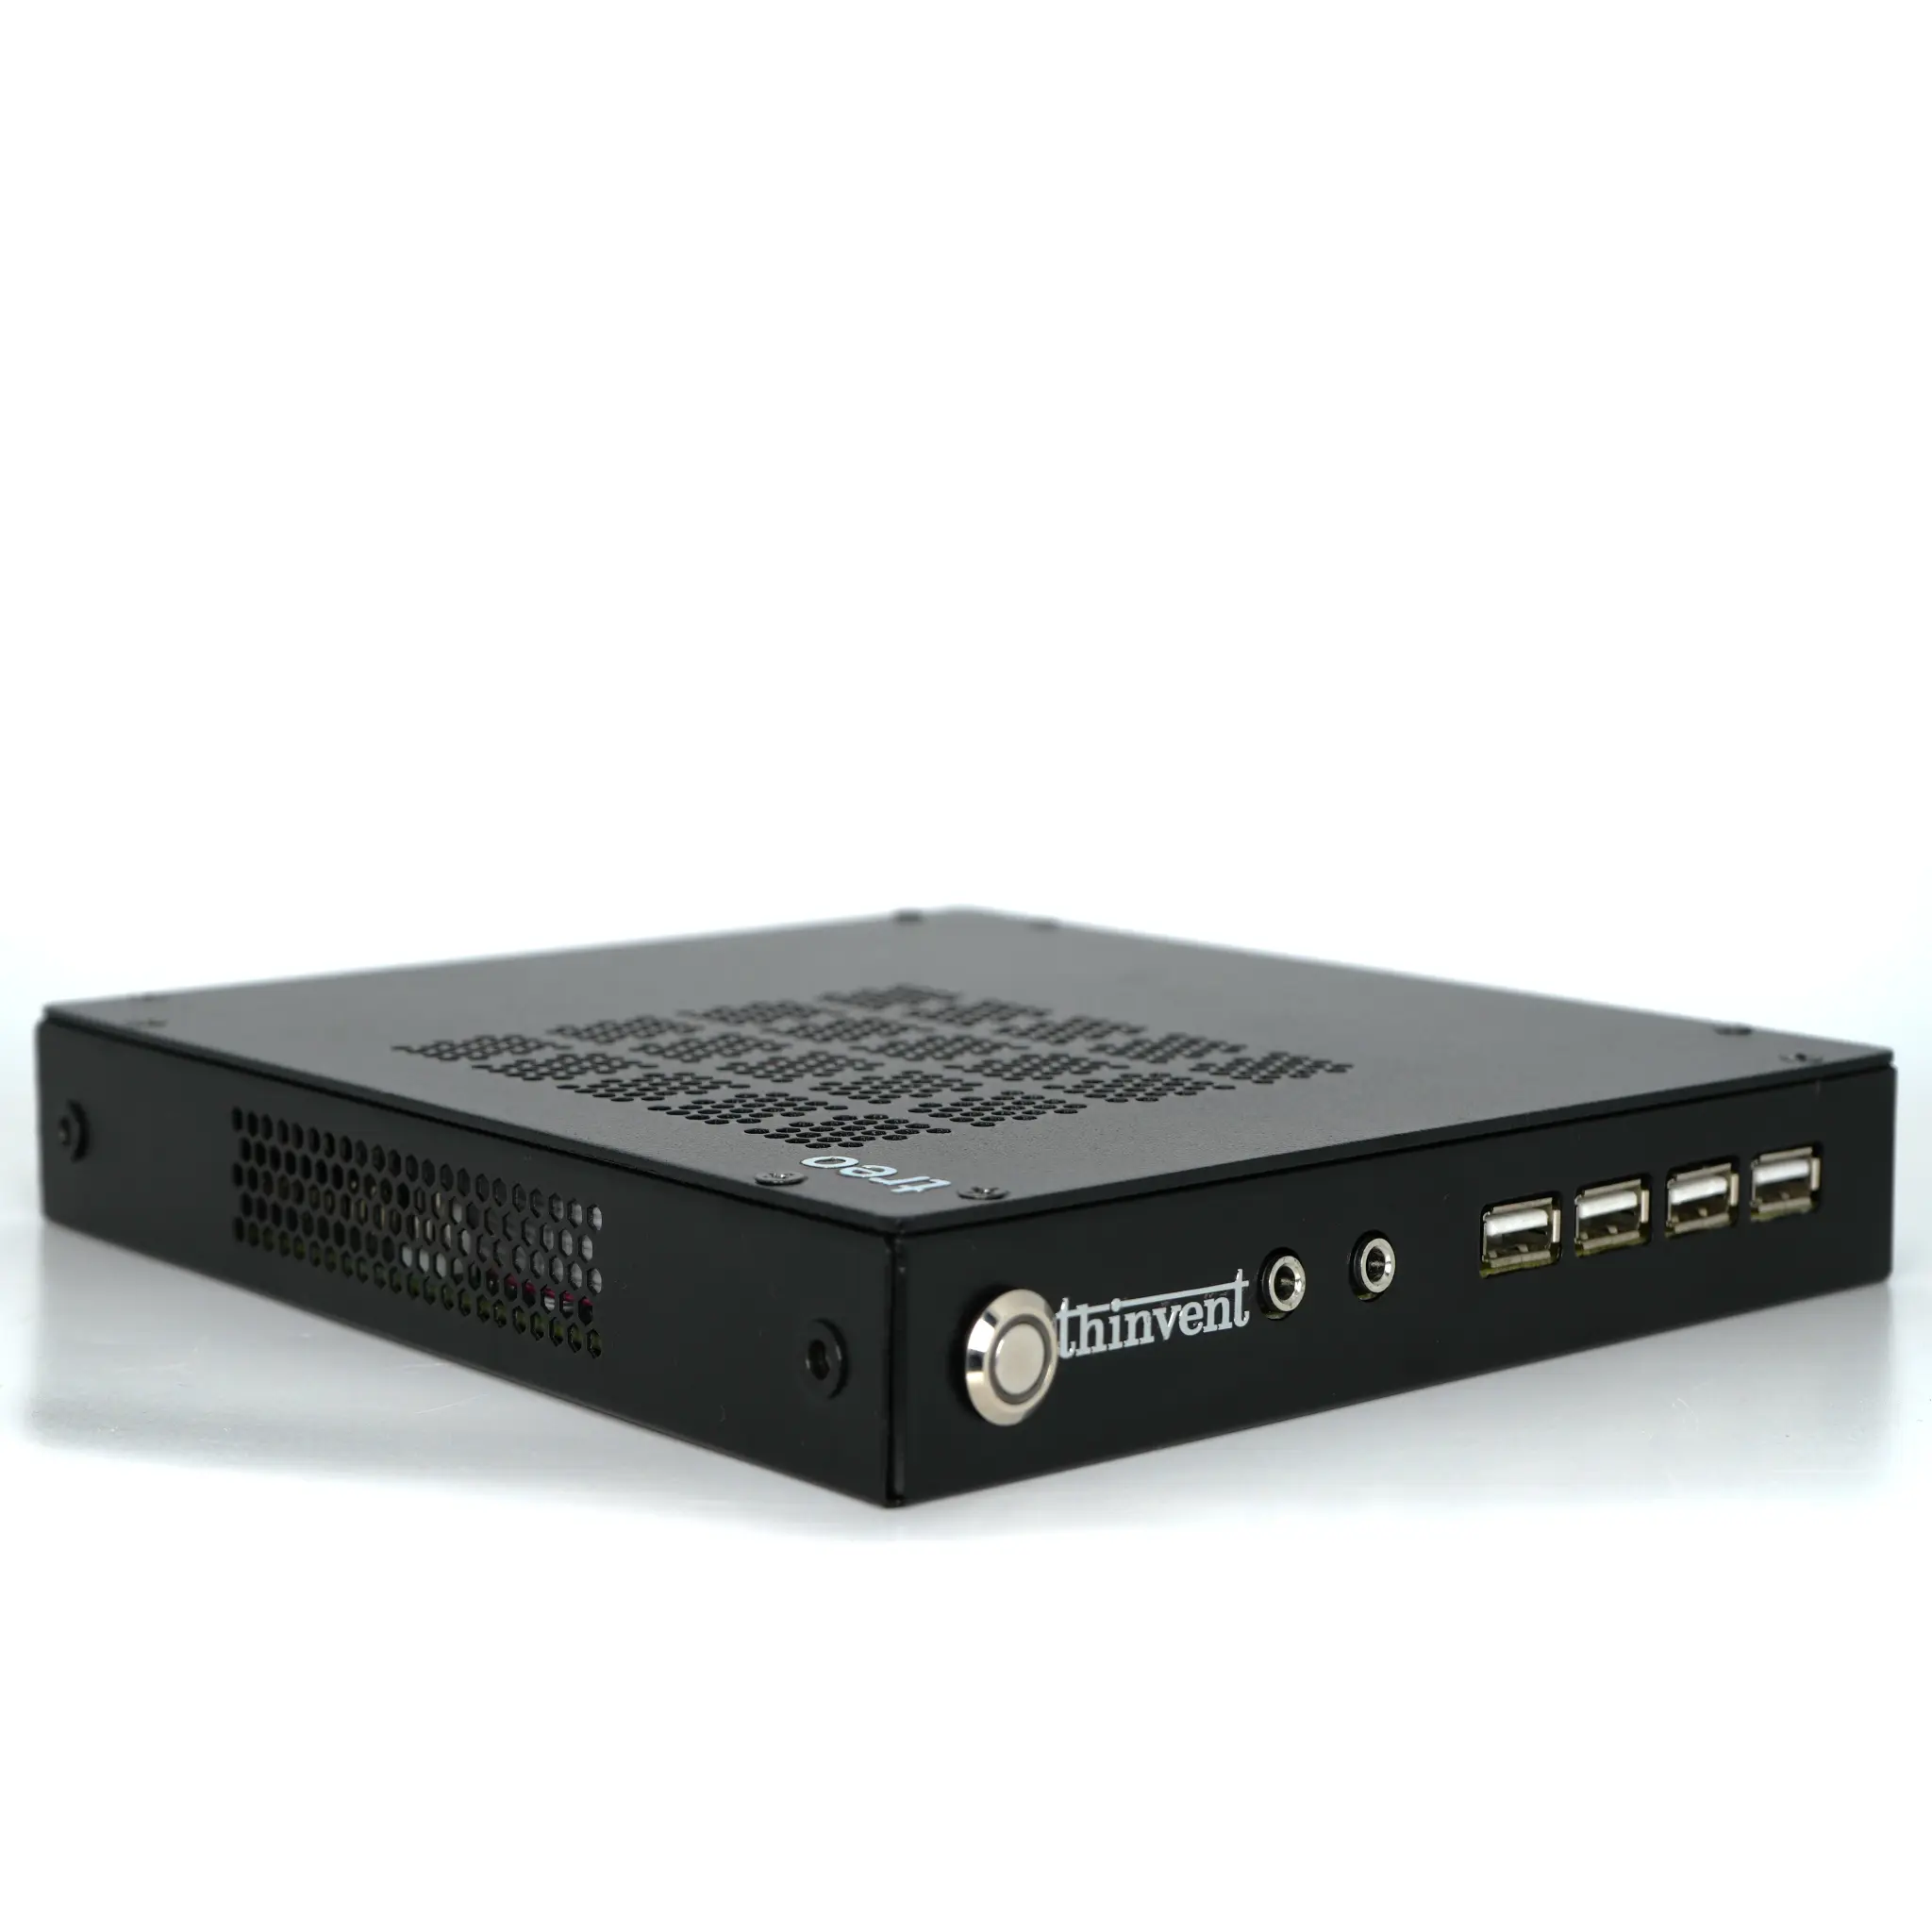
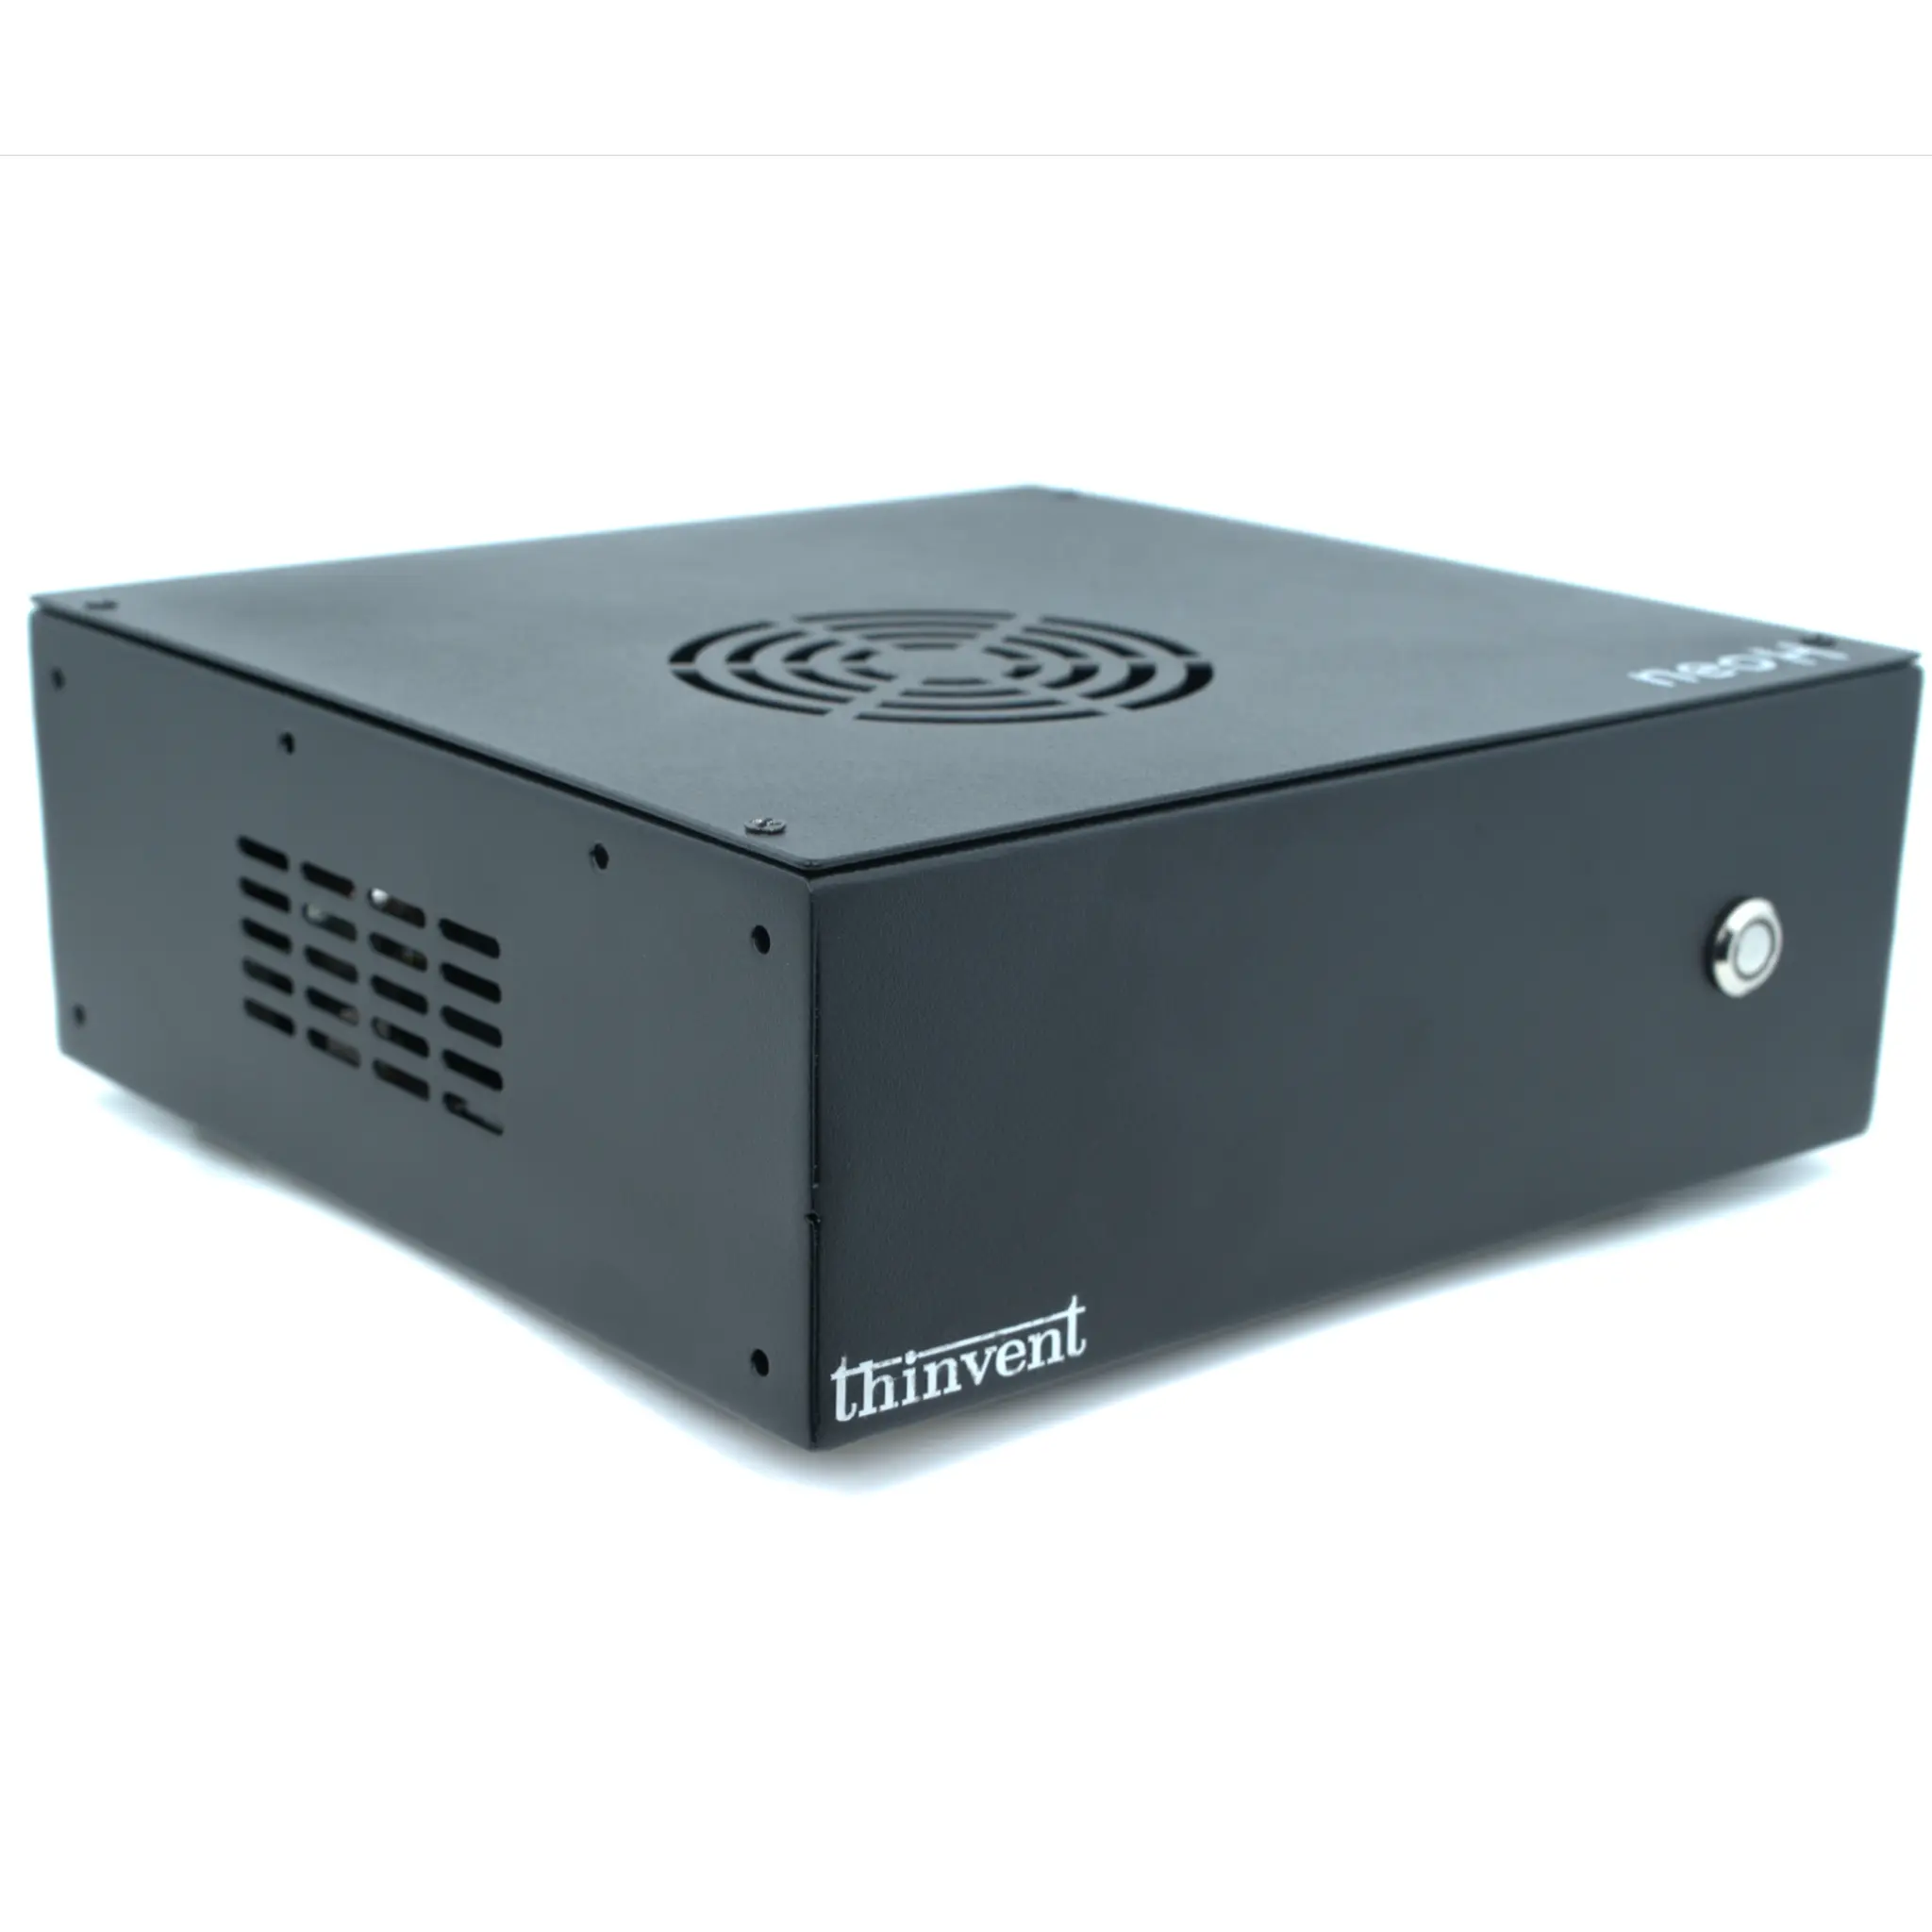
Thinvent builds industrial computers, mini PCs, thin clients, and all-in-one PCs designed for continuous operation in demanding environments. Our industrial PCs support current-generation Intel processors, generous DDR4 memory, and fast SSD storage, with options for Windows 11 Pro, Windows 11 IoT, Linux, or no OS at all — so you can standardise on a hardened, fully patched platform. Fanless chassis options reduce dust ingress and moving-part failures, while multiple Ethernet and serial ports make integration into existing control networks straightforward. For kiosk and signage projects, our all-in-one and thin client ranges offer a compact footprint with the reliability needed for unattended, always-on operation.